

TL;DR: GNU Savannah hosts Bash, Coreutils, and hundreds of other GNU projects. Using Hacktron, we found that an email address like a`touch${IFS}/tmp/savane-rce-proof`@attacker.example gave any registered user code execution on its backend. From there, we made our account a superuser, impersonated Bash’s maintainer, and confirmed we could add an SSH key with push access to the upstream Bash repository. An unpatched kernel gave us root access and access to a GNU backup server. We reported it to the FSF on May 11, 2026.
We then ran Hacktron’s pentest across the rest of Savane to find further bugs and reported those too, bringing the total to 26 confirmed vulnerabilities. The FSF fixed them and published an incident report.
- Regular accountsavannah.gnu.org
- Email addressShell metacharacters allowed
- GPG key testEmail in a shell command
- Web server RCEDatabase access
- SuperuserImpersonate any user
- Bash maintainerAdd SSH keys
- OverlayFSUnpatched kernel
- RootSavannah backend
- Backup serverGNU
Why Savannah
Savannah is where much of the GNU userland lives, including Bash and Coreutils, which provides commands such as ls, cp, and rm. It holds the repositories, the maintainer accounts, and the SSH keys that decide who can push. Code that lands there gets packaged by distributions and installed on millions of machines, and the xz backdoor showed what one compromised link in that chain can do.
Like much of the infrastructure free software depends on, it’s run by a handful of volunteers and FSF staff with limited resources. We wanted to put our resources to work there. Savannah runs Savane, a PHP application that is itself free software, so we pointed Hacktron at the source and audited it.
What came back is probably the most impactful bug we’ve ever found.
The bug: an email address that runs commands
Savane let us register with this email address:
a`touch${IFS}/tmp/savane-rce-proof`@attacker.exampleYou know where this is going, right?
The validator
Savane’s email validator (frontend/php/include/account.php:275) accepts dot-atom addresses with characters like backticks, $, {}, /, and |. Most of these are technically allowed in the local part of an email address by the RFC, so the address above passes validation. Any user can set it at registration or through the email-change flow (frontend/php/my/admin/change.php:271).
The sink
Every logged-in user can manage a GPG key for their account, and Savane offers a “Test GPG keys” button at /my/admin/change.php?item=gpgkey. One of the checks it runs lists key fingerprints for the email address on the account. In frontend/php/include/gpg.php:
function test_gpg_command ($temp_dir, $command, &$ret, $in = null){ $cmd = gpg_name () . " --home '$temp_dir' $command"; ... $res = utils_run_proc ($cmd, $out, $err, $aux); ...}
function test_listing ($temp_dir, $level, &$ret, $test_against_email = false){ ... if ($test_against_email) { $email = user_get_email (0); ... } $options = '--list-keys --fingerprint'; if ($test_against_email) $options .= " $email"; $res = test_gpg_command ($temp_dir, $options, $ret);}The email is appended to $options as plain text, $options is concatenated into $cmd, and utils_run_proc() hands that string to proc_open(). With a string command, PHP runs it through /bin/sh. The shell sees our backticks and runs whatever is between them before gpg even starts. ${IFS} is there because the validator rejects spaces, and the shell expands it to one.
Exploiting it takes four steps:
- Register with the payload above as your email address, or change an existing account’s email address to it. The app accepts it.
- Open
/my/admin/change.php?item=gpgkey. - Paste any GPG key and click “Test GPG keys”.
- The command inside the email runs on the server as the web server user.
The FSF later traced the vulnerable path to the March 7, 2026, release of Savane (3.17-c369). It affected both savannah.gnu.org and savannah.nongnu.org, so the window was about two months.
From a shell to superuser
To see how far it went, we swapped the payload for a reverse shell and landed on the backend as the web server user.
The web server user can read Savane’s configuration, which includes the database credentials, so there was nothing to crack. We set the superuser flag on our own account, harshjaiswal, and reloaded the page.
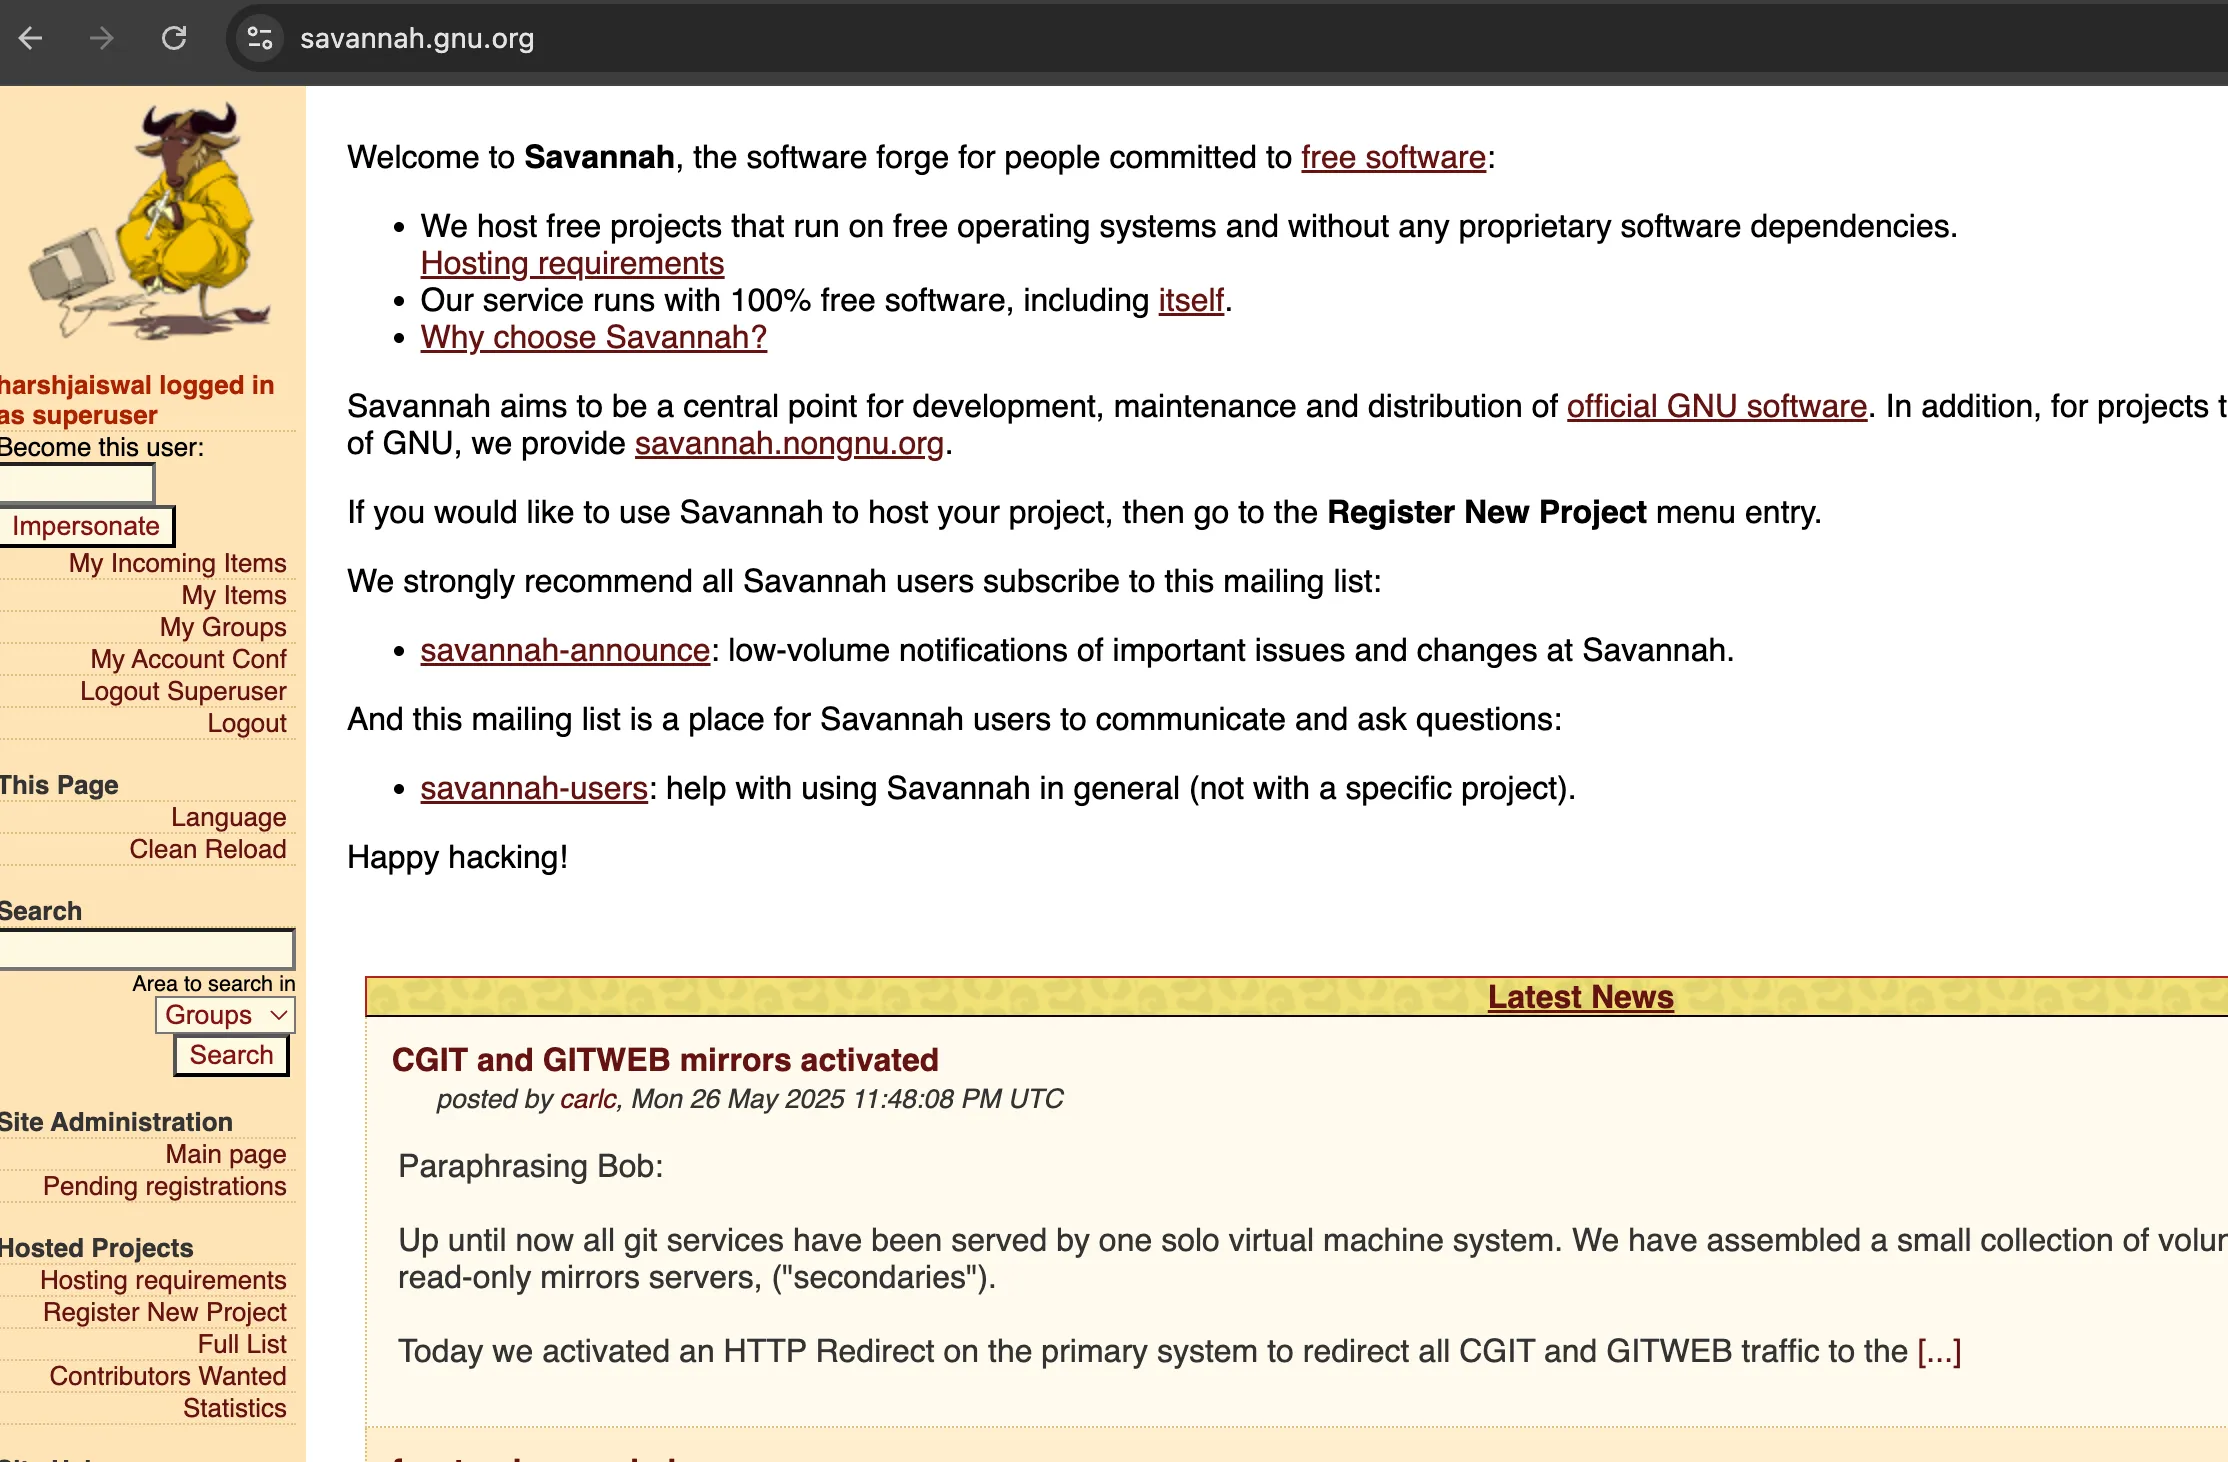
Superusers get a “Become this user” box in the sidebar, which lets a site admin act as any account without its password.
Becoming Bash’s maintainer
We typed chet into that box. Chet Ramey maintains Bash.
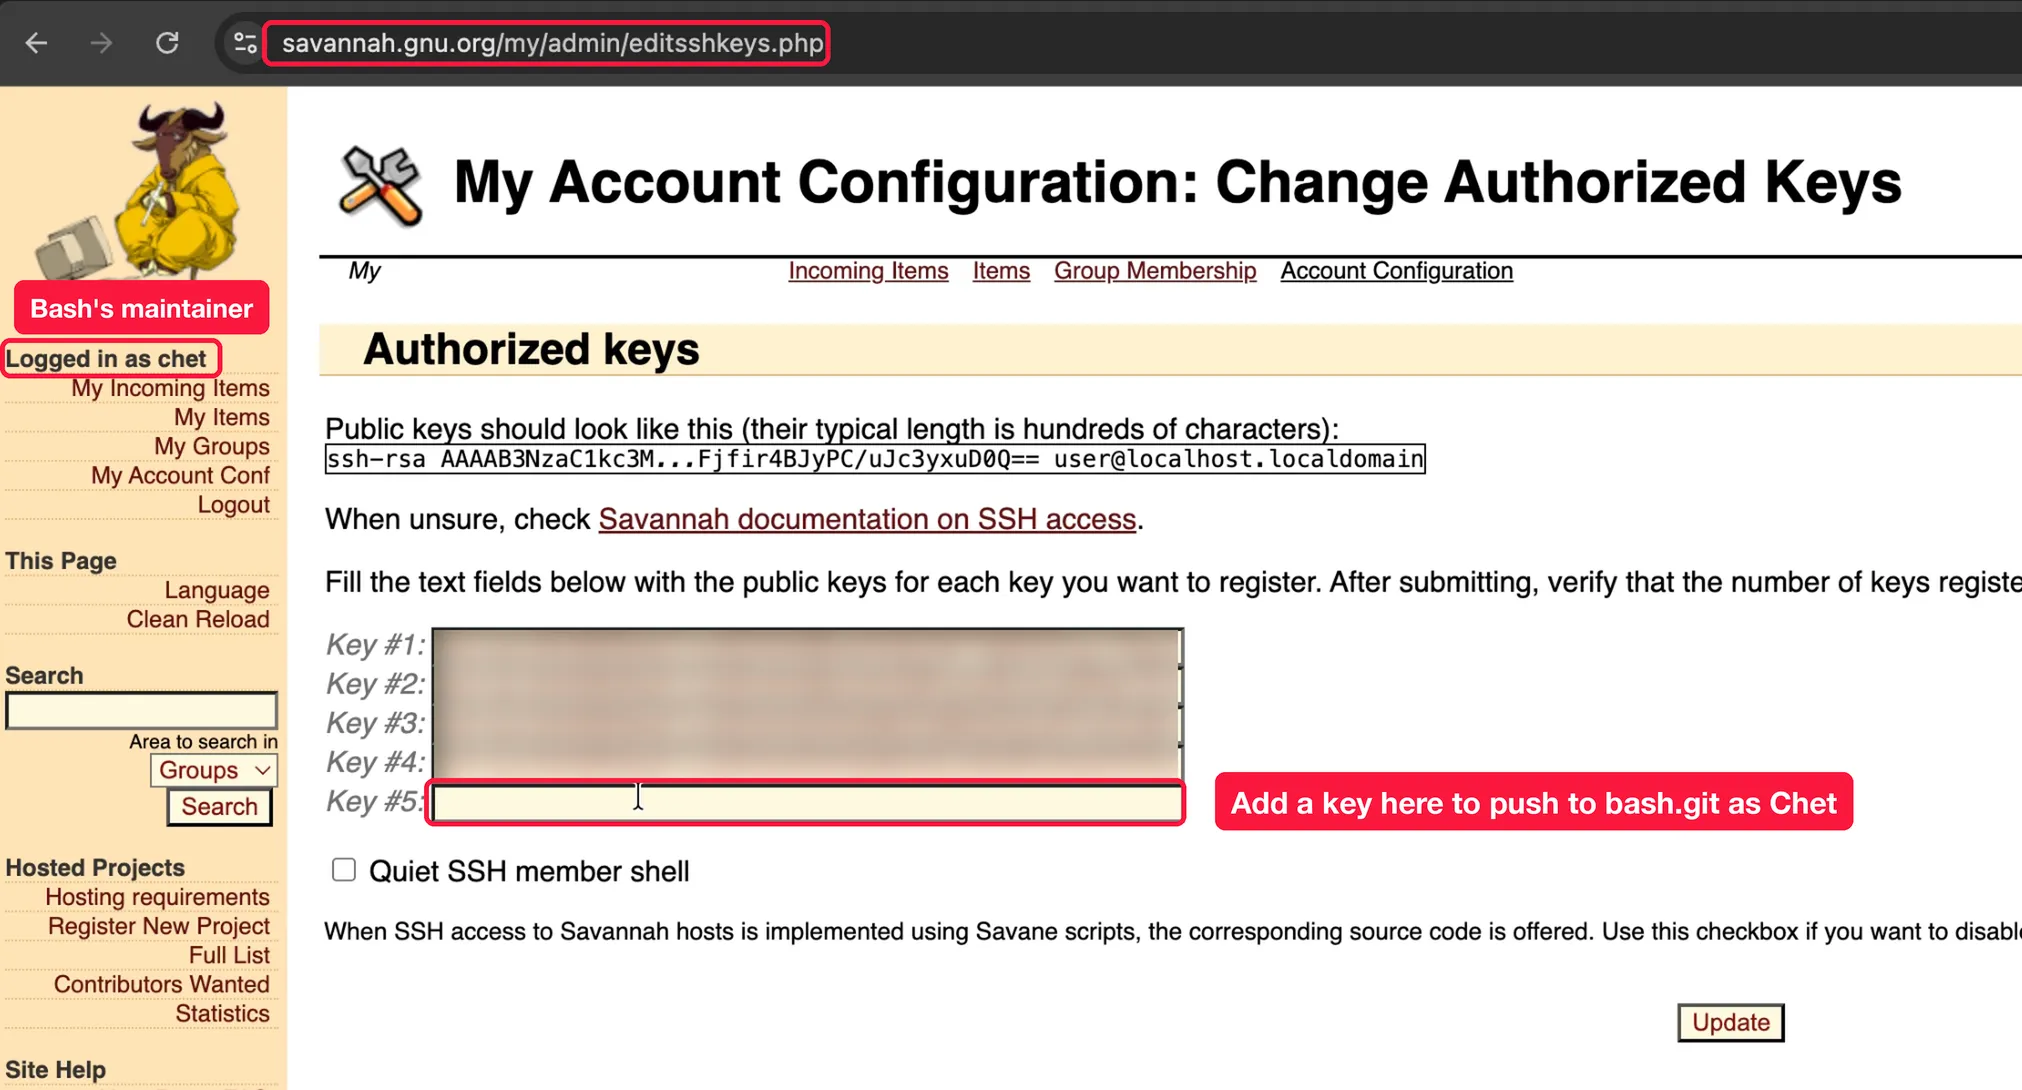
That’s his SSH key page, with an empty slot for one more. Savannah’s Git hosting is keyed off these entries, so adding a key here grants push access to bash.git as the maintainer. We confirmed the page accepted edits and stopped there. We did not add a key and we did not touch the repository.
An attacker in this position could have pushed a commit to upstream Bash under Chet’s name and done the same to Coreutils or any other project on Savannah.
Root and a backup server
The web shell was unprivileged. Savannah runs Trisquel GNU/Linux 11, with a linux-libre kernel built from Ubuntu 22.04’s 5.15 LTS kernel. That kernel was still affected by GameOver(lay), two OverlayFS bugs from 2023 (CVE-2023-2640 and CVE-2023-32629). Canonical fixed the 5.19 and 6.2 kernels back then, but the 5.15 kernel didn’t get a fix until USN-8255-1 on May 7, 2026, four days before our report. The public exploit worked on the first try and gave us root on the Savannah backend.
As root, we found a key that let us SSH to a GNU backup host as the gnubackup user.
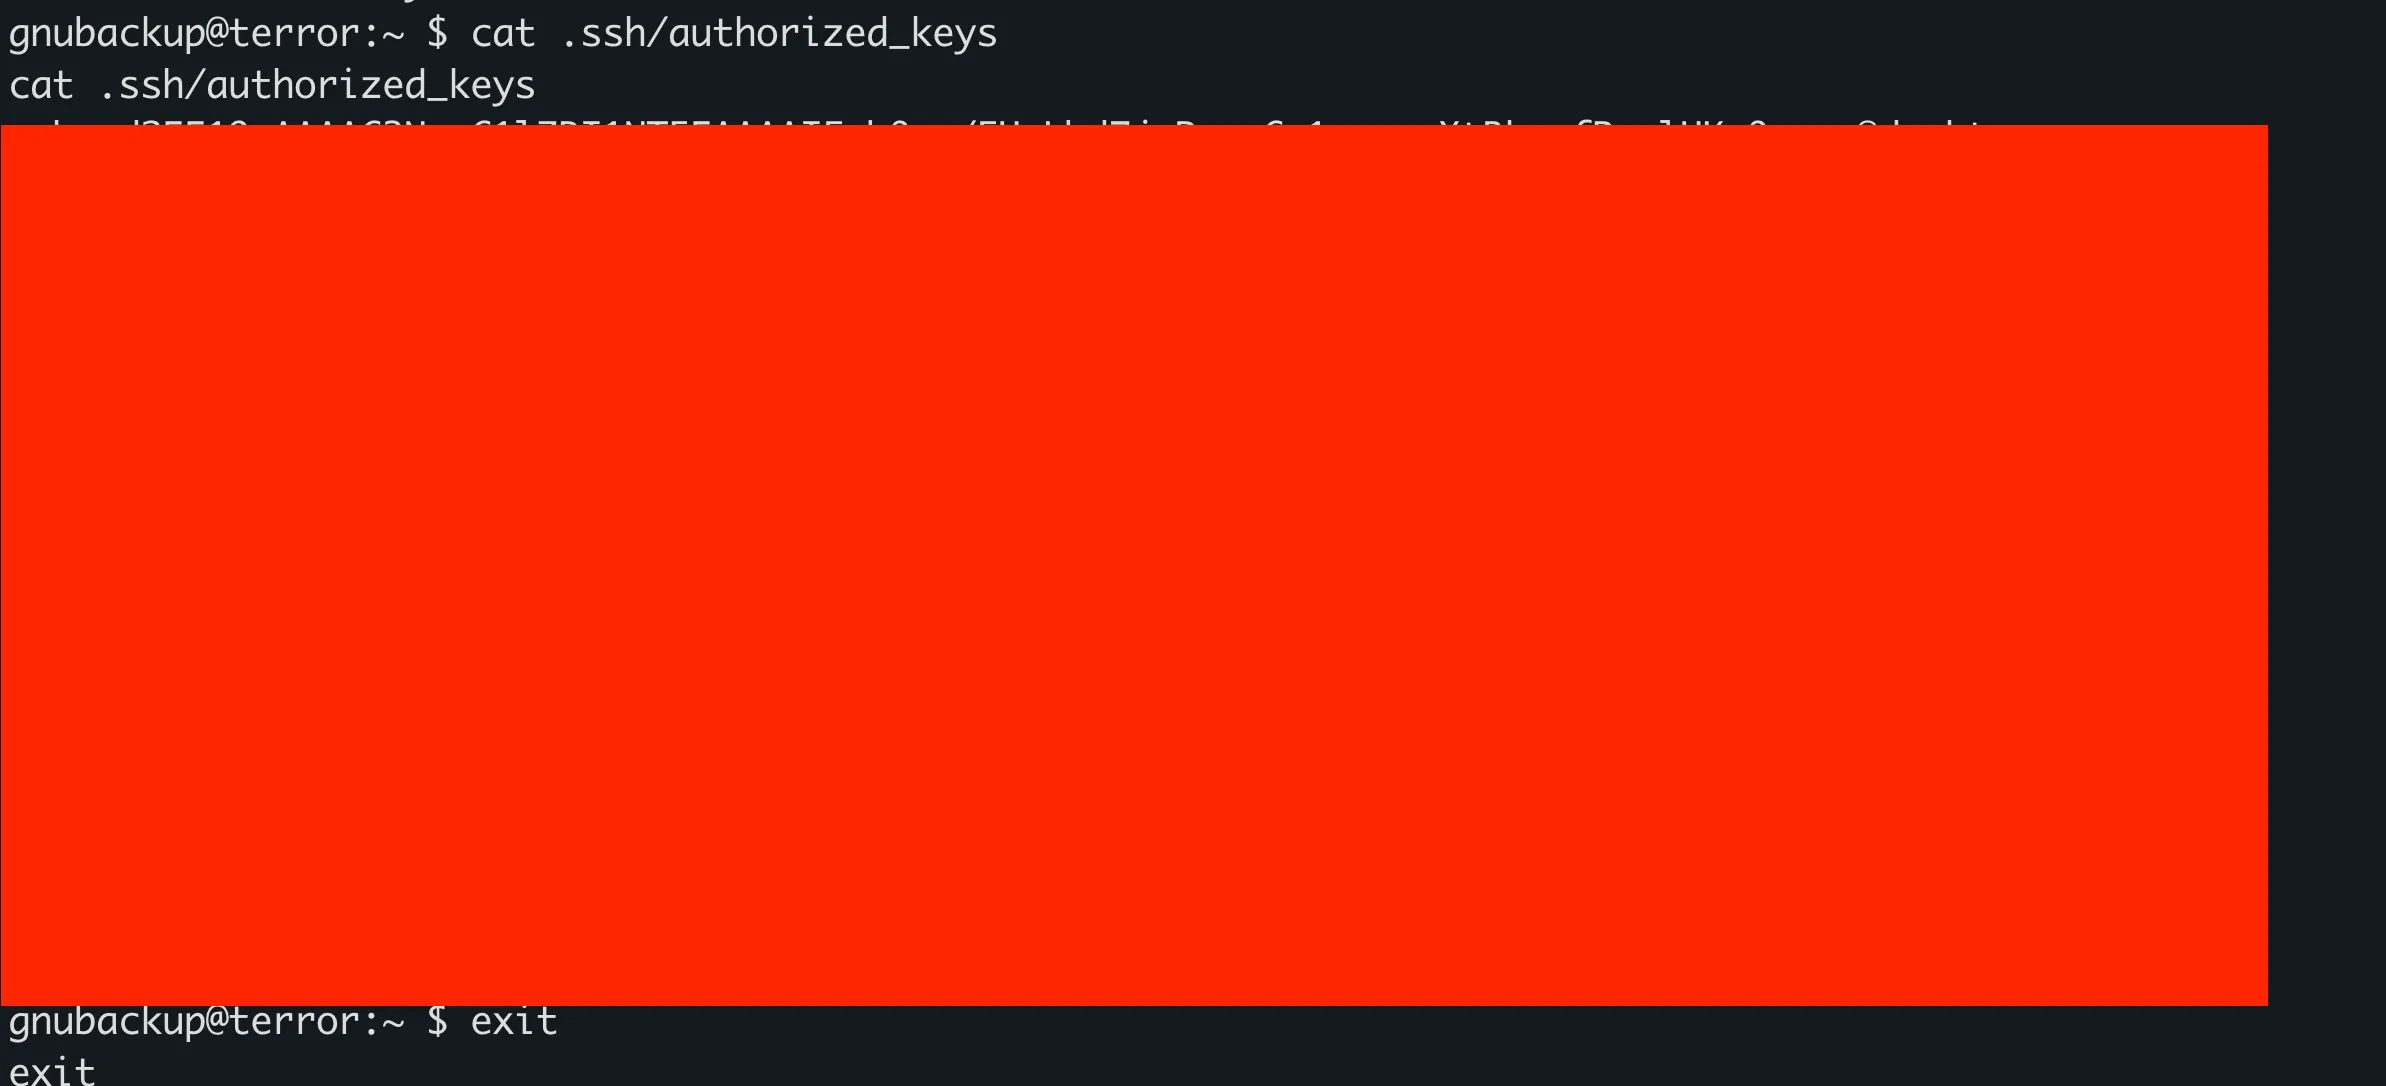
At that point, we had root on the forge, access to its backups, and the ability to act as any maintainer. We stopped doing recon and wrote the report.
The rest of Savane
The RCE was one finding of many. After the initial report, we kept Hacktron running on the Savane codebase, which descends from the 2001 SourceForge code. It produced 33 findings; we threw out 7 false positives and sent the FSF the remaining 26 (2 critical, 6 high, 16 medium, 2 low) with file paths, line numbers, and reproduction steps. The notable ones:
| ID | Severity | Finding |
|---|---|---|
| HCK-001 | Critical | Command injection to RCE through the GPG key test email |
| HCK-002 | Critical | Authorization bypass in site-wide admin group configuration (siteadmin/triggercreation.php) |
| HCK-003 | High | Any group member can delete the group’s mailing lists |
| HCK-004 | High | Any user can change any group’s tracker notification addresses |
| HCK-006 | High | Any group member can reset mailing list admin passwords |
| HCK-008 | High | Private file access trusts a file_uid parameter from the request instead of the session |
| HCK-010 | Medium | Session hijacking: cross-domain SSO passes session_uid and session_hash in the URL |
| HCK-012 | Medium | Password reset and email change confirmation hashes never expire |
| HCK-017 | Medium | Stored XSS through the real name field, which only strips < |
Working with the FSF
Corwin Brust, a Savannah administrator, replied the same night. The FSF treated it as a full compromise: it patched the kernel, audited access controls, databases, and logs, and warned the operator of the other public Savane instance. The authorization bugs were fixed through a refactor rather than individual patches.
Disclosure timeline
| Date | Event |
|---|---|
| 2026-03-07 | Savane 3.17-c369 ships with the vulnerable GPG key path |
| 2026-05-07 | Canonical publishes USN-8255-1, fixing GameOver(lay) in the 5.15 kernel |
| 2026-05-11 | We report RCE, root access, and access to the Bash repository to savannah-hackers-private |
| 2026-05-12 | Corwin Brust, Savannah administrator, acknowledges the report and our 30-day disclosure window |
| 2026-05-14 | FSF installs the fixed kernel and removes our account |
| May 2026 | We send the remaining 25 findings from the full Savane audit |
| 2026-06-19 | FSF publishes a statement on the incident |
| 2026-08-07 | FSF publishes its incident report and the Savane patches |
Thanks to Ineiev, Corwin Brust, and Bob Proulx from the Savannah hackers and the FSF sysops for working with us.
Work with the team behind this research
Hacktron brings together top CTF researchers, experienced red teamers, and offensive security researchers. We use AI to accelerate security research, finding and eliminating vulnerabilities in widely trusted software before malicious actors do. We’re continuing our research across the infrastructure the world depends on. If you’re responsible for securing some of it, we’d like to work with you through red teaming, pentests, or AI code review. Reach out at hello@hacktron.ai.