
Between 16 and 23 October, five major security incidents went public in a single week: two remote code execution bugs in PHP, a memory corruption bug in Google’s Brotli decoder, a chain of four bugs in Plex Media Server, a CVSS 10.0 bug in GitLab, and eight compromised certificate authority keys at eMudhra.
Now that the month is over, here’s what happened next.
At a glance
| Issue | Patch / containment | Exploitation |
|---|---|---|
| PHP2Shell (CVE-2026-109618, CVE-2026-109619) | 21 Oct | Attempt seen 17 Oct, before disclosure; CISA-listed 26 Oct; 24 PAN-OS firewalls rooted (Dream Research) |
| HTTP2Shell / Node2Shell (CVE-2026-111497) | 21 Oct | CISA-listed as exploited 27 Oct; public details of compromises limited. ELLIO’s documented attempt failed in lab replays |
| Plex2Shell (four CVEs) | Early Aug | CISA-listed 20 Oct; active exploitation confirmed by Plex: crypto miners, proxy malware |
| GitLab (CVE-2026-110264) | 21 Oct | No public exploitation reported |
| GitLab (CVE-2026-97229, earlier flaw) | 12 Oct | Exploitation attempts detected by GitLab; Alpine Linux targeted 20–21 Oct; CISA cites ongoing attacks |
| eMudhra CA keys | 17 Oct (blocked) | No malicious use confirmed |
PHP2Shell
Fixed: 21 October, in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Who is affected and how to check: PHP2Shell: Critical PHP RCE (CVE-2026-109618, CVE-2026-109619).
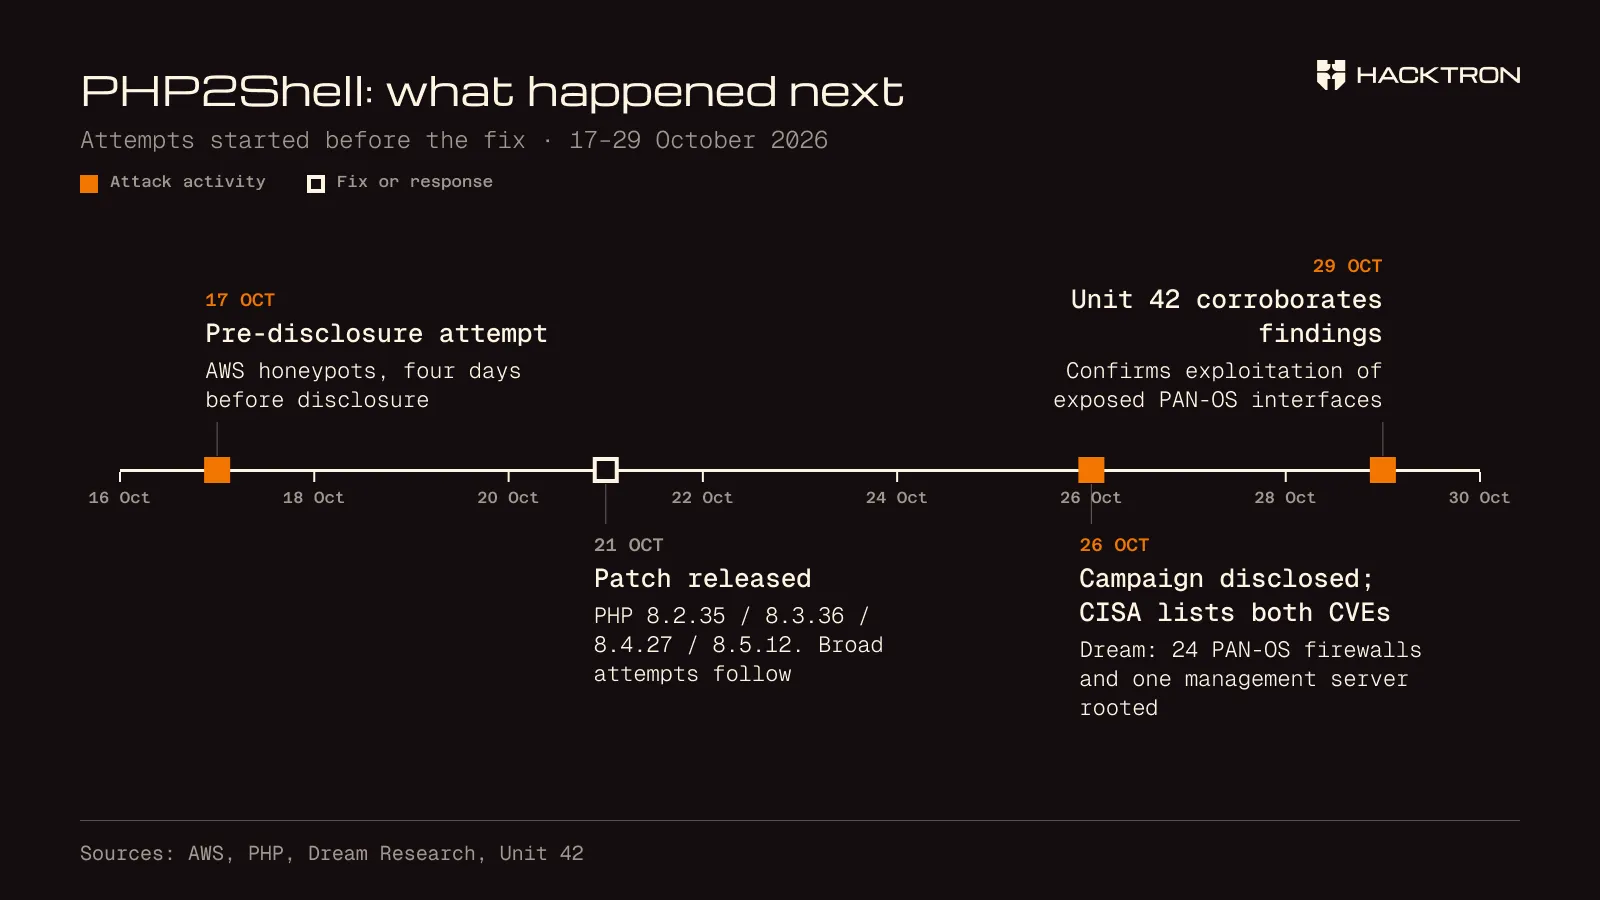
Exploited: yes. Amazon Threat Intelligence recorded an exploitation attempt in its MadPot honeypots on 17 October, four days before public disclosure, and says it’s unclear how the actor got the exploit details that early. After disclosure, AWS reports broad exploitation attempts in the wild. CISA added both CVEs to its Known Exploited Vulnerabilities catalog on 26 October.
Palo Alto Networks’ advisory now says active exploitation has been observed against PAN-OS management interfaces exposed to the internet. On 26 October, Dream Research reported a campaign that chained PHP2Shell with Fragnesia (CVE-2026-46300), a Linux kernel privilege-escalation bug, and rooted 24 PAN-OS firewalls in the US, Japan, Taiwan and South Korea, plus an internal management server. Two of the firewalls belonged to a US government-affiliated organisation. Unit 42 says it independently verified the attacker’s tooling and the reported results. Dream Research found signs of AI-assisted tooling on the attacker’s infrastructure, but says it has no direct evidence AI wrote the exploit.
PHP2Shell is a blind remote memory corruption bug. A proof of concept built for one target rarely works on the next one, because memory layout depends on the PHP build, the extensions loaded and the application in front of it. Code execution needs an exploit tuned to each target.
That doesn’t make the bug overhyped. Attempts are widespread; confirmed successful compromises are much rarer. Wiz says it hasn’t seen a successful end-to-end PHP2Shell exploit in its own telemetry.
php2shell: The exploitability gap between frontier and open models
We measured how long that adaptation takes: frontier models ported the exploit to a new target in hours, while the open models we tested didn't get there. That gap is likely to narrow.
Read the postA separate PHP issue is still open. On 23 October, PHP published an advisory for CVE-2026-115560, another possible remote code execution path through session upload progress. It needs an unusual configuration: a non-default session serializer in server settings that the application switches back at runtime with ini_set() before session_start(). The 21 October releases don’t fix it, and no fix release is out yet. PHP’s mitigation for affected configurations is to set session.upload_progress.enabled=0 at the server level. No exploitation has been reported.
The attacks a vendor has confirmed so far are against firewall management interfaces. Most people don’t think of their firewall as a PHP server, but its management interface runs PHP under the hood.
HTTP2Shell / Node2Shell (Brotli)
Fixed: 21 October, in Brotli 1.2.1, 1.1.1 and 1.0.10, and in Node.js 26.12.1, 24.22.1 and 22.23.4. Fixes are still landing in software that bundles its own copy of Brotli. Linux distributions may backport the fix under older-looking version numbers, so check your distro’s security tracker rather than the version string alone.
Exploited: CISA added CVE-2026-111497 to its Known Exploited Vulnerabilities catalog on 27 October, citing evidence of active exploitation. Public details of successful compromises remain limited.
On 26 October, threat-intelligence firm ELLIO documented an exploitation attempt involving a Brotli-compressed request targeting Node.js 24.22.0 on x86-64. When ELLIO replayed the attacker’s chain in its lab, the final stage failed in all 50 attempts. The same source IP had been associated with PHP2Shell activity in OffSeq’s honeypots the week before.
The bug isn’t limited to Node.js. On 25 October, Microsoft shipped out-of-band .NET updates (8.0.33, 9.0.22 and 10.0.14) for the same flaw in .NET’s use of Brotli; request and automatic response decompression are off by default, and self-contained apps and containers carry their own runtime, so they need rebuilding. On 28 October, AWS published a bulletin saying its .NET and Node.js Lambda runtimes are affected, along with App Runner, CodeBuild curated images and other services. Updated Lambda container base images are already available. For functions deployed as ZIP files, AWS rolled out runtime updates in phases, scheduled to finish by 30 October for Node.js and 31 October for .NET, so check that your functions picked up the update. A real code or configuration change picks up the patched runtime sooner once it’s available in your region; AWS notes that “a zero-change update is not sufficient.”
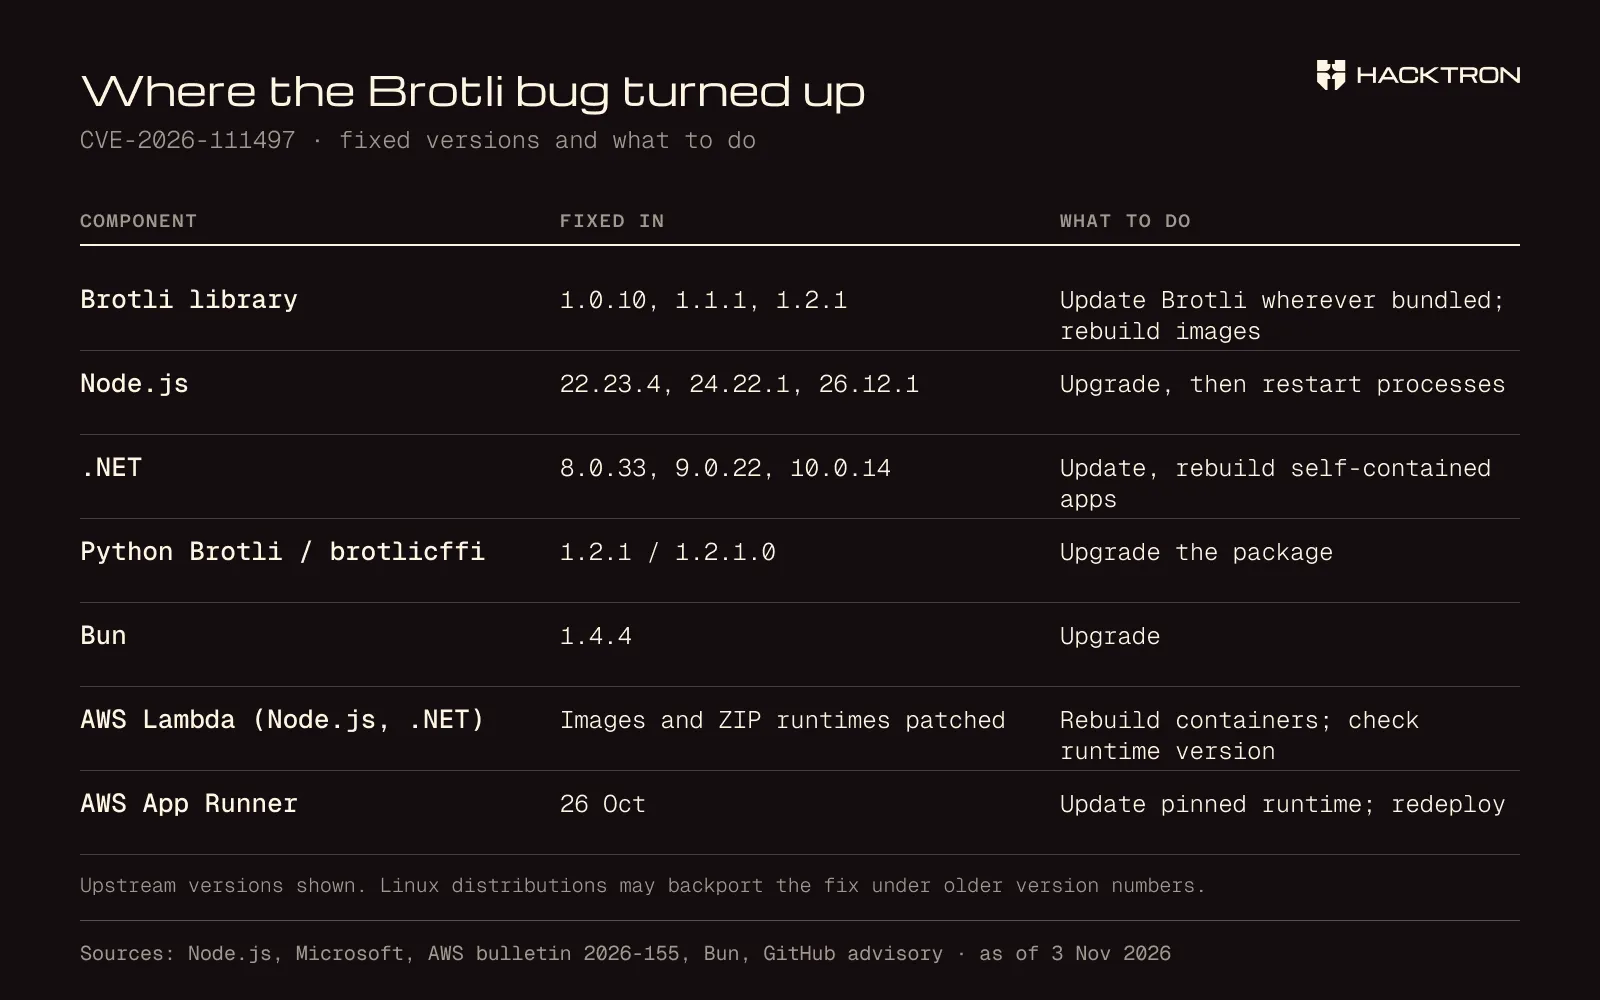
Brotli is hard to fingerprint from the outside. A server doesn’t announce which decoder it uses, and the bug only matters if something decodes attacker-controlled Brotli data: request bodies, or responses fetched from a server the attacker controls.
We covered the bug and the exploit path in more detail in Node2Shell: Brotli Decoder RCE in Node.js (CVE-2026-111497).
Plex2Shell
Fixed: Plex fixed the issue in version 1.43.3.10861, released in early August.
Exploited: yes, from about a day after the 16 October write-up. A researcher’s honeypot recorded attacks on 17 October that installed an XMRig-based crypto miner and proxy software, and Plex has confirmed active exploitation. No one has published a count of compromised servers. CISA added all four CVEs to its Known Exploited Vulnerabilities catalog on 20 October.
This is the only one of the five where the fix was out for more than two months before the attacks. Plex Media Server mostly runs on home and small-office machines, often exposed for remote streaming, and often not updated until something breaks.
GitLab (CVE-2026-110264)
Fixed: 21 October, in 19.5.1, 19.4.3 and 19.3.6, with backports to four older branches. GitLab.com and GitLab Dedicated were patched before disclosure.
Exploited: no public exploitation reported for this flaw. The bug was in the Ruby regular expression engine GitLab ships, not in GitLab’s own code.
An earlier GitLab flaw in the same family is under attack. GitLab says it has detected exploitation attempts against CVE-2026-97229, fixed on 12 October, and has published detection rules. Shadowserver tracks nearly 2,800 internet-exposed GitLab Community Edition instances, though it hasn’t said how many are patched.
The best-documented case is Alpine Linux, whose GitLab instance was targeted on 20 and 21 October. Alpine found no evidence the attacker succeeded but couldn’t rule it out, so it rebuilt the instance, reset all passwords and replaced GitLab’s secret keys. Alpine had two patching misses. Before the attack, it upgraded to GitLab 19.3.4 instead of the patched 19.3.5 by mistake. Then its upgrade to 19.3.6 on 22 October, after the attempts, still didn’t close the path: the fix is a patch to Ruby that GitLab only applies in its official packages, and Alpine’s image used standard Ruby.
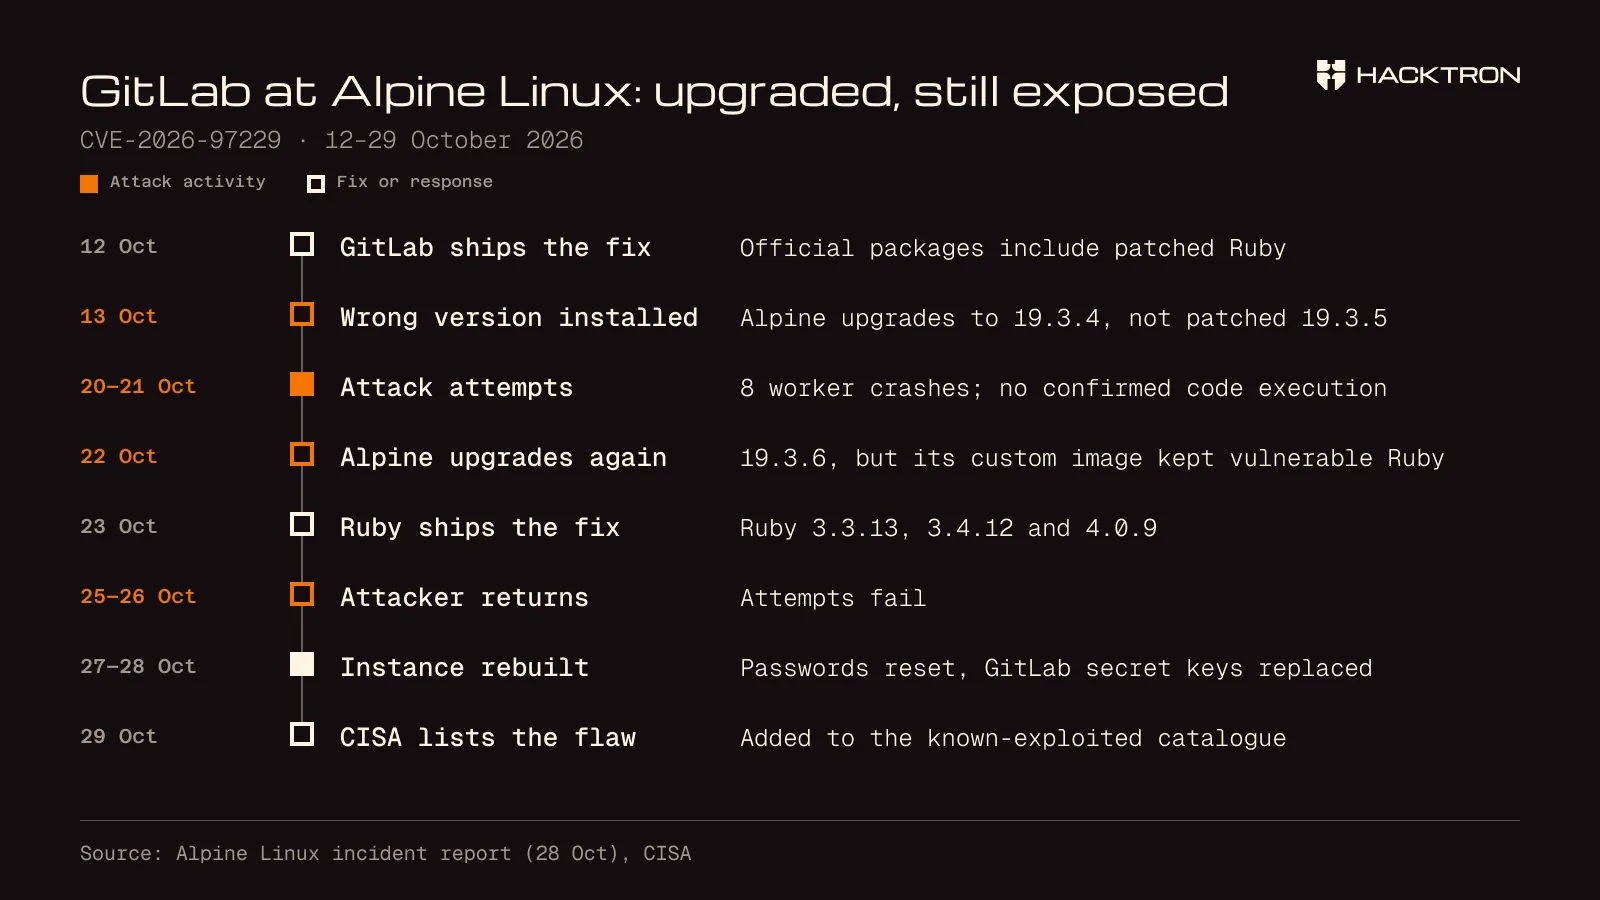
If you self-host GitLab and haven’t upgraded, do it now. A successful exploit could expose repositories and CI/CD secrets accessible to the GitLab service account.
eMudhra
Fixed: Chrome blocked the eight affected keys within two hours of the 17 October report, and other browsers and runtimes followed. Chrome stopped trusting the affected eMudhra root certificate on 27 October.
Exploited: no public exploitation reported. Google says no website certificates from the affected intermediates had appeared in Certificate Transparency logs before the block, and eMudhra says it isn’t aware of any evidence the weak keys were recovered or exploited before disclosure. eMudhra’s board decided on 22 October to leave the global TLS certificate business.
If you have certificates chained to the eMudhra root, they need replacing with another CA.
Is there a pattern?
The PHP2Shell attacks a vendor has confirmed are on firewall appliances. Plex2Shell’s are self-hosted media servers with a fix from two months prior. ELLIO’s publicly documented Brotli exploit attempt was built for a specific Node.js build. In each case, the vulnerable code sits inside something people don’t think of as theirs to patch such as a vendor’s appliance, a bundled runtime, or a container base image.
Those are also the copies a version scan tends to miss. Brotli is compiled into runtimes and libraries that don’t list it as a dependency. GitLab’s fixes are in the Ruby it ships, which is why Alpine’s upgraded instance stayed vulnerable. And as of 28 October, the Dutch National Cyber Security Centre was tracking 757 products for PHP2Shell, with 218 confirmed vulnerable, 144 fixed and 354 still under investigation.
A patch existing doesn’t mean systems are patched. Wiz’s telemetry shows the number of internet-exposed machines vulnerable to PHP2Shell fell about 67% in the first week, but nearly half of the organisations originally affected were still vulnerable a week after disclosure. The remaining risk is in the copies you may not have realised you need to update. Check what’s actually running across your environment, and look for signs of exploitation that may have happened before you patched.
Get hacked on your terms. Talk to the researchers behind Hacktron about continuous red teaming across your whole attack surface.
Sources
- CISA: critical vulnerabilities in PHP require immediate patching
- AWS: PHP2Shell exploitation prior to public disclosure
- Palo Alto Networks advisory: CVE-2026-109618
- Unit 42 threat brief: CVE-2026-109618 and CVE-2026-109619
- OffSeq: PHP2Shell, the first 48 hours
- ELLIO: Node2Shell analysis
- SecurityAffairs on Plex2Shell
- eMudhra statement
- Dream Research: chained PHP2Shell exploit roots 25 servers
- Alpine Linux: GitLab security incident (CVE-2026-97229)
- THN: CISA adds actively exploited GitLab RCE to KEV
- BleepingComputer: hackers now exploiting max severity GitLab flaw
- Wiz: PHP2Shell exploitation attempts and remediation trends
- NCSC-NL: PHP2Shell operational information
- Tenable: PHP2Shell one week later
- Check Point on HTTP2Shell
- Node.js October 2026 security releases
- Microsoft: .NET October 2026 out-of-band security updates
- AWS security bulletin 2026-155-AWS: Brotli
- PHP CVE-2026-115560 advisory
- Secure.com on Plex2Shell
- GitLab patch release 19.5.1
- Google on eMudhra
- THN: eMudhra to exit global SSL/TLS business