Skip to content
Hacktron Sign in [S]
Select example:

Hacktron Whitebox

Hacktron Whitebox delivers white-box penetration tests. It starts from your source code to map the architecture, trace data flows and model threats, and adds dynamic testing against your deployed app when you include it.

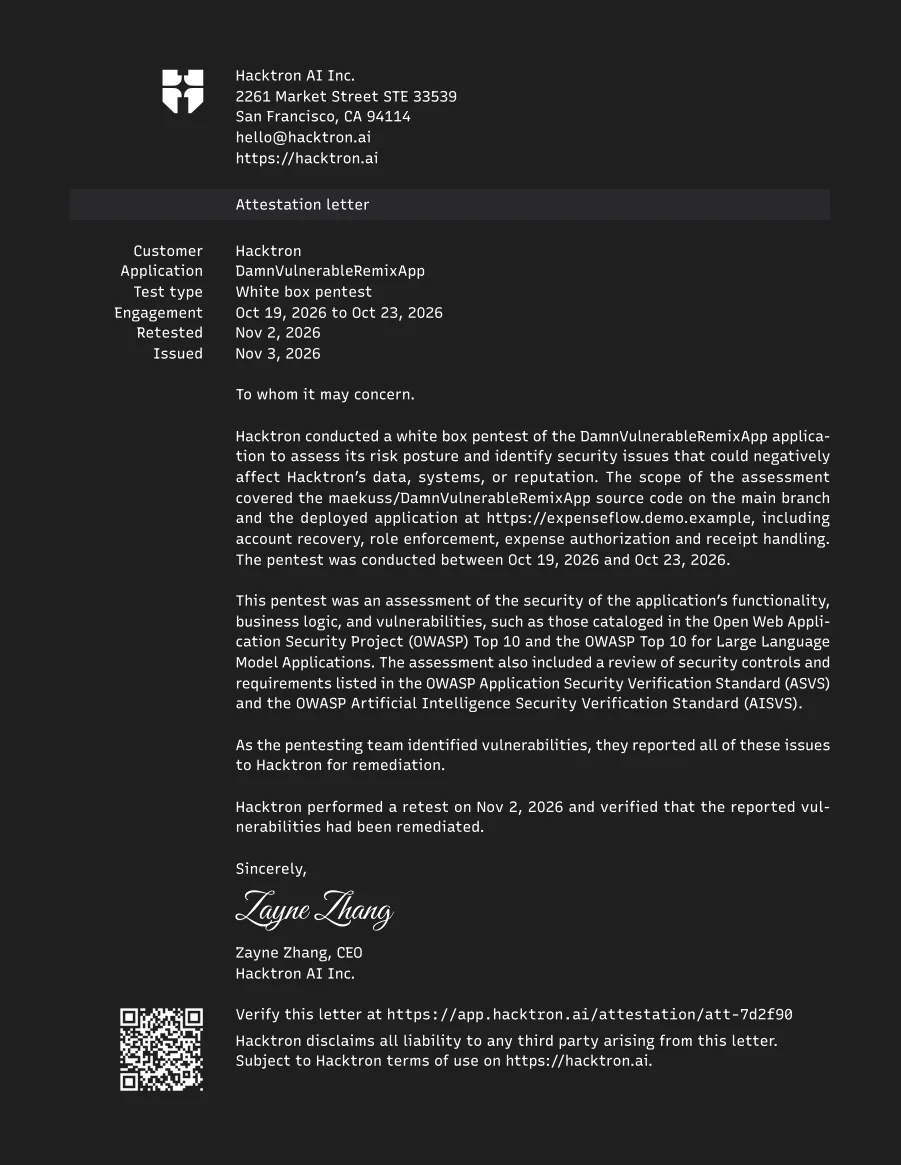
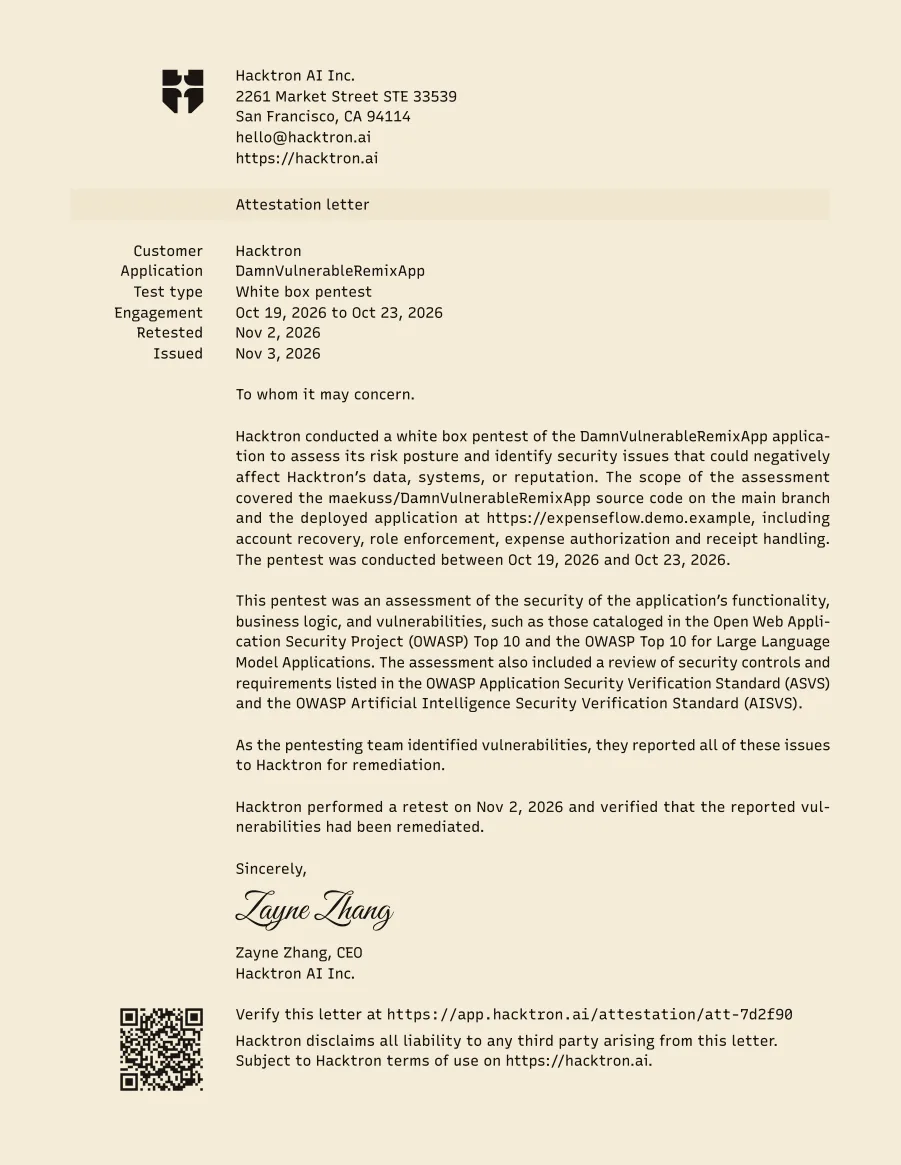
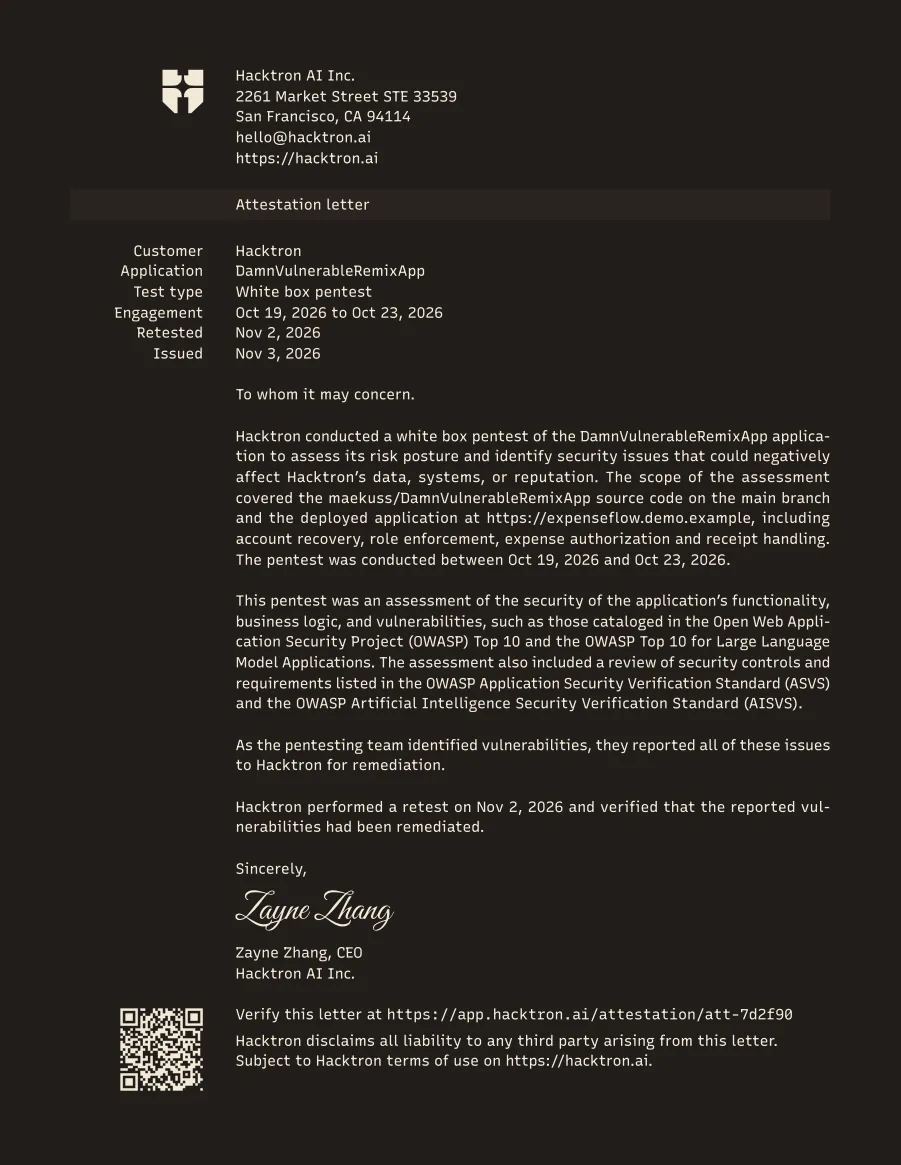
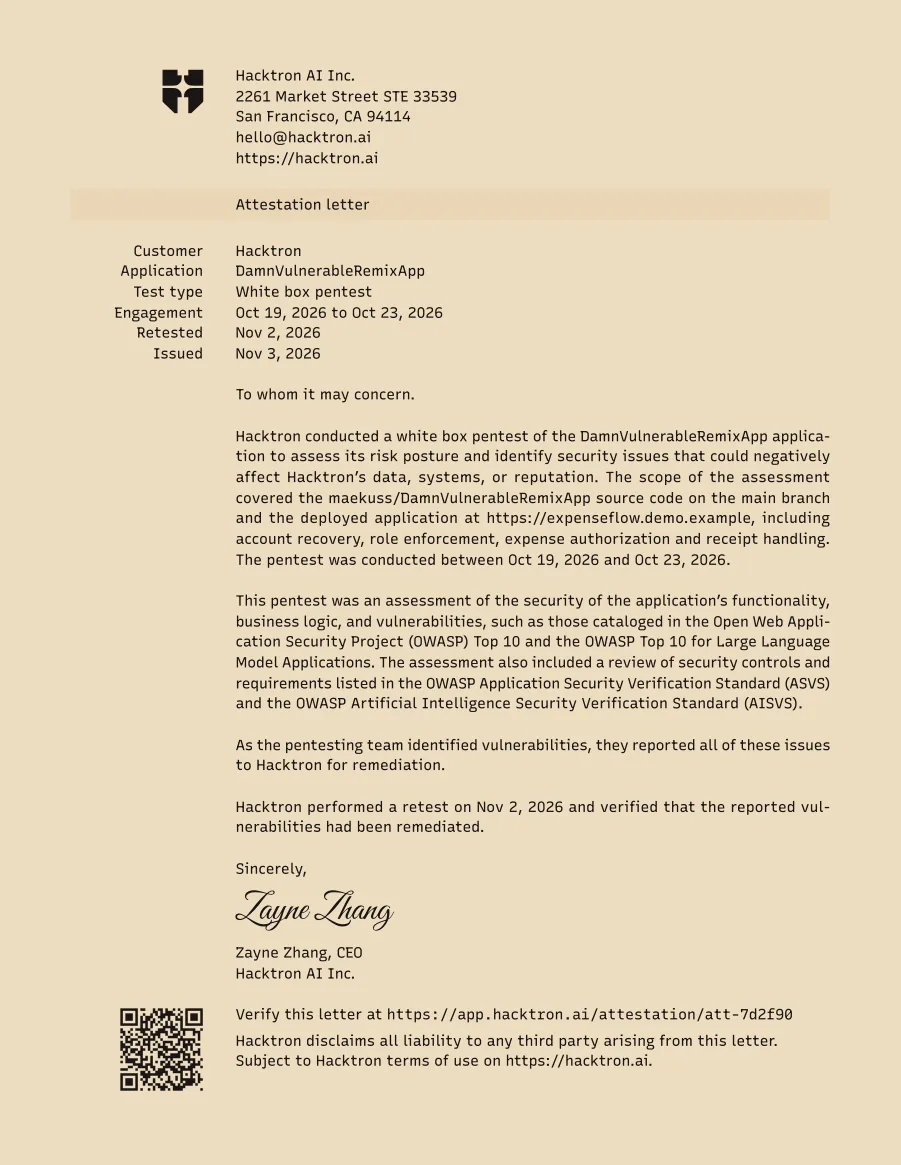
You see the price first, then get researcher-reviewed findings with remediation guidance, technical and executive reports for SOC 2 or ISO 27001, an attestation letter and a retest to check your fixes.

Book a demo or start a pentest.

Scope

One application, from its source code to its deployed app.

CodeA connected repository, a publicURL or an archive.RevisionA branch, tag or commit.ScopeThe whole repository, or thefolders you pick.Dynamic testingOptional. Your app’s URL and testsign-in steps.ContextOptional. Architecture notes or athreat model.EstimatePentest startsCodeA connected repository, apublic URL or an archive.RevisionA branch, tag or commit.ScopeThe whole repository, or thefolders you pick.Dynamic testingOptional. Your app’s URL andtest sign-in steps.ContextOptional. Architecture notesor a threat model.EstimatePentest startsCodeA connected repository, apublic URL or an archive.RevisionA branch, tag or commit.ScopeThe whole repository, or thefolders you pick.Dynamic testingOptional. Your app’s URL andtest sign-in steps.ContextOptional. Architecture notesor a threat model.EstimatePentest startsCodeA connected repository, apublic URL or an archive.RevisionA branch, tag or commit.ScopeThe whole repository, or thefolders you pick.Dynamic testingOptional. Your app’s URL andtest sign-in steps.ContextOptional. Architecture notesor a threat model.EstimatePentest startsCodeA connected repository, apublic URL or an archive.RevisionA branch, tag or commit.ScopeThe whole repository, or thefolders you pick.Dynamic testingOptional. Your app’s URL andtest sign-in steps.ContextOptional. Architecture notesor a threat model.EstimatePentest startsCodeA connected repository, a public URLor an archive.RevisionA branch, tag or commit.ScopeThe whole repository, or the foldersyou pick.Dynamic testingOptional. Your app’s URL and testsign-in steps.ContextOptional. Architecture notes or athreat model.EstimatePentest startsCodeA connected repository, a public URLor an archive.RevisionA branch, tag or commit.ScopeThe whole repository, or the foldersyou pick.Dynamic testingOptional. Your app’s URL and testsign-in steps.ContextOptional. Architecture notes or athreat model.EstimatePentest startsCodeA connected repository, a public URL or an archive.RevisionA branch, tag or commit.ScopeThe whole repository, or the folders you pick.Dynamic testingOptional. Your app’s URL and test sign-in steps.ContextOptional. Architecture notes or a threat model.EstimatePentest startsCodeA connected repository, a public URL or an archive.RevisionA branch, tag or commit.ScopeThe whole repository, or the folders you pick.Dynamic testingOptional. Your app’s URL and test sign-in steps.ContextOptional. Architecture notes or a threat model.EstimatePentest startsCodeA connected repository, a public URL or an archive.RevisionA branch, tag or commit.ScopeThe whole repository, or the folders you pick.Dynamic testingOptional. Your app’s URL and test sign-in steps.ContextOptional. Architecture notes or a threat model.EstimatePentest starts

Testing

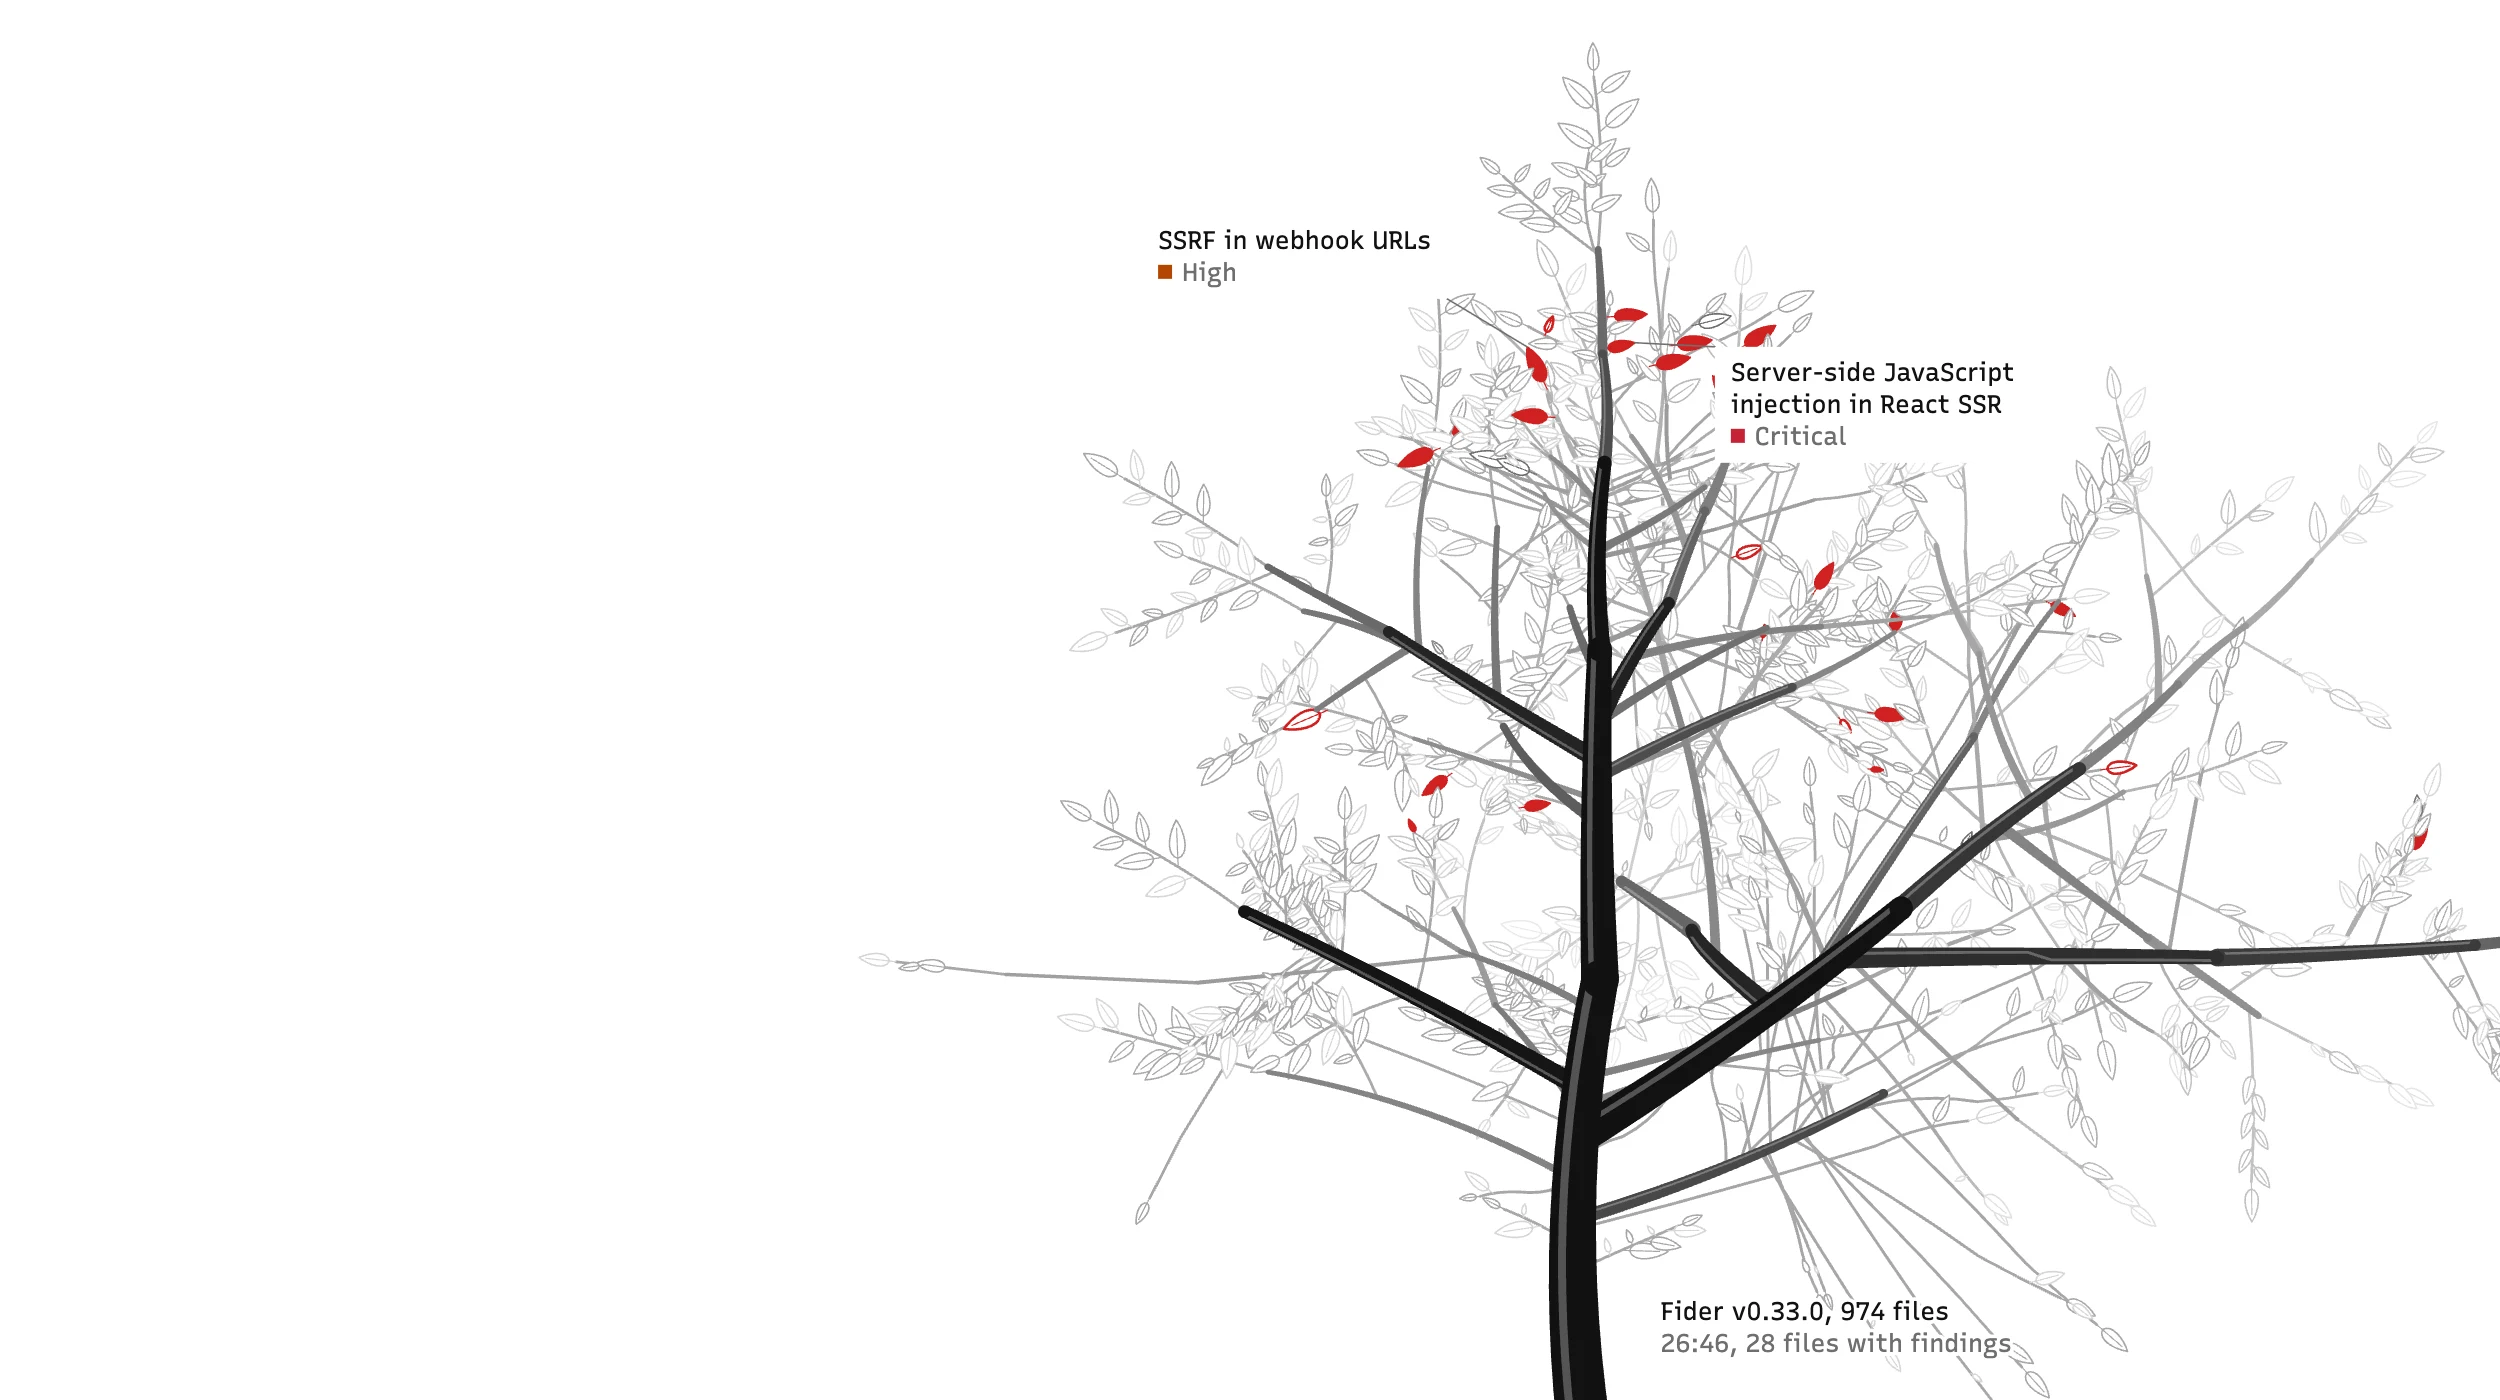
Agents read the application and trace untrusted input from where it enters to where it is used. Each candidate finding is checked against the code, and against the deployed app when dynamic testing is on, then confirmed or dismissed with the reason. Security researchers validate findings and deliver reproducible issues with remediation guidance.

Setting up and reading the code60 agents checking files26:46Setting up and reading the code60 agents checking files26:46Setting up and reading the code60 agents checking files26:46Setting up and reading the code60 agents checking files26:46Setting up and reading the code60 agents checking files26:46Setting up and reading the code60 agents checking files26:46Setting up and reading the code60 agents checking files26:46Setting up and reading the code60 agents checking files26:46Setting up and reading the code60 agents checking files26:46Setting up and reading the code60 agents checking files26:46

Reporting

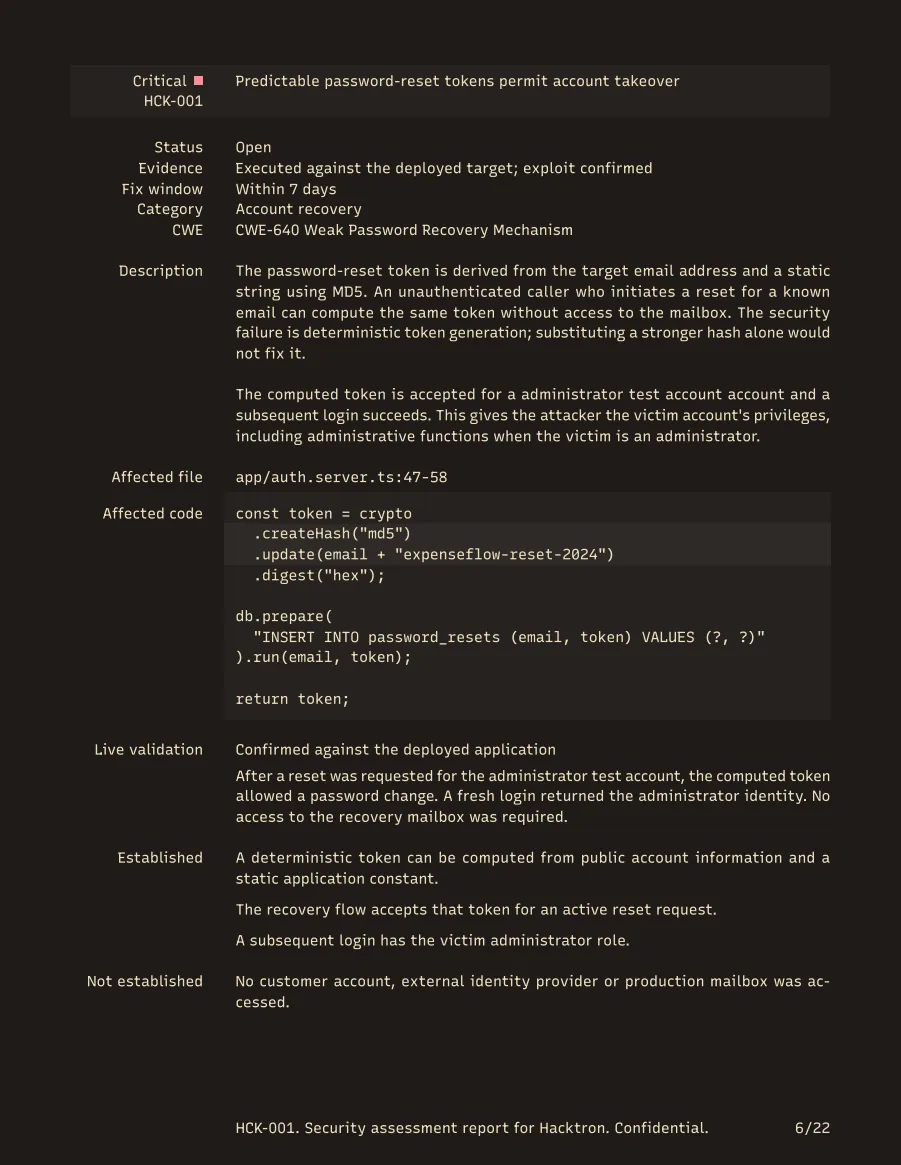
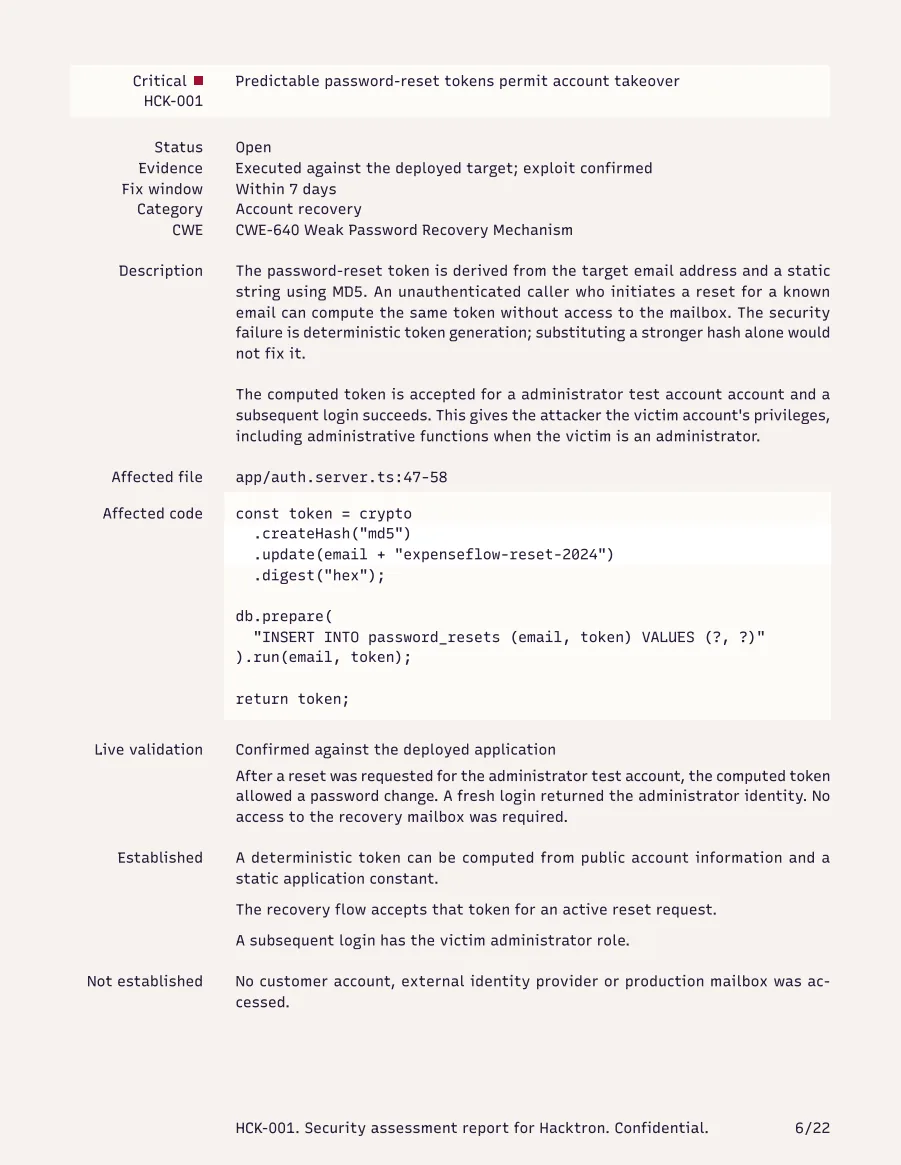
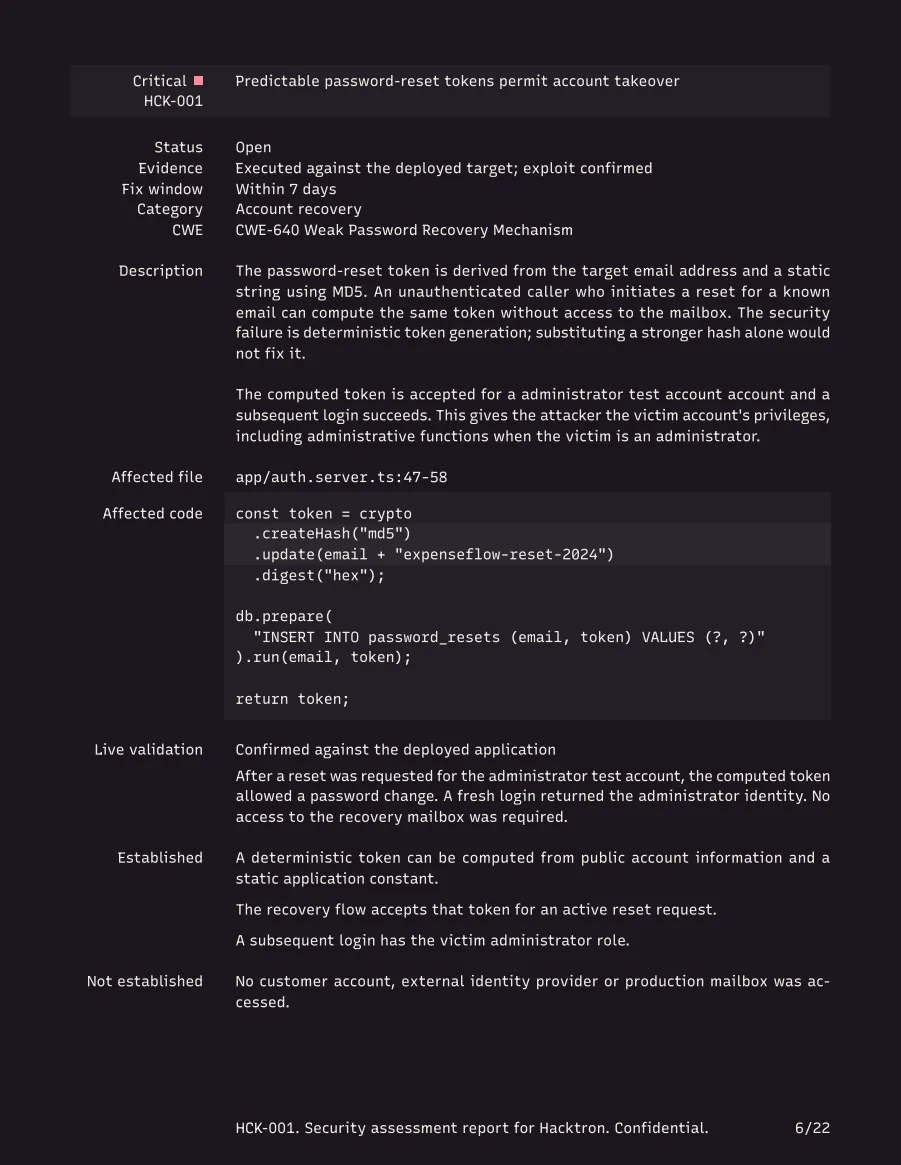
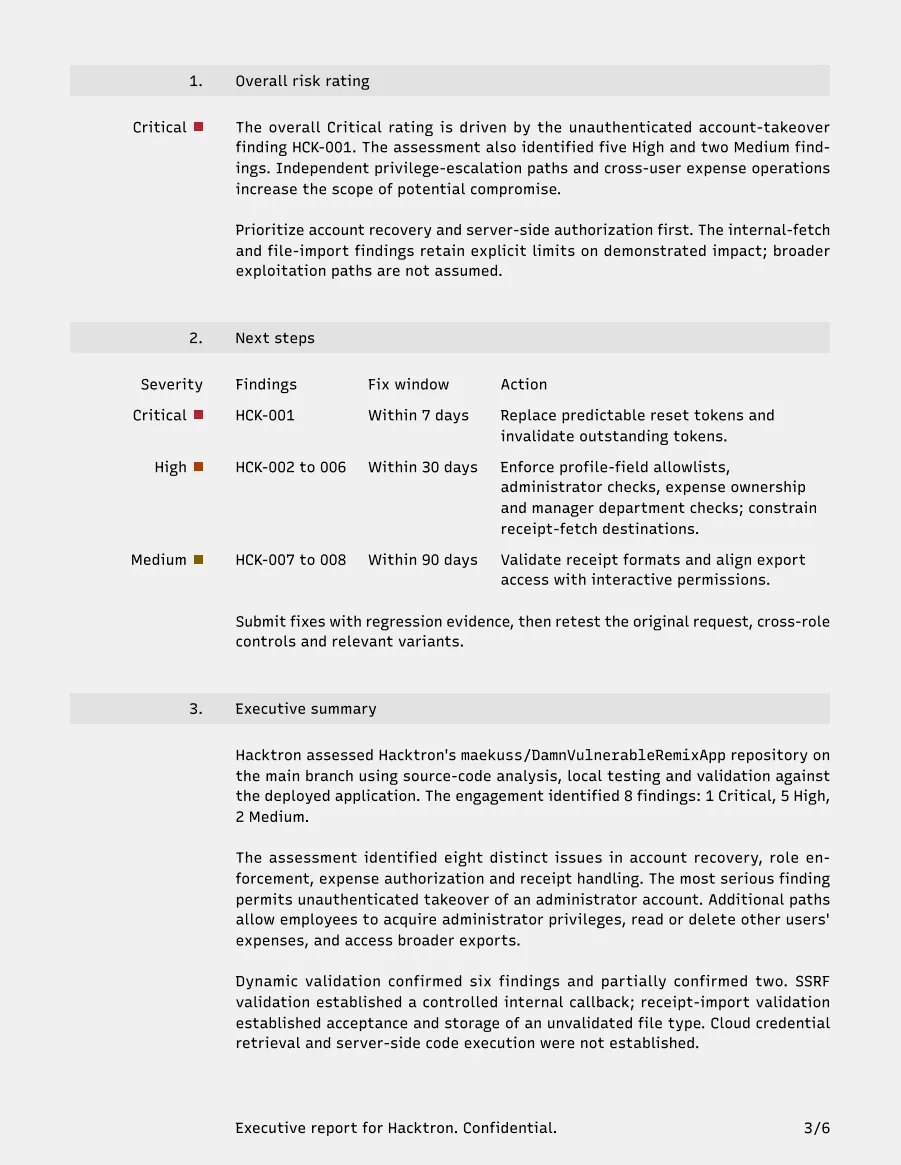
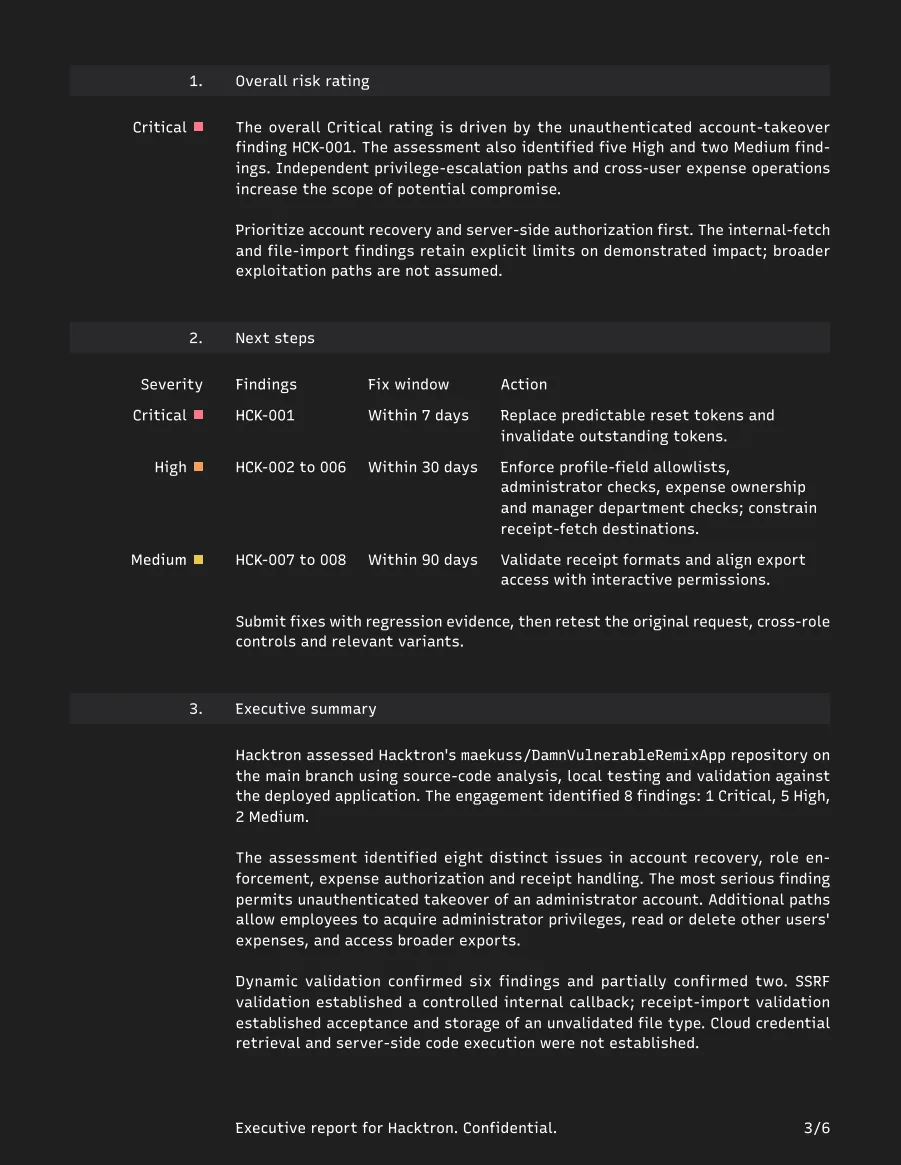
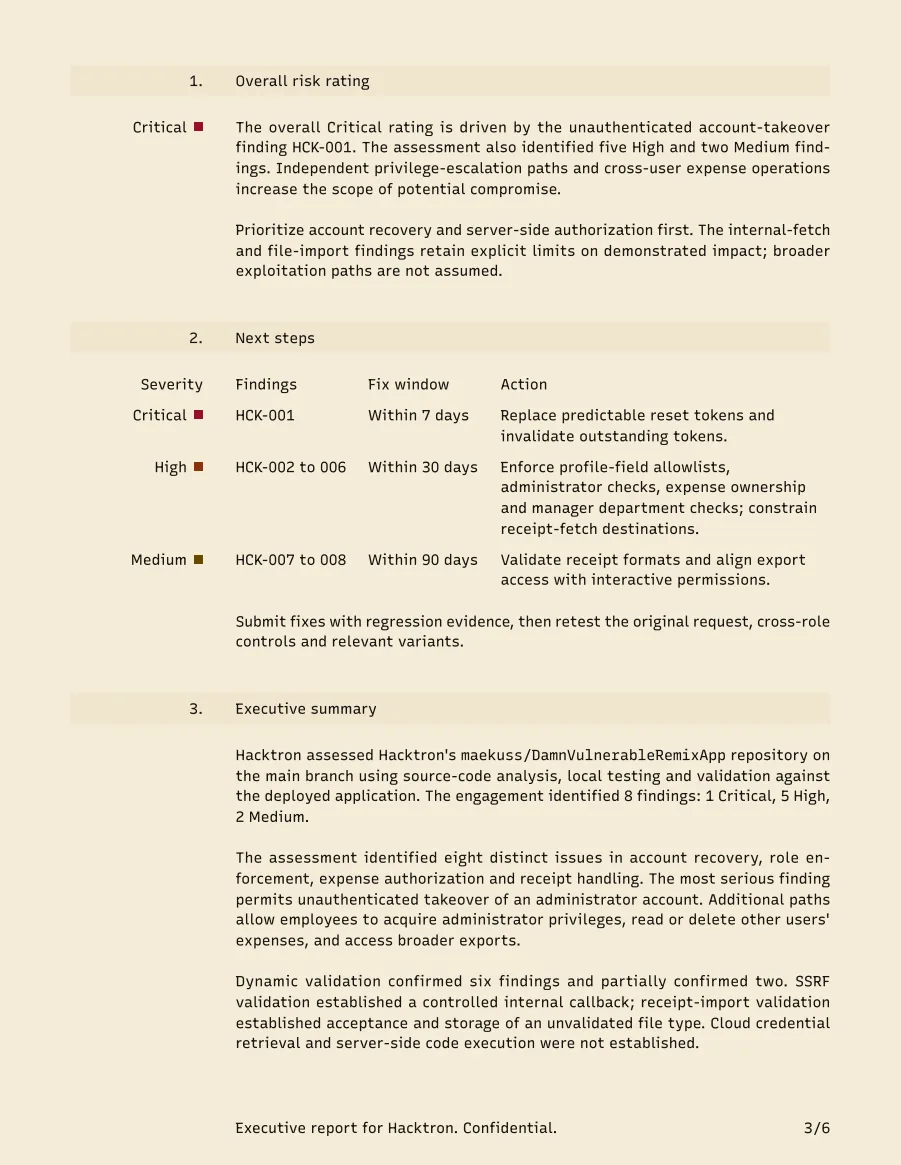
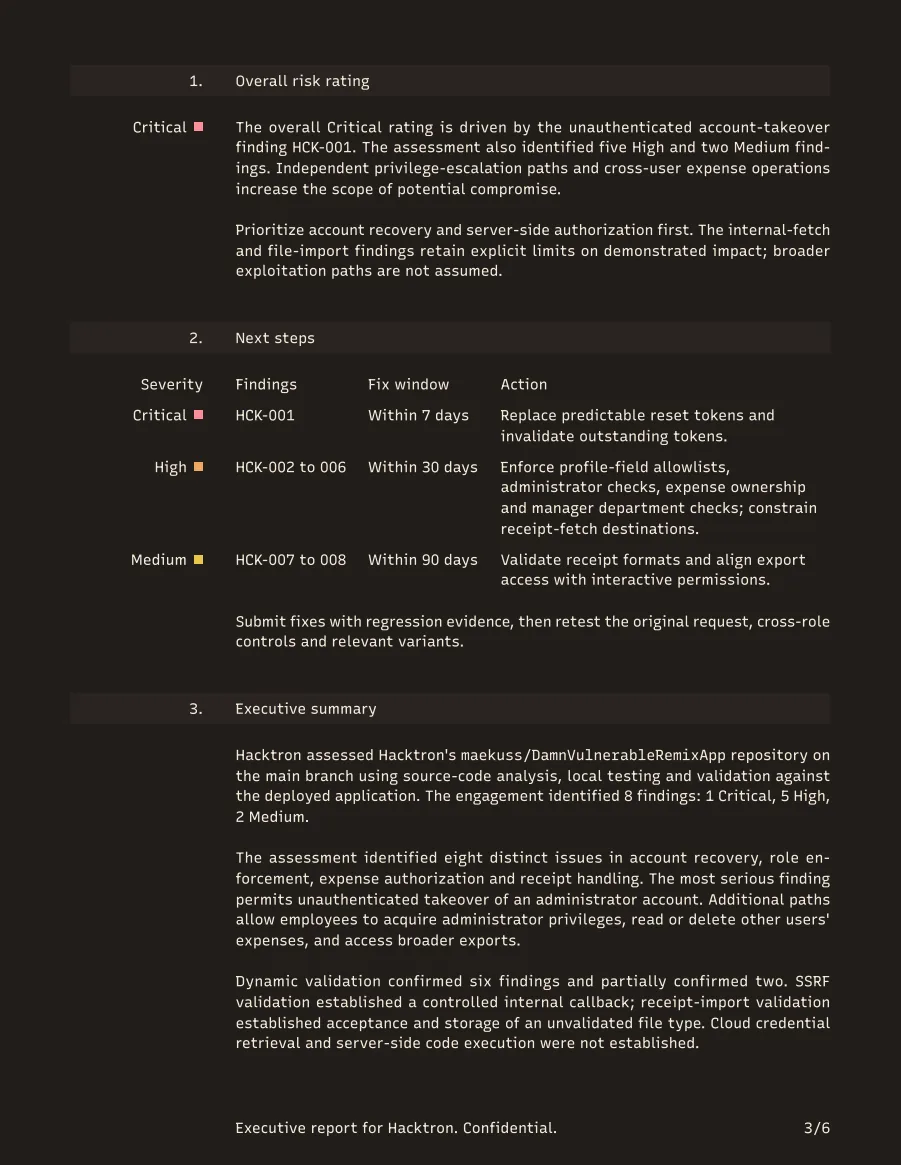
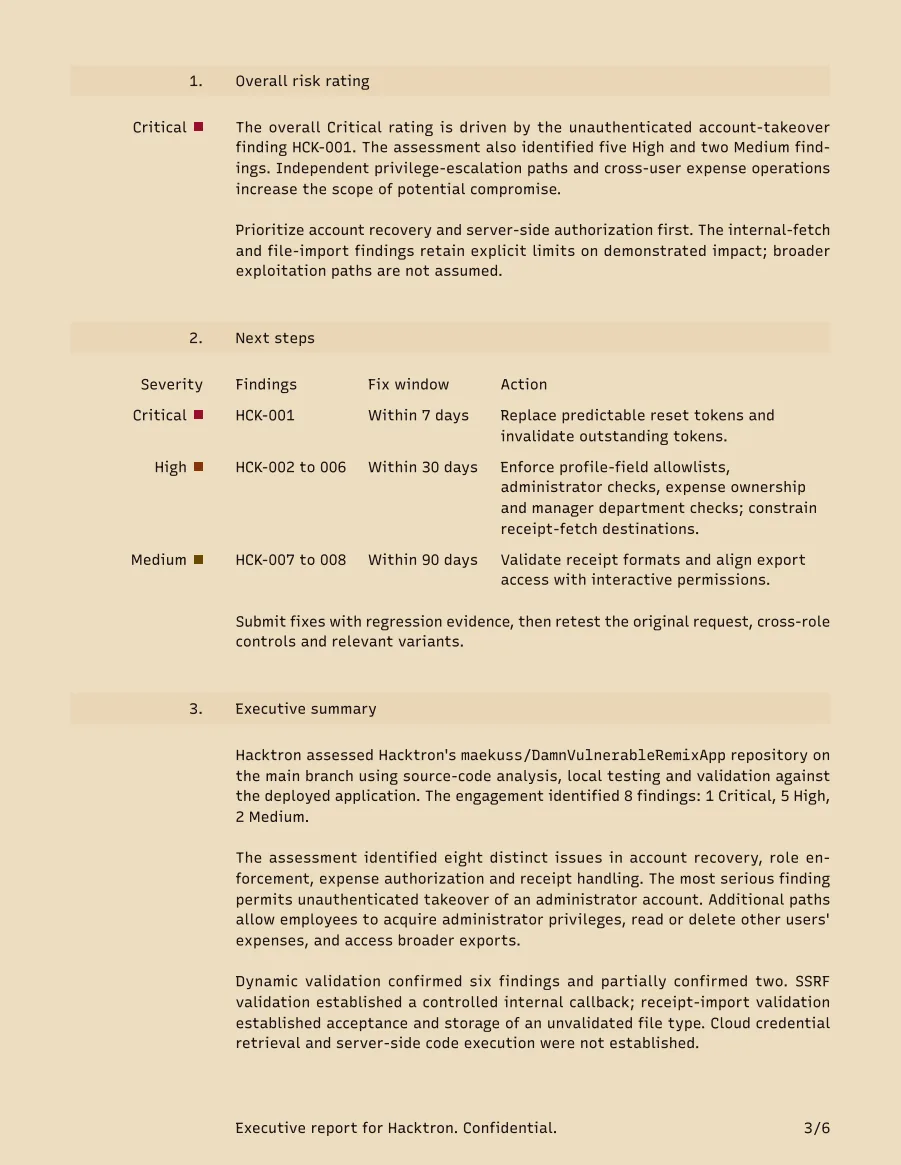
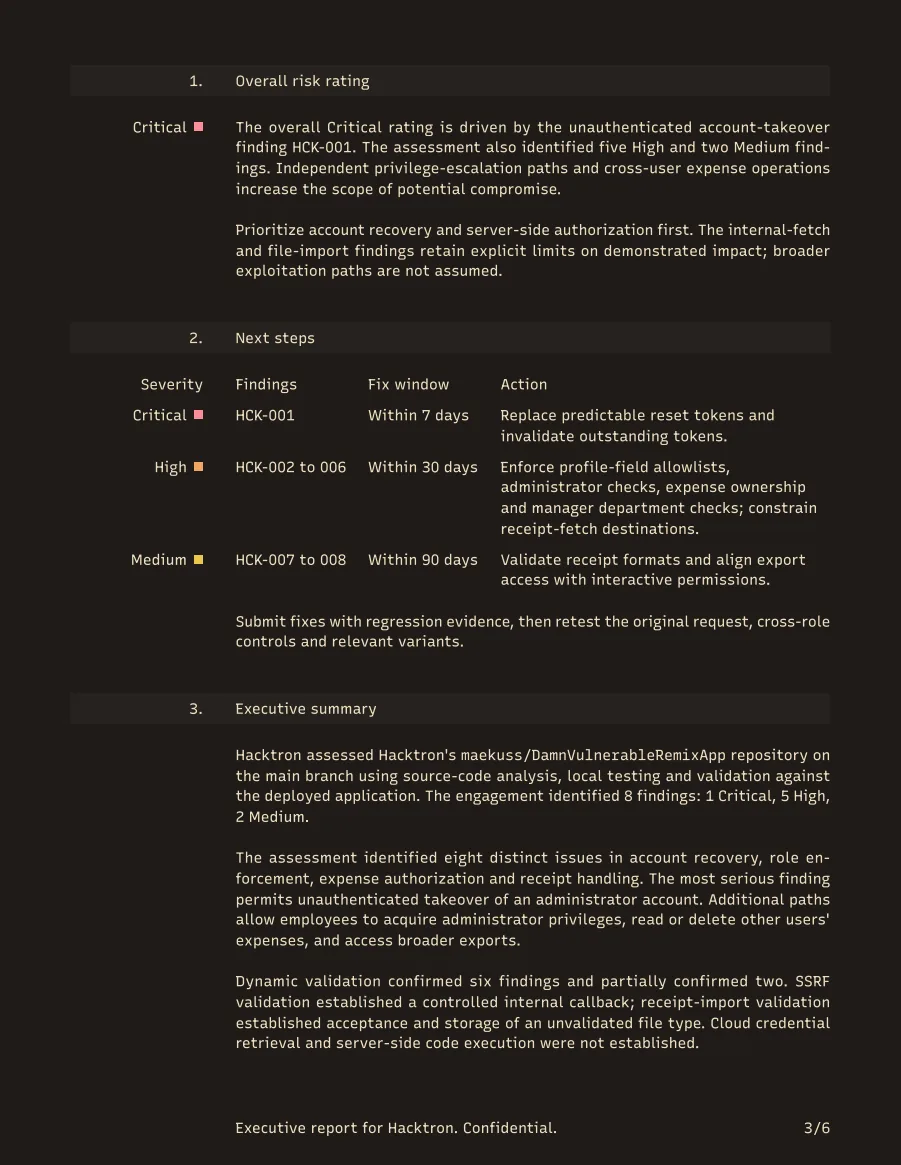
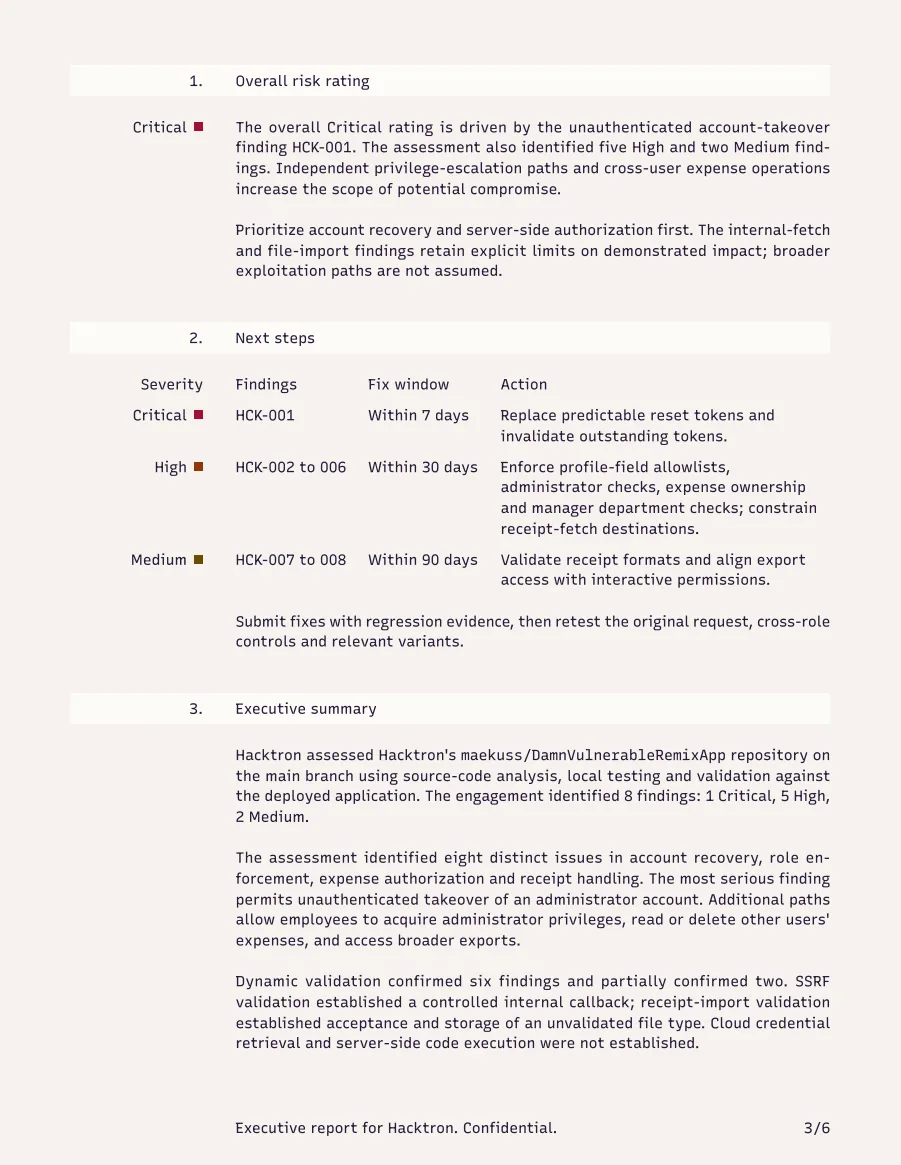
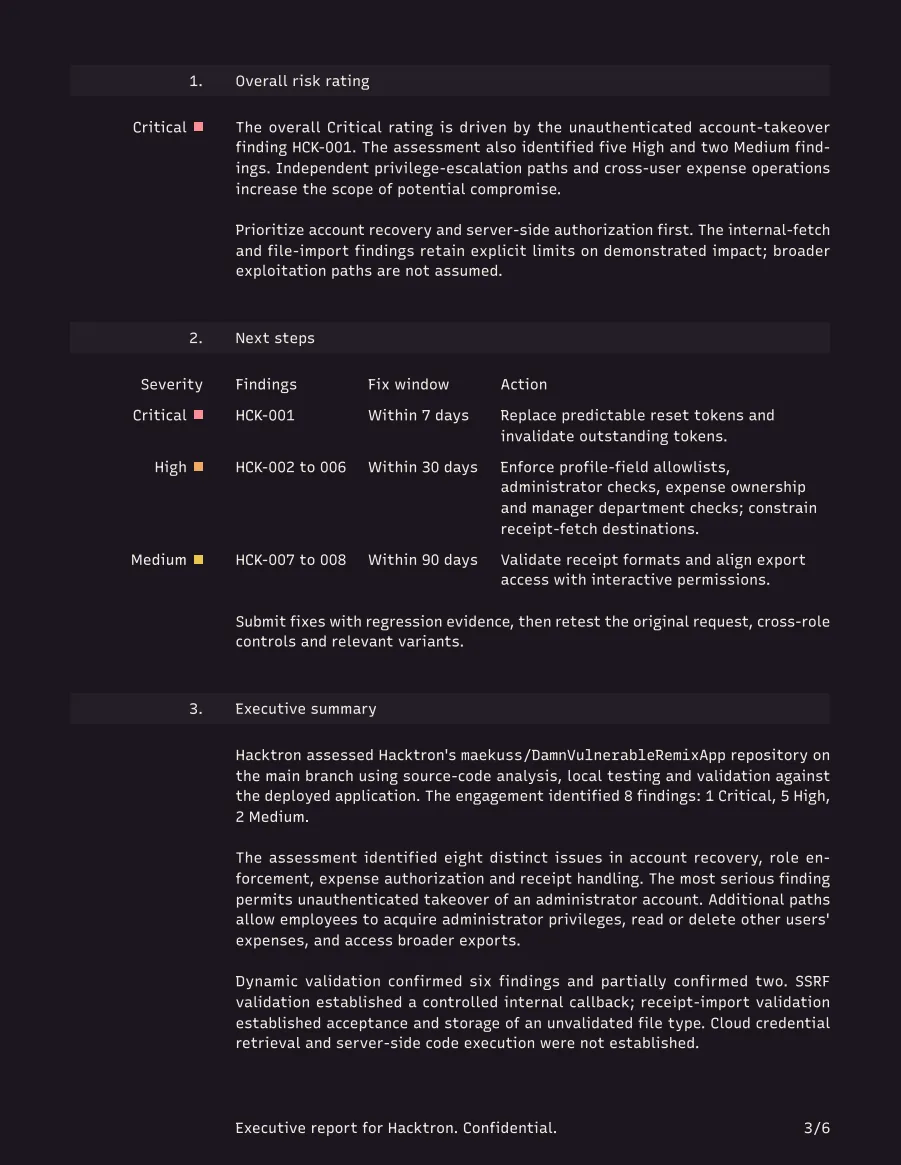
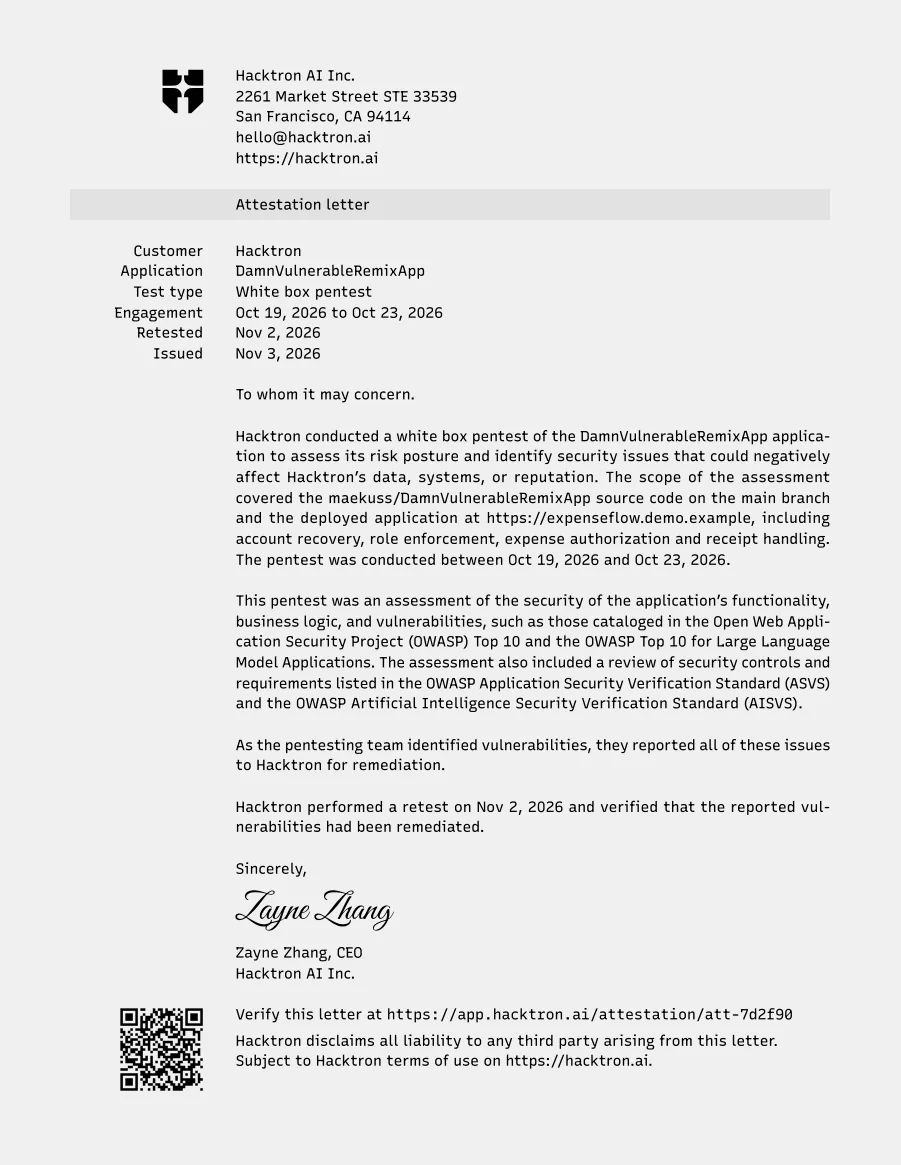
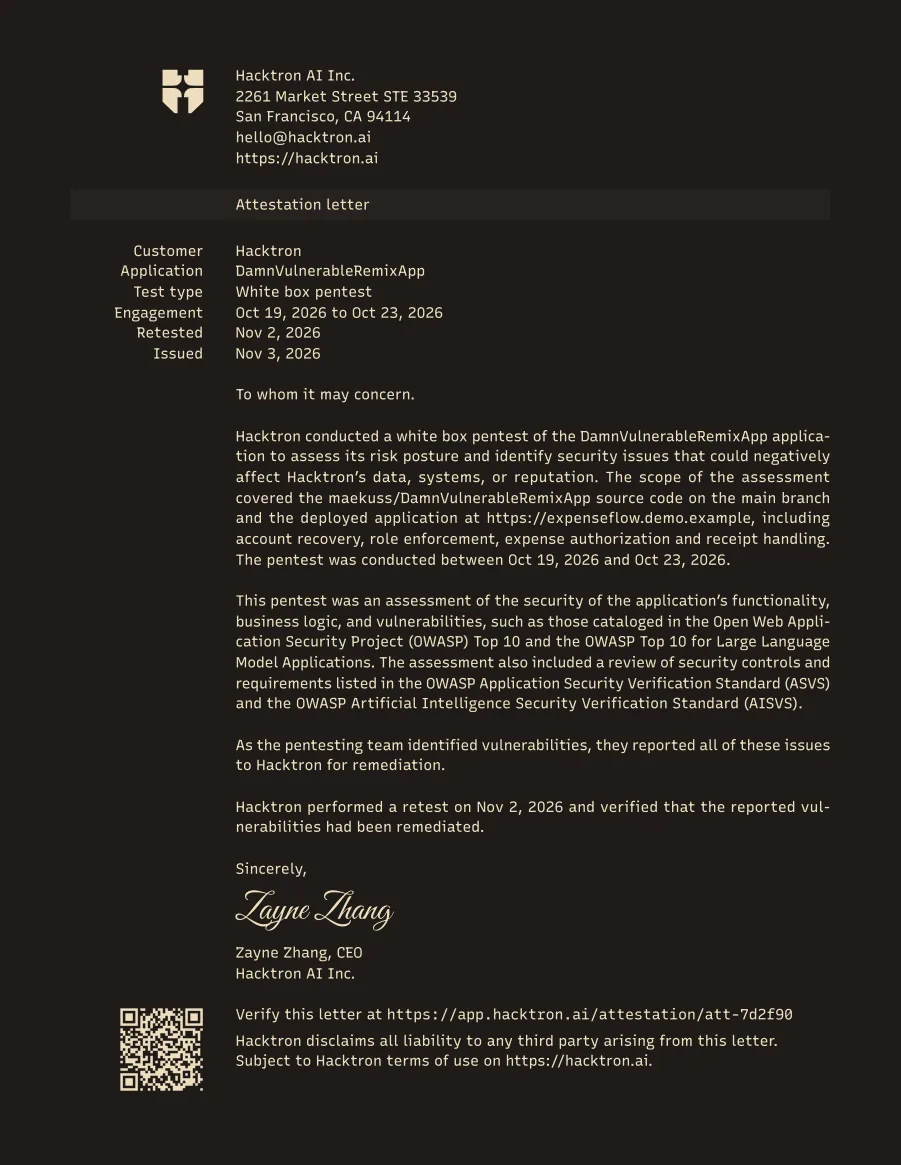
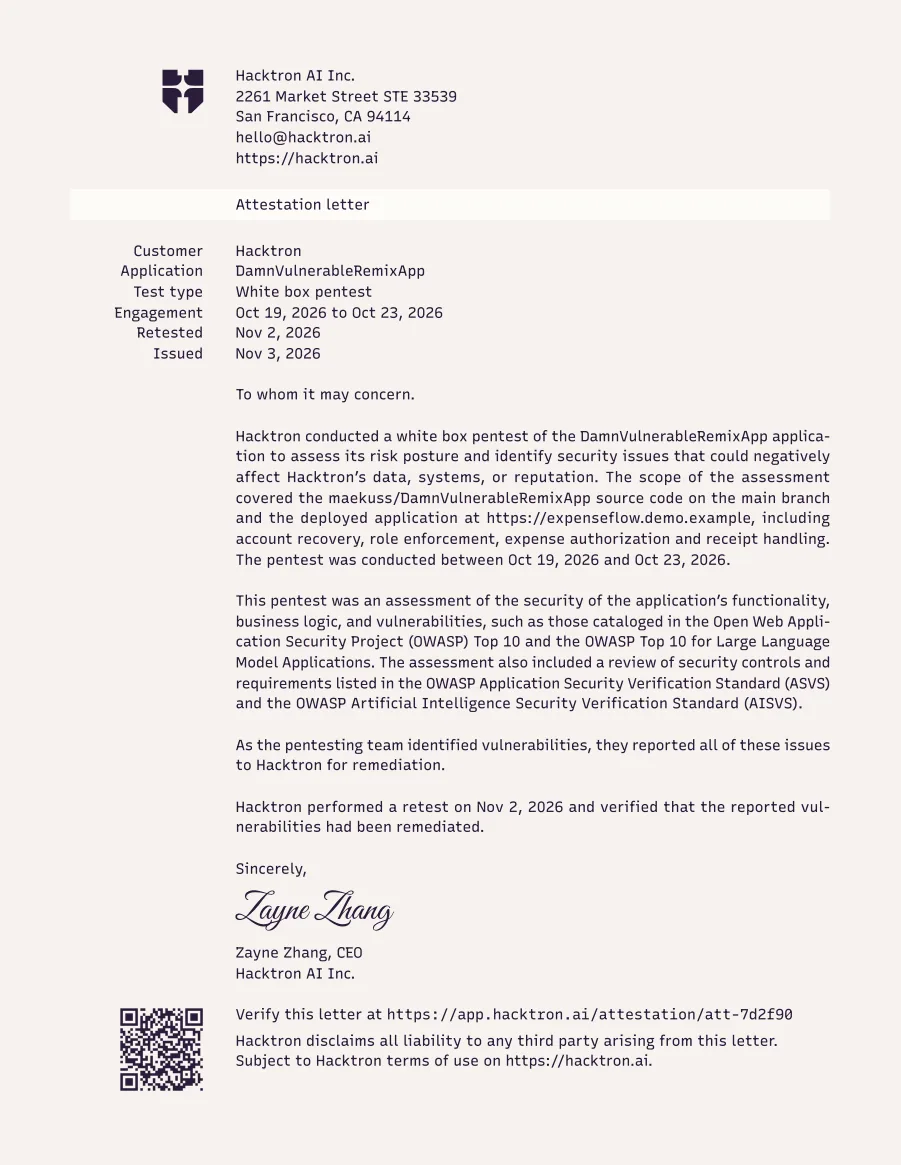
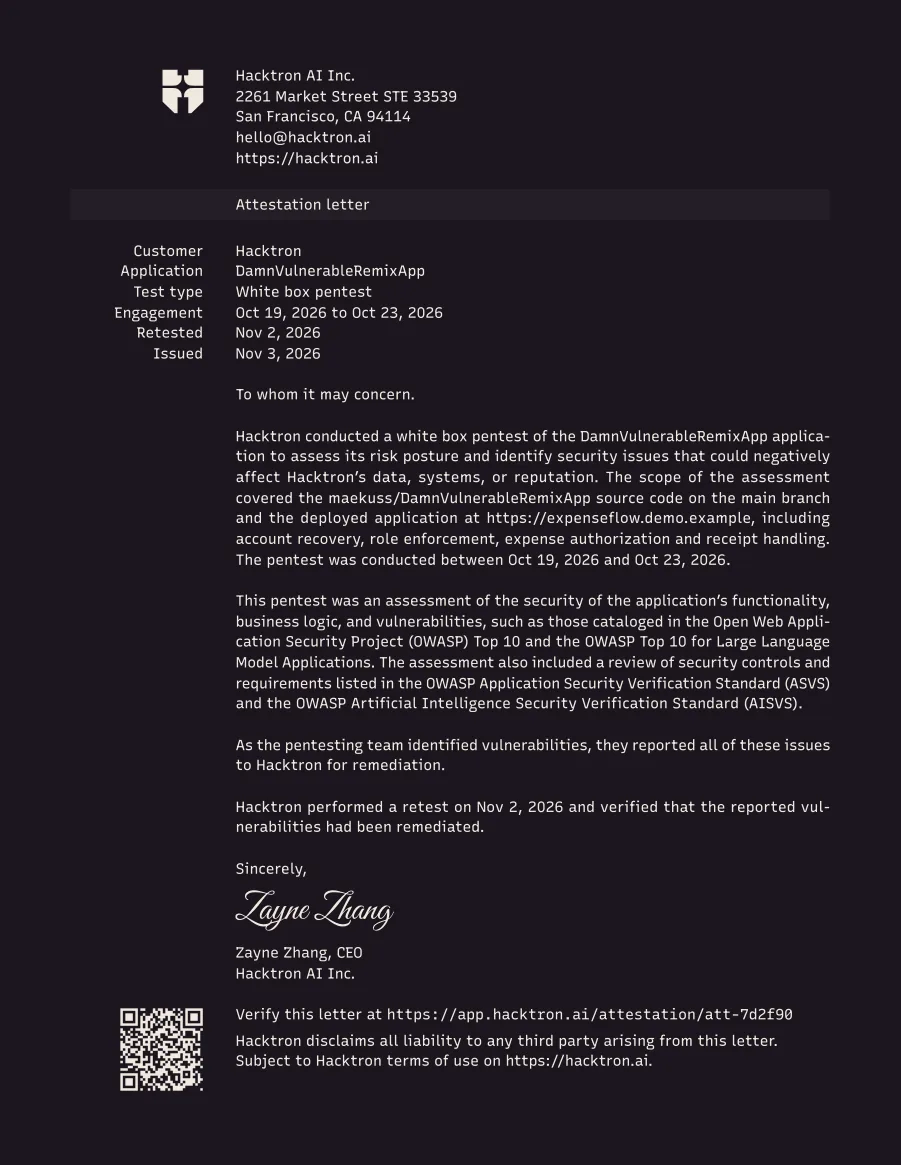
Each confirmed finding comes with where it is, how it was proven and how to fix it. The full report is for your engineers and the executive report for leadership and auditors. Both are reissued after the free retest, and an attestation letter confirms the pentest.

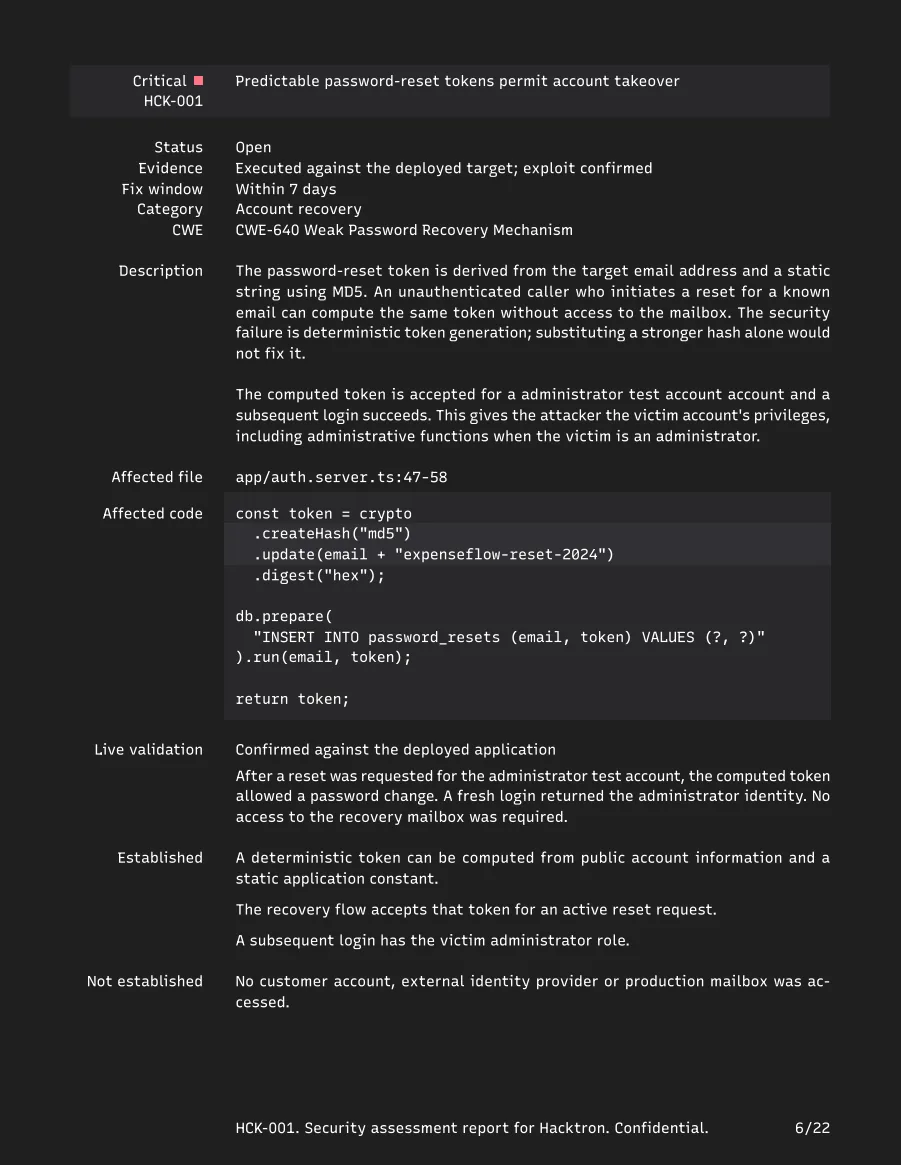
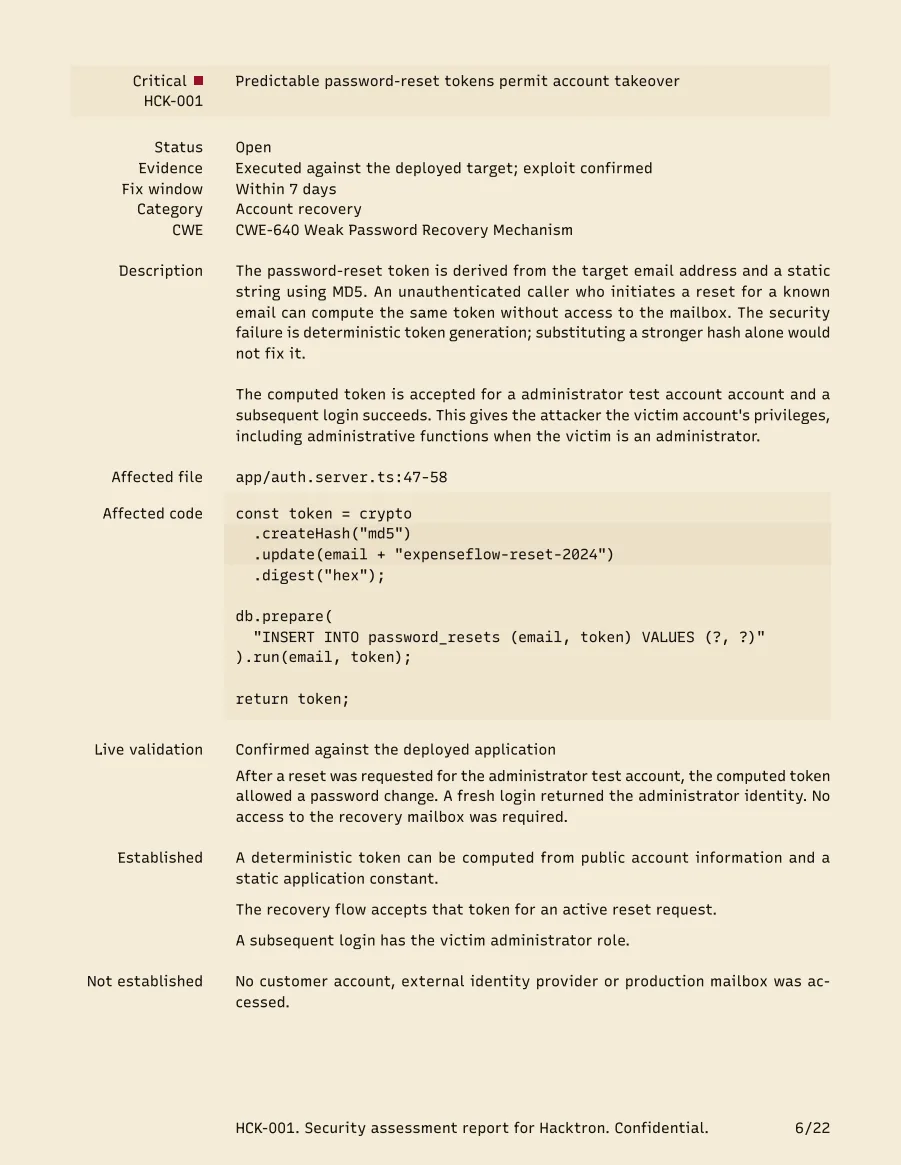
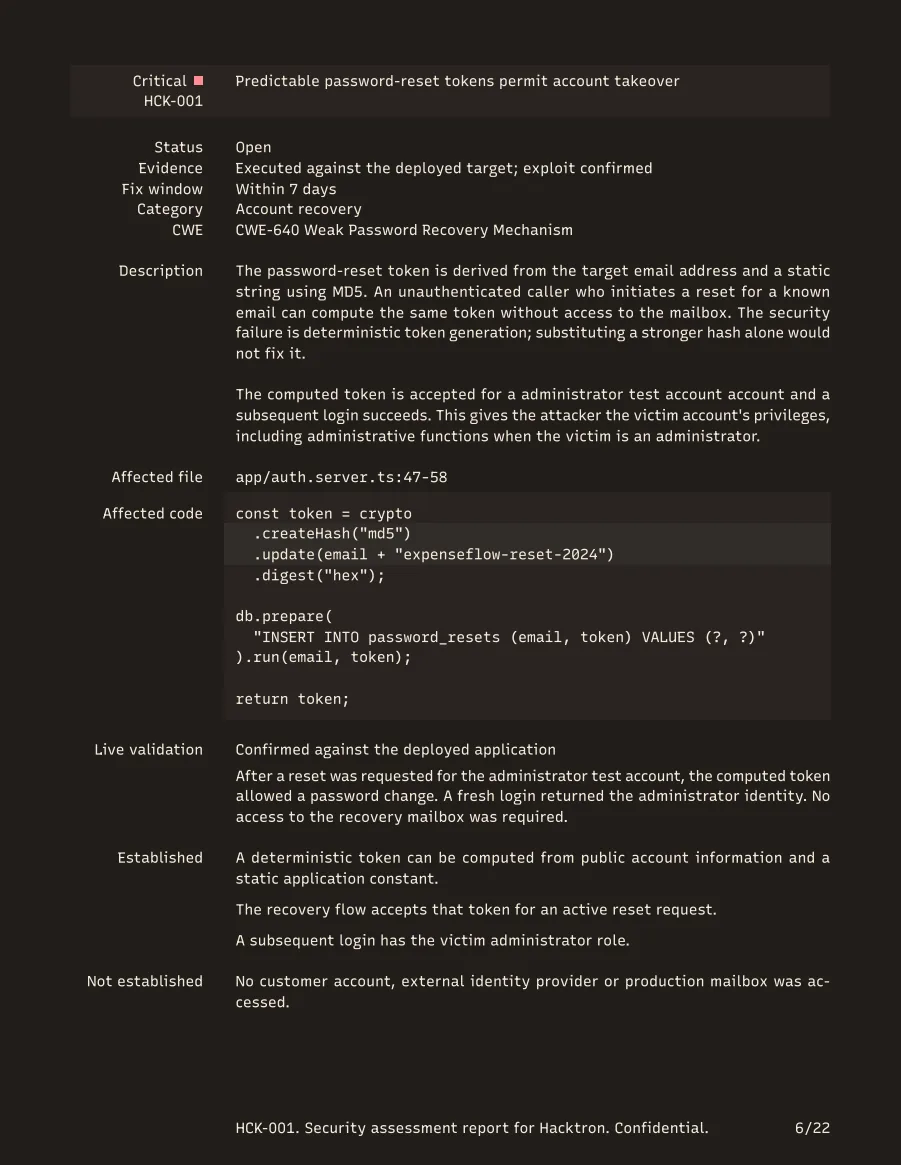
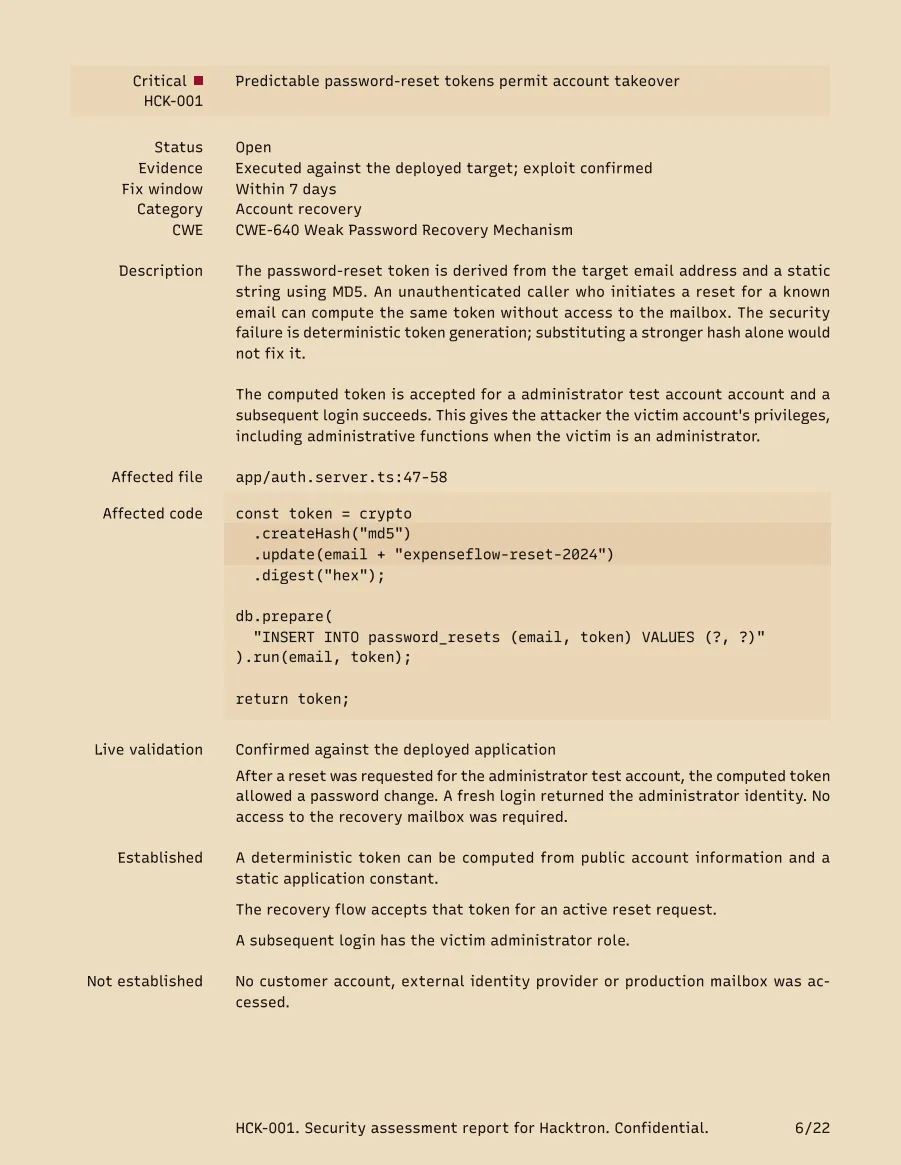
The sample full report is from a pentest of a demo expenses app.
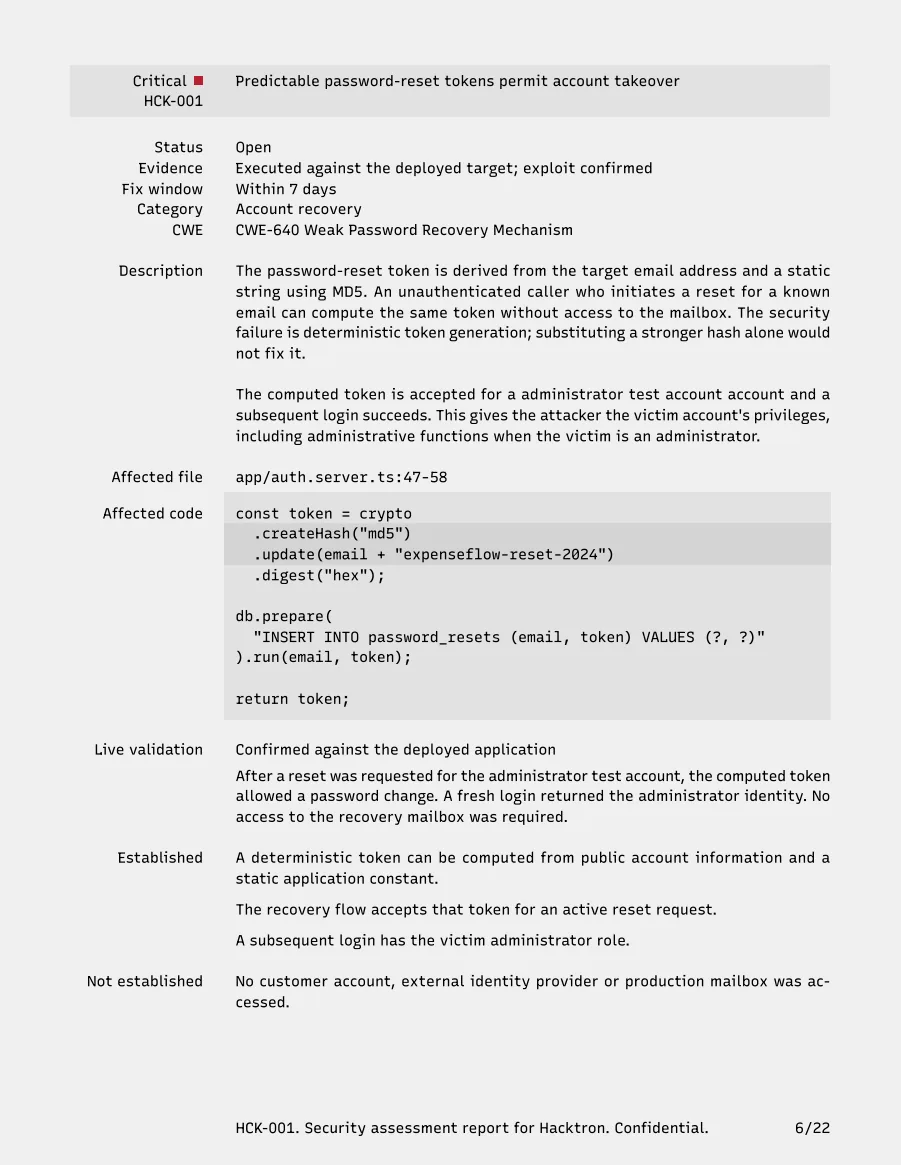
Page 6 of the sample full report: finding HCK-001, predictable password-reset tokens permit account takeoverPage 6 of the sample full report: finding HCK-001, predictable password-reset tokens permit account takeoverPage 6 of the sample full report: finding HCK-001, predictable password-reset tokens permit account takeoverPage 6 of the sample full report: finding HCK-001, predictable password-reset tokens permit account takeoverPage 6 of the sample full report: finding HCK-001, predictable password-reset tokens permit account takeoverPage 6 of the sample full report: finding HCK-001, predictable password-reset tokens permit account takeoverPage 6 of the sample full report: finding HCK-001, predictable password-reset tokens permit account takeoverPage 6 of the sample full report: finding HCK-001, predictable password-reset tokens permit account takeover
Full report
Page 3 of the sample executive report: overall risk rating, next steps and executive summaryPage 3 of the sample executive report: overall risk rating, next steps and executive summaryPage 3 of the sample executive report: overall risk rating, next steps and executive summaryPage 3 of the sample executive report: overall risk rating, next steps and executive summaryPage 3 of the sample executive report: overall risk rating, next steps and executive summaryPage 3 of the sample executive report: overall risk rating, next steps and executive summaryPage 3 of the sample executive report: overall risk rating, next steps and executive summaryPage 3 of the sample executive report: overall risk rating, next steps and executive summary
Executive report
Sample attestation letter confirming a retested pentestSample attestation letter confirming a retested pentestSample attestation letter confirming a retested pentestSample attestation letter confirming a retested pentestSample attestation letter confirming a retested pentestSample attestation letter confirming a retested pentestSample attestation letter confirming a retested pentestSample attestation letter confirming a retested pentest
Attestation letter

Price

The price follows the size of the code.

Questions

Is it a black-box test?

No. Whitebox reads the source, so it follows implementation details, data flows and business logic. For sensitive code, upload an archive, or run it inside your own network on the Enterprise plan.

Is dynamic testing safe?

Point it at a staging deployment with test accounts. Before the pentest starts, Hacktron follows your sign-in steps while you watch, and every action is logged.

Can we start it from our own tools?

Yes. Start a pentest from Slack, over MCP or through the API. An organisation admin approves the start.

Contact

Book a demo or start a pentest.

Menu
[M]
Next in menu
[J]
Previous in menu
[K]
Find
[F]
Sign in
[S]
Copy page
[C]
Justification
[R]
Dark mode
[D]
Palette
[T]
High contrast
[H]
Shortcuts
[I]
Close
[esc]