Introducing Hacktron
TL;DR
Gumroad was the very first audit we conducted at Hacktron a few months ago. Our agents found 12 issues, including a critical SQL injection.
We ran our swarm of specialized agents using Gemini 2.5 Pro. Some were purely LLM-based, some AST-based, and others purpose-built for niche vulnerability classes. Each source code review agent focused on a different weakness.
We’re proud to publicly release the Gumroad pentest report. We think it shows AI-powered penetration testing delivering results equivalent to a human pentest team.
Intro
At Hacktron, we’re building collaborative AI agents that act as autonomous security researchers1, capable of working across the entire software development lifecycle to find, triage, and fix vulnerabilities automatically.
These agents think like human hackers, collaborate across tasks, and take real action, because we distill our security research team’s expertise into them.
Further, we’re also building standardized security benchmarks to evaluate AI capabilities, and backing it all with zero-day research.
Manifesto
Our goal is to solve 90%2 of current software security problems.
As security researchers, we live for zero-days3 and novel exploits. But the vast majority of real findings are not intellectually challenging research problems that take years to materialize. They are repetitions of the same mistakes in different places. These are the vulnerabilities that constitute more than 90% of the software security problems we face today, showing up across the OWASP Top 10 and the HackerOne, Bugcrowd, Synack, and Cobalt yearly reports. Pentests and audits only find variants of already existing vulnerabilities. We don’t want to patch one hole only for another one to show up months later. The only way to do this is to change how penetration testing works, so that it runs continuously instead of as a one-off audit.
Just as AI has enabled an entire generation of non-technical users to build software, we see a real opportunity to bring the expertise of security researchers to ambitious teams who don’t have the time or expertise to think deeply about security. AI lets us do this at a scale and frequency that traditional security audits can’t match.
We are building a full-stack security engineer: an agent that finds, triages, and patches vulnerabilities autonomously.
These principles guide everything we build.
- We find and confirm vulnerabilities that are actually exploitable (PoC || GTFO), working across the entire software development lifecycle. Most security scanners are just noise.
- Our long-term goal is to secure the open-source software the internet depends on, such as Chromium, Linux, and Apache.
- We believe capable AI agents pose both an opportunity and a threat, so we commit to open, continuous evaluation of AI capabilities through real-world benchmarks that builders and policymakers can use. We’ve laid out our approach in detail at Hackbench.ai.
The Gumroad pentest
Saying “PoC || GTFO” then dropping a vague launch post with no real outcomes would’ve been just more noise. So instead, we’re presenting an AI-powered pentest of a real product, with real findings. We pointed Hacktron at Gumroad, and it found 12 issues, one of them a critical SQL injection.
This was part of a broader wave of assessments we’ve been running against open source products, bug bounty targets, and enterprise software.
The Gumroad team triaged and fixed our reports quickly. We would like to thank Sahil and Ershad for their collaboration throughout the process. We are now collaborating with Antiwork to integrate Hacktron into their CI/CD pipeline for ongoing, autonomous security monitoring.
Read the Gumroad pentest report.
How Hacktron works
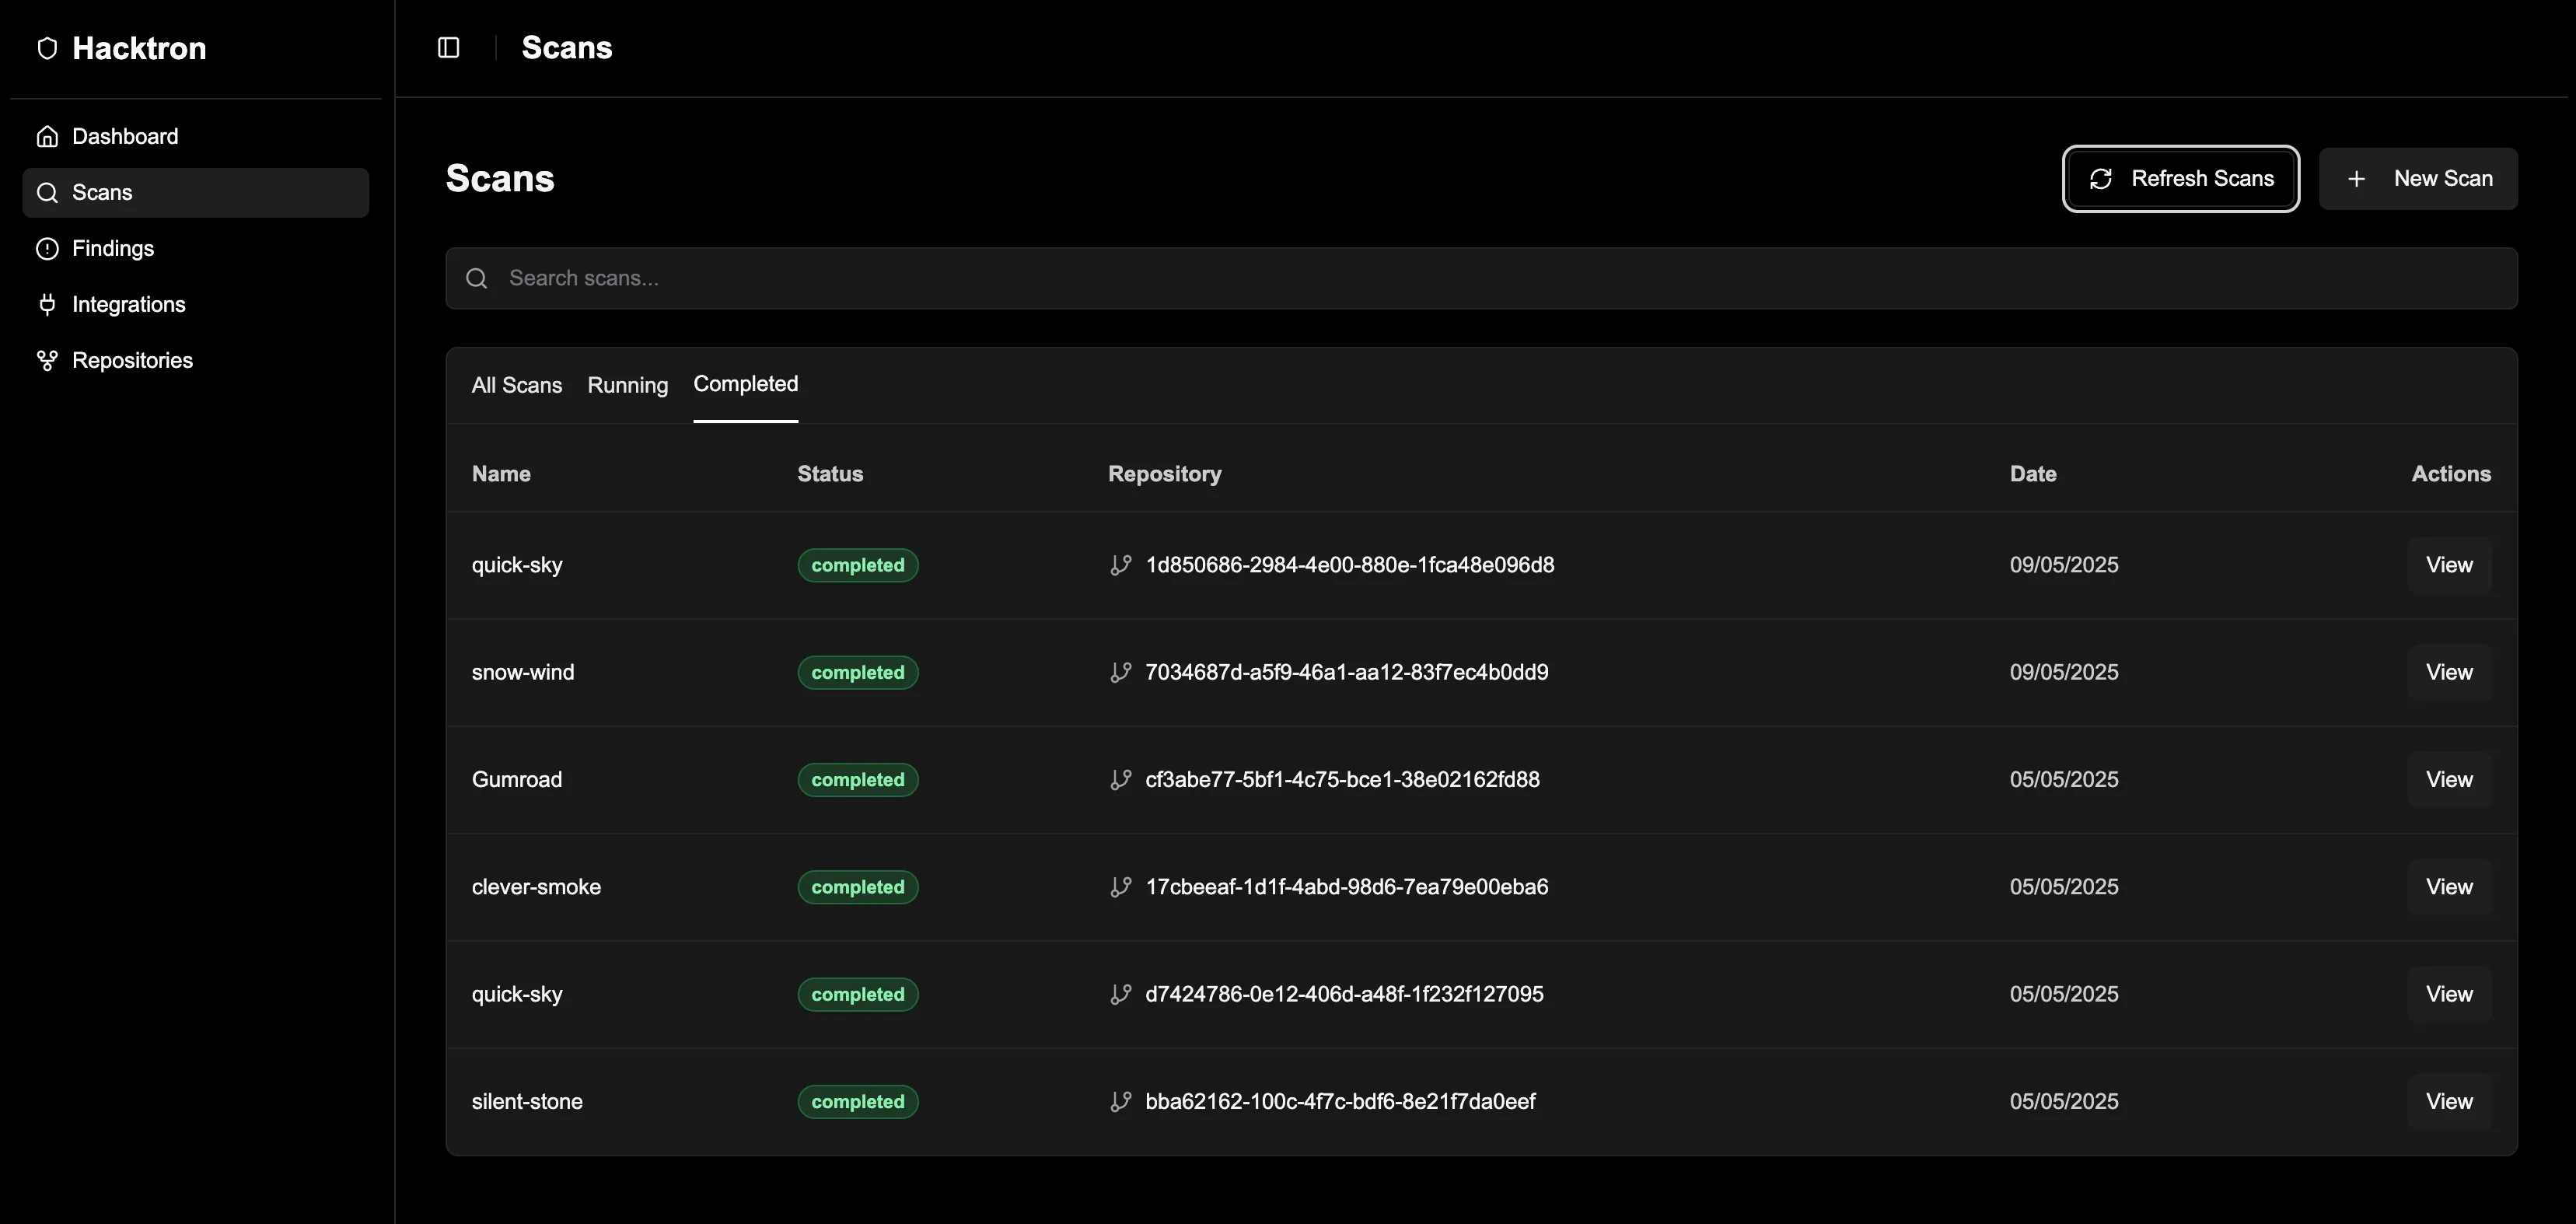
To initiate the engagement, we connected Hacktron to the Gumroad codebase and triggered a full-scope assessment:
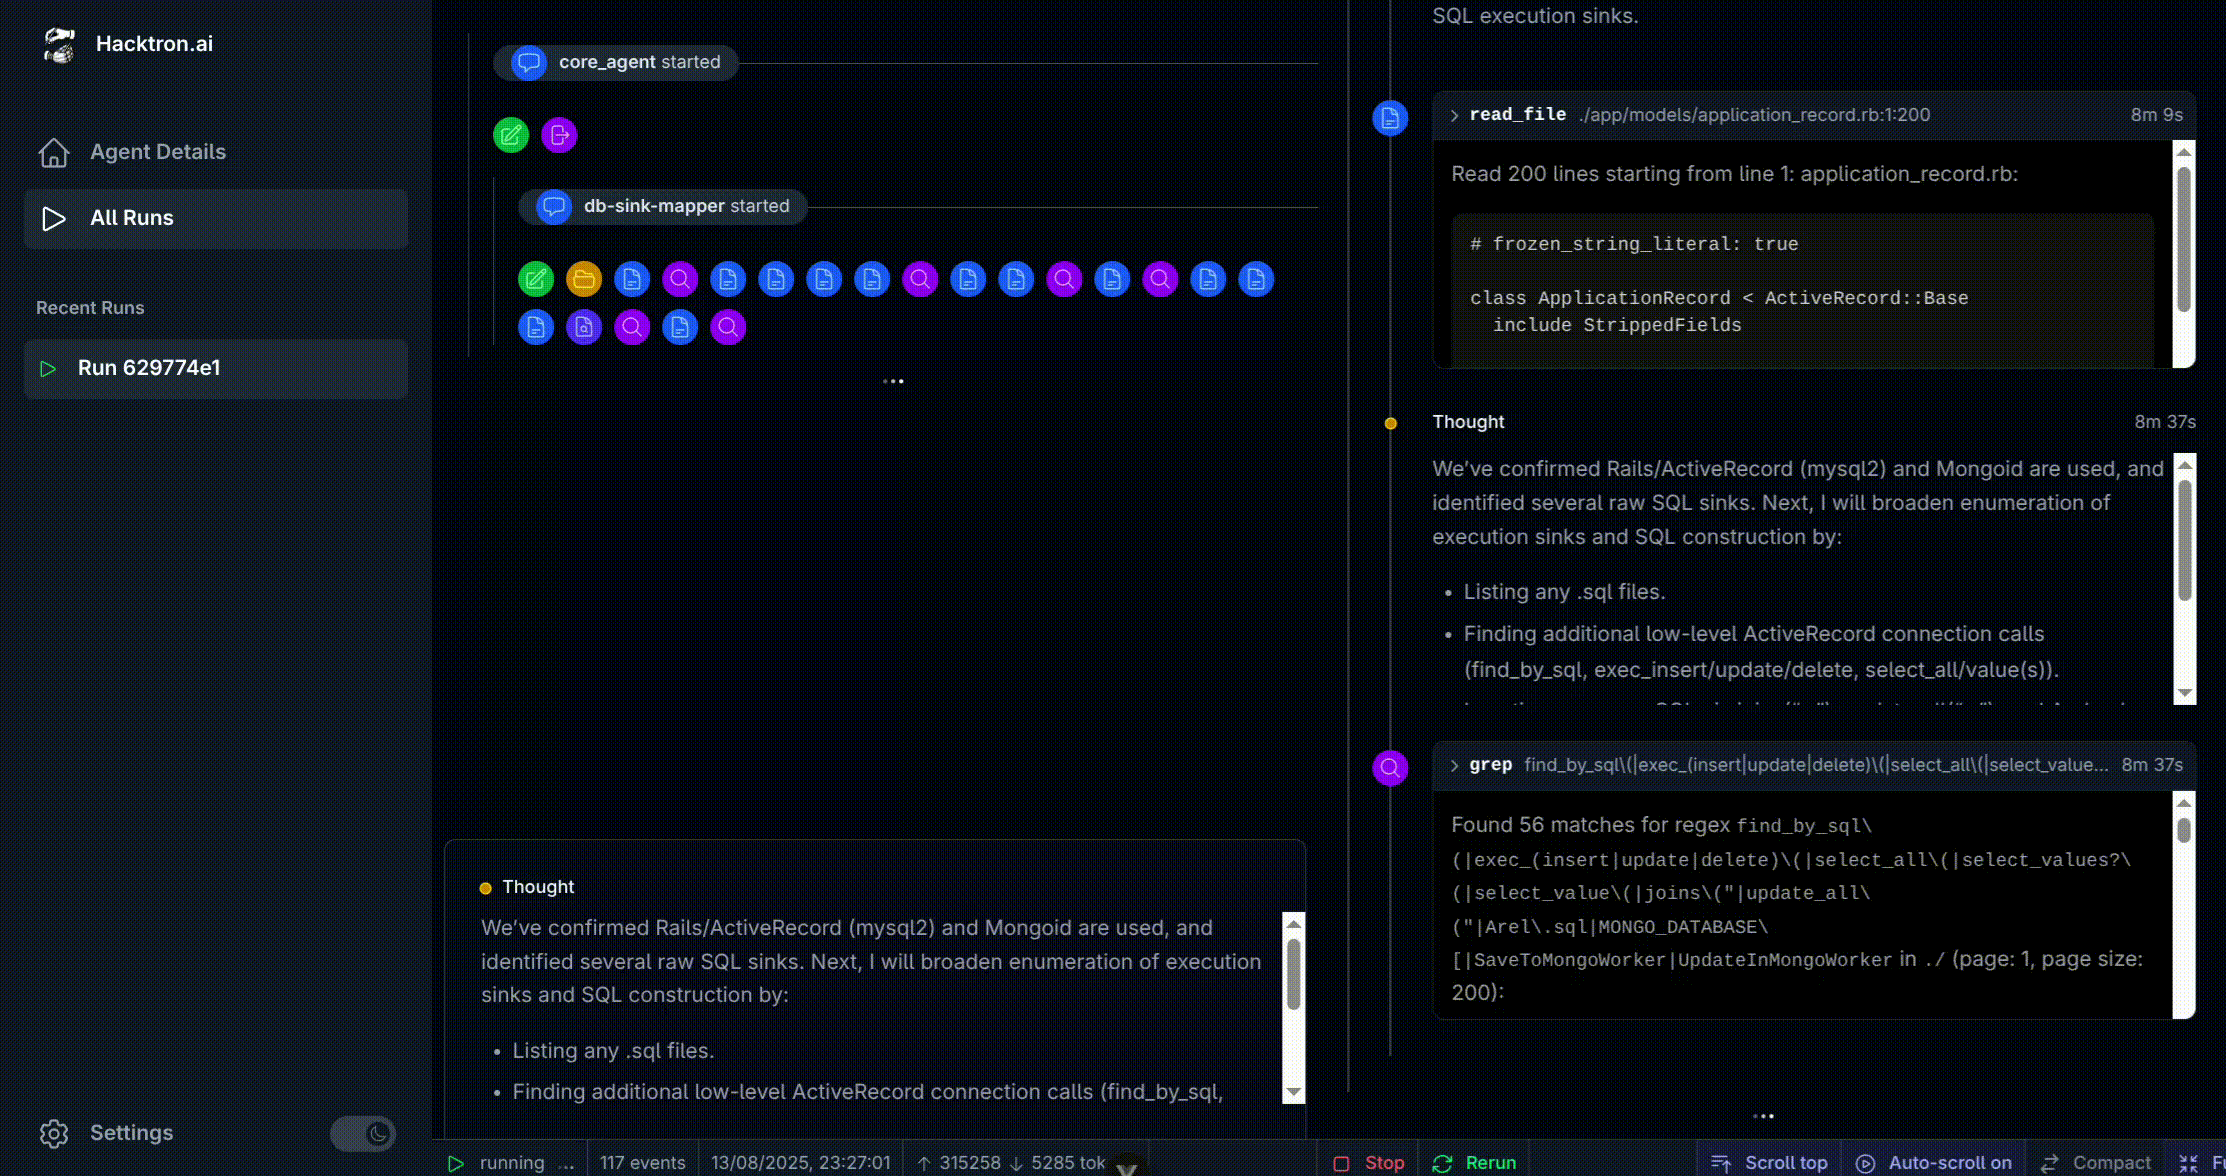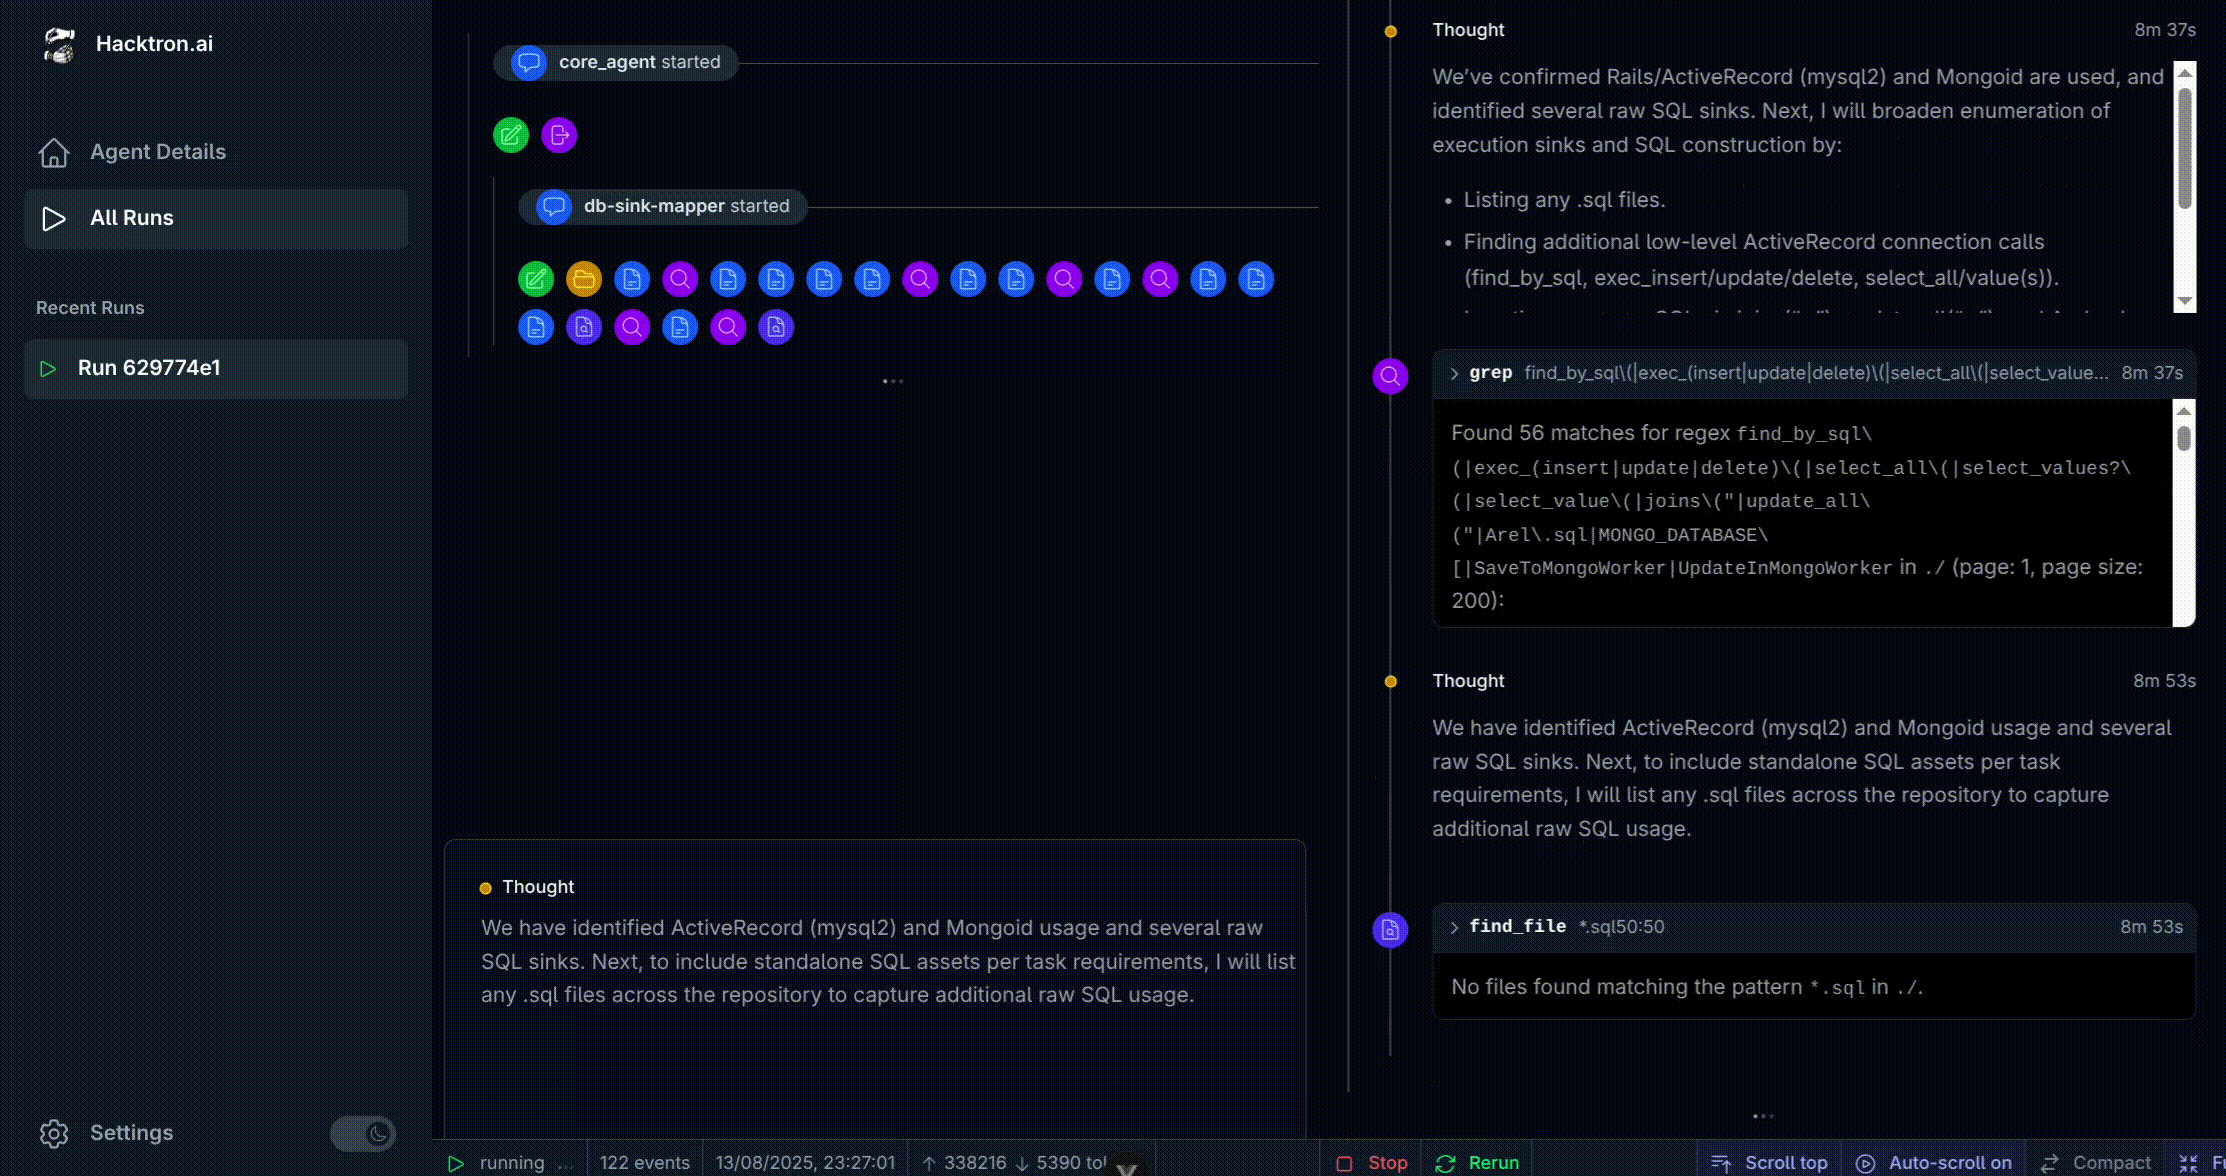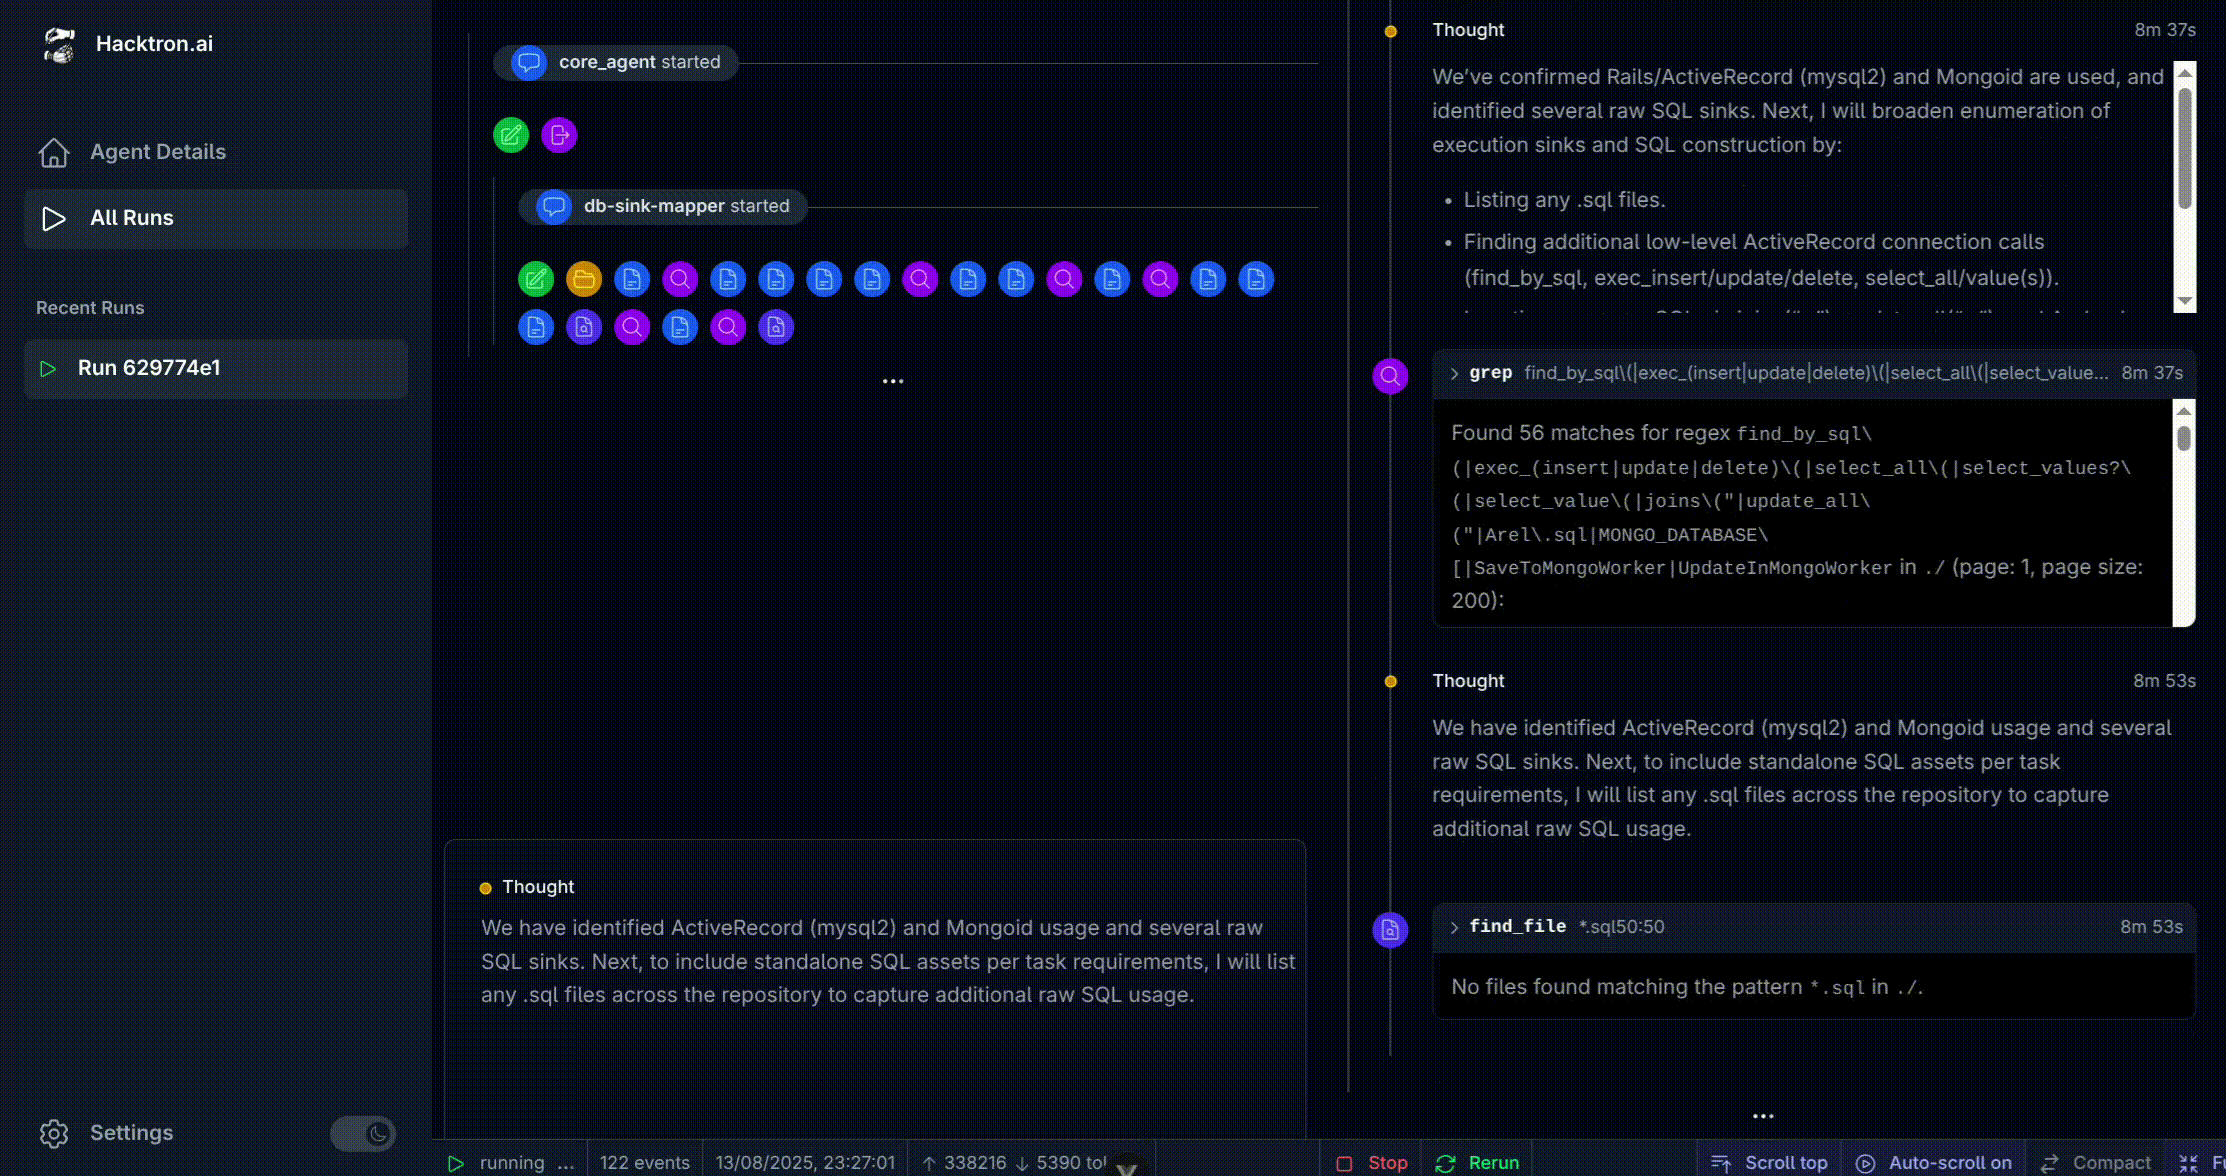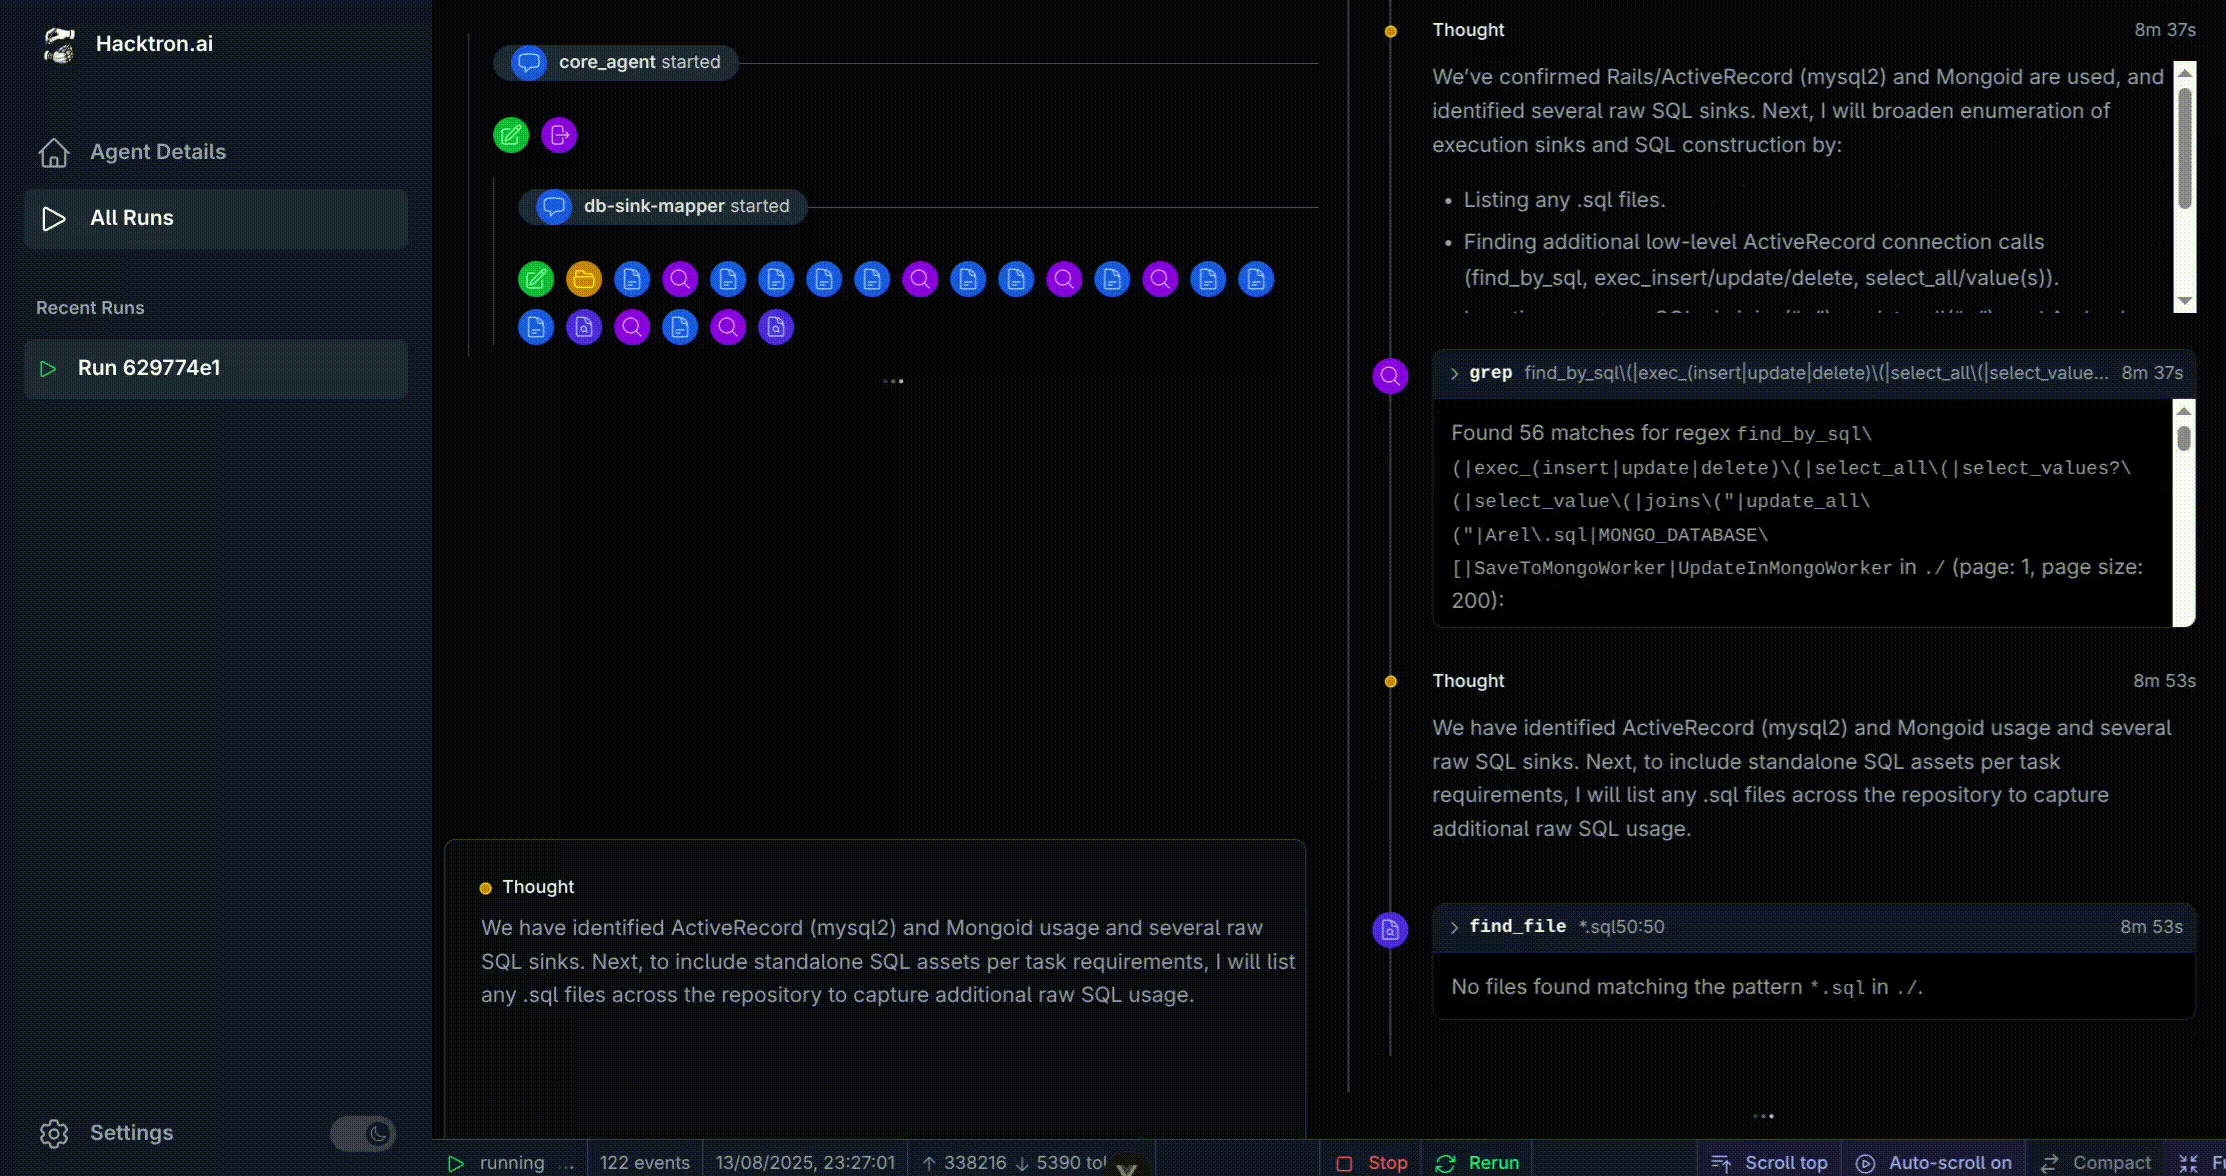
Hacktron began by cloning the repository and analyzing the application’s architecture. It performed a hybrid of static and dynamic analysis. It reasoned through frontend and backend flows, mapped attack surfaces, and identified critical data flows and control points:
For Gumroad, when vulnerabilities were identified, Hacktron triaged them autonomously, prioritizing issues based on exploitability, reachability, and security impact:
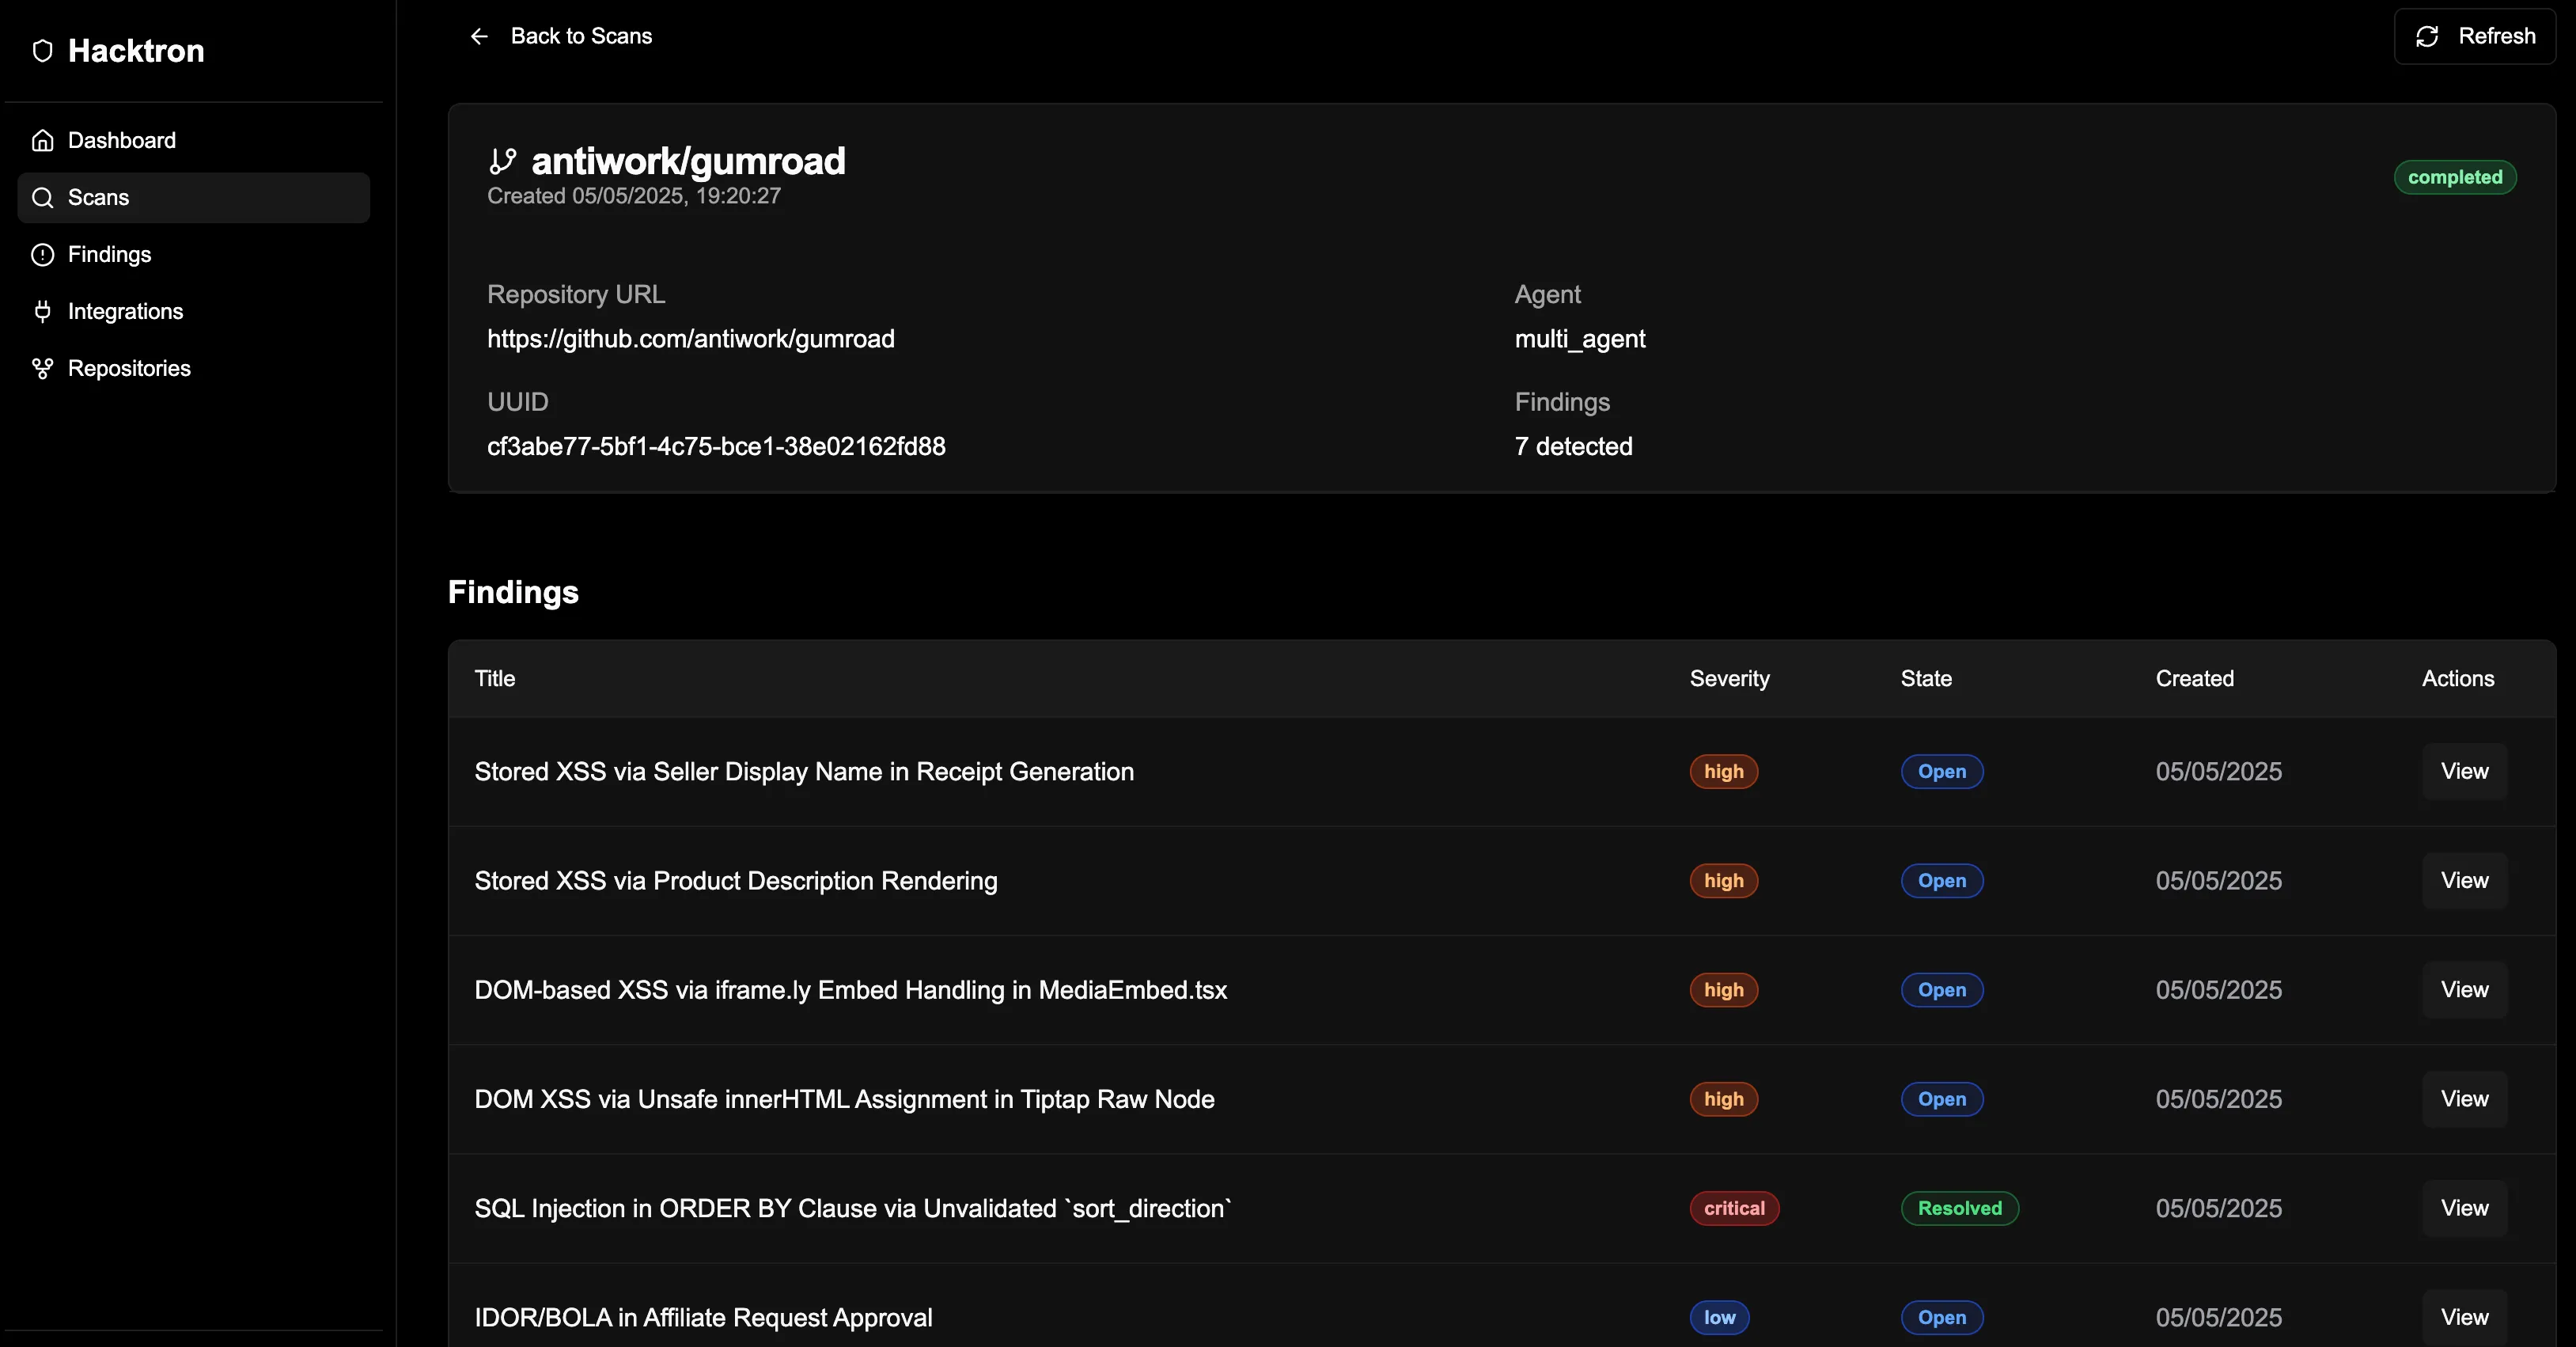
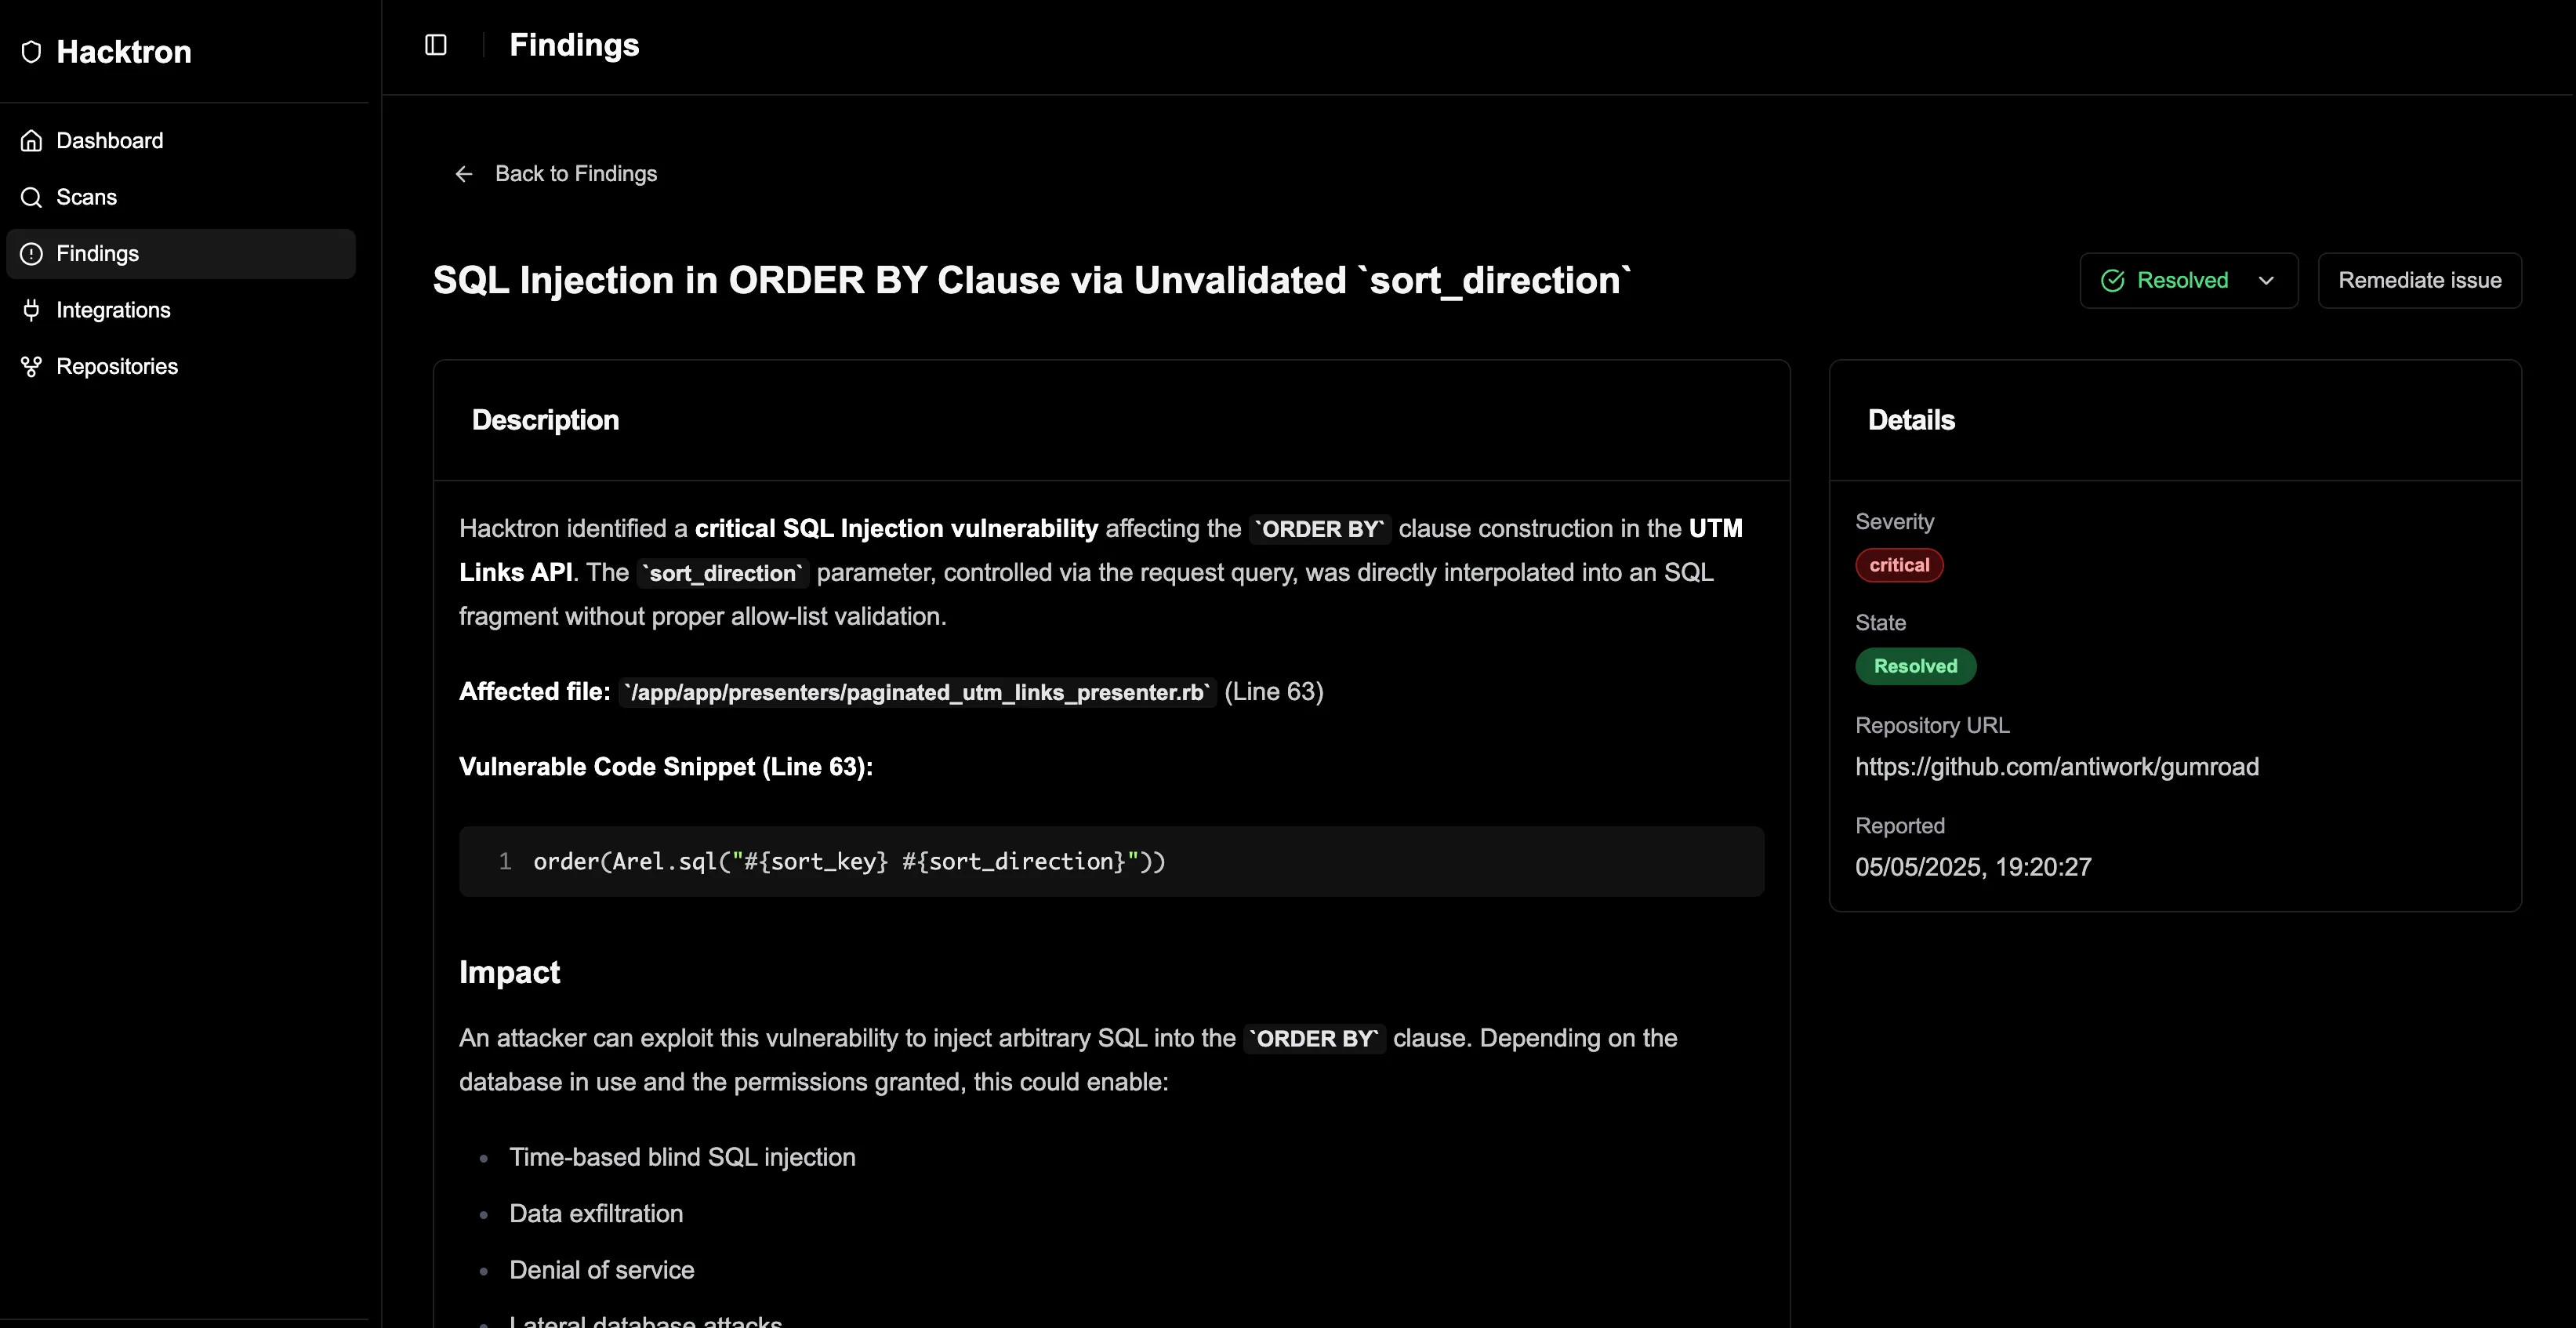
Each issue included full technical context: source traces, affected files, and remediation strategies. Raw tickets can be found on Hacktron’s hacktivity. The issues were surfaced through a dedicated dashboard for both our team and Gumroad’s engineers:
Our human researchers then reviewed and validated Hacktron’s findings, producing production-ready PoCs. The latest version of Hacktron generates PoCs and triages findings itself.
Reporting
The findings include one critical SQL injection and four high-severity XSS bugs, all exploitable. The SQL injection alone posed a serious risk, and Gumroad moved quickly to remediate it. A traditional pentest for the same scope would cost between $20,000 and $30,000, and we did it for roughly one-third of the price.
High
DOM XSS via Unsafe
innerHTMLAssignment in Tiptap Raw NodeHigh
DOM-based XSS via iframe.ly Embed Handling in
MediaEmbed.tsxHigh
Stored XSS via Product Description Rendering
High
Stored XSS via Seller Display Name in Receipt Generation
Critical
SQL Injection in
ORDER BYClause via Unvalidatedsort_directionLow
IDOR in Email Unsubscribe Functionality
Low
IDOR/BOLA in Affiliate Request Approval
Low
IDOR in Mobile Preorder Attributes API with Hardcoded Mobile Token
The report also lists four miscellaneous findings:
Info
Weak Host Validation in
isValidHostFunctionInfo
Stored XSS via Unsanitized Third-Party Analytics Snippets
Low
Unauthenticated Purchase Unsubscribe via IDOR in
PurchasesControllerLow
Potential XSS via Arbitrary HTML Upload to
files.gum
Patching
For confirmed issues, Hacktron generated suggested code-level patches and submitted pull requests, which were then merged by the Gumroad team:
      ).squish, query: "%#{query}%")    end
    scope = scope.order(Arel.sql("#{sort_key} #{sort_direction}"))    allowed_directions = ['asc', 'desc']    sort_direction = allowed_directions.include?(sort_direction.to_s.downcase) ? sort_direction : 'asc'    scope = scope.order(Arel.sql("#{sort_key} #{sort_direction}"))
    pagination, links = pagy(scope, page:, limit: PER_PAGE, overflow: :last_page)
...
  private    attr_reader :seller, :query, :page, :sort_key, :sort_directionendend\ No newline at end of file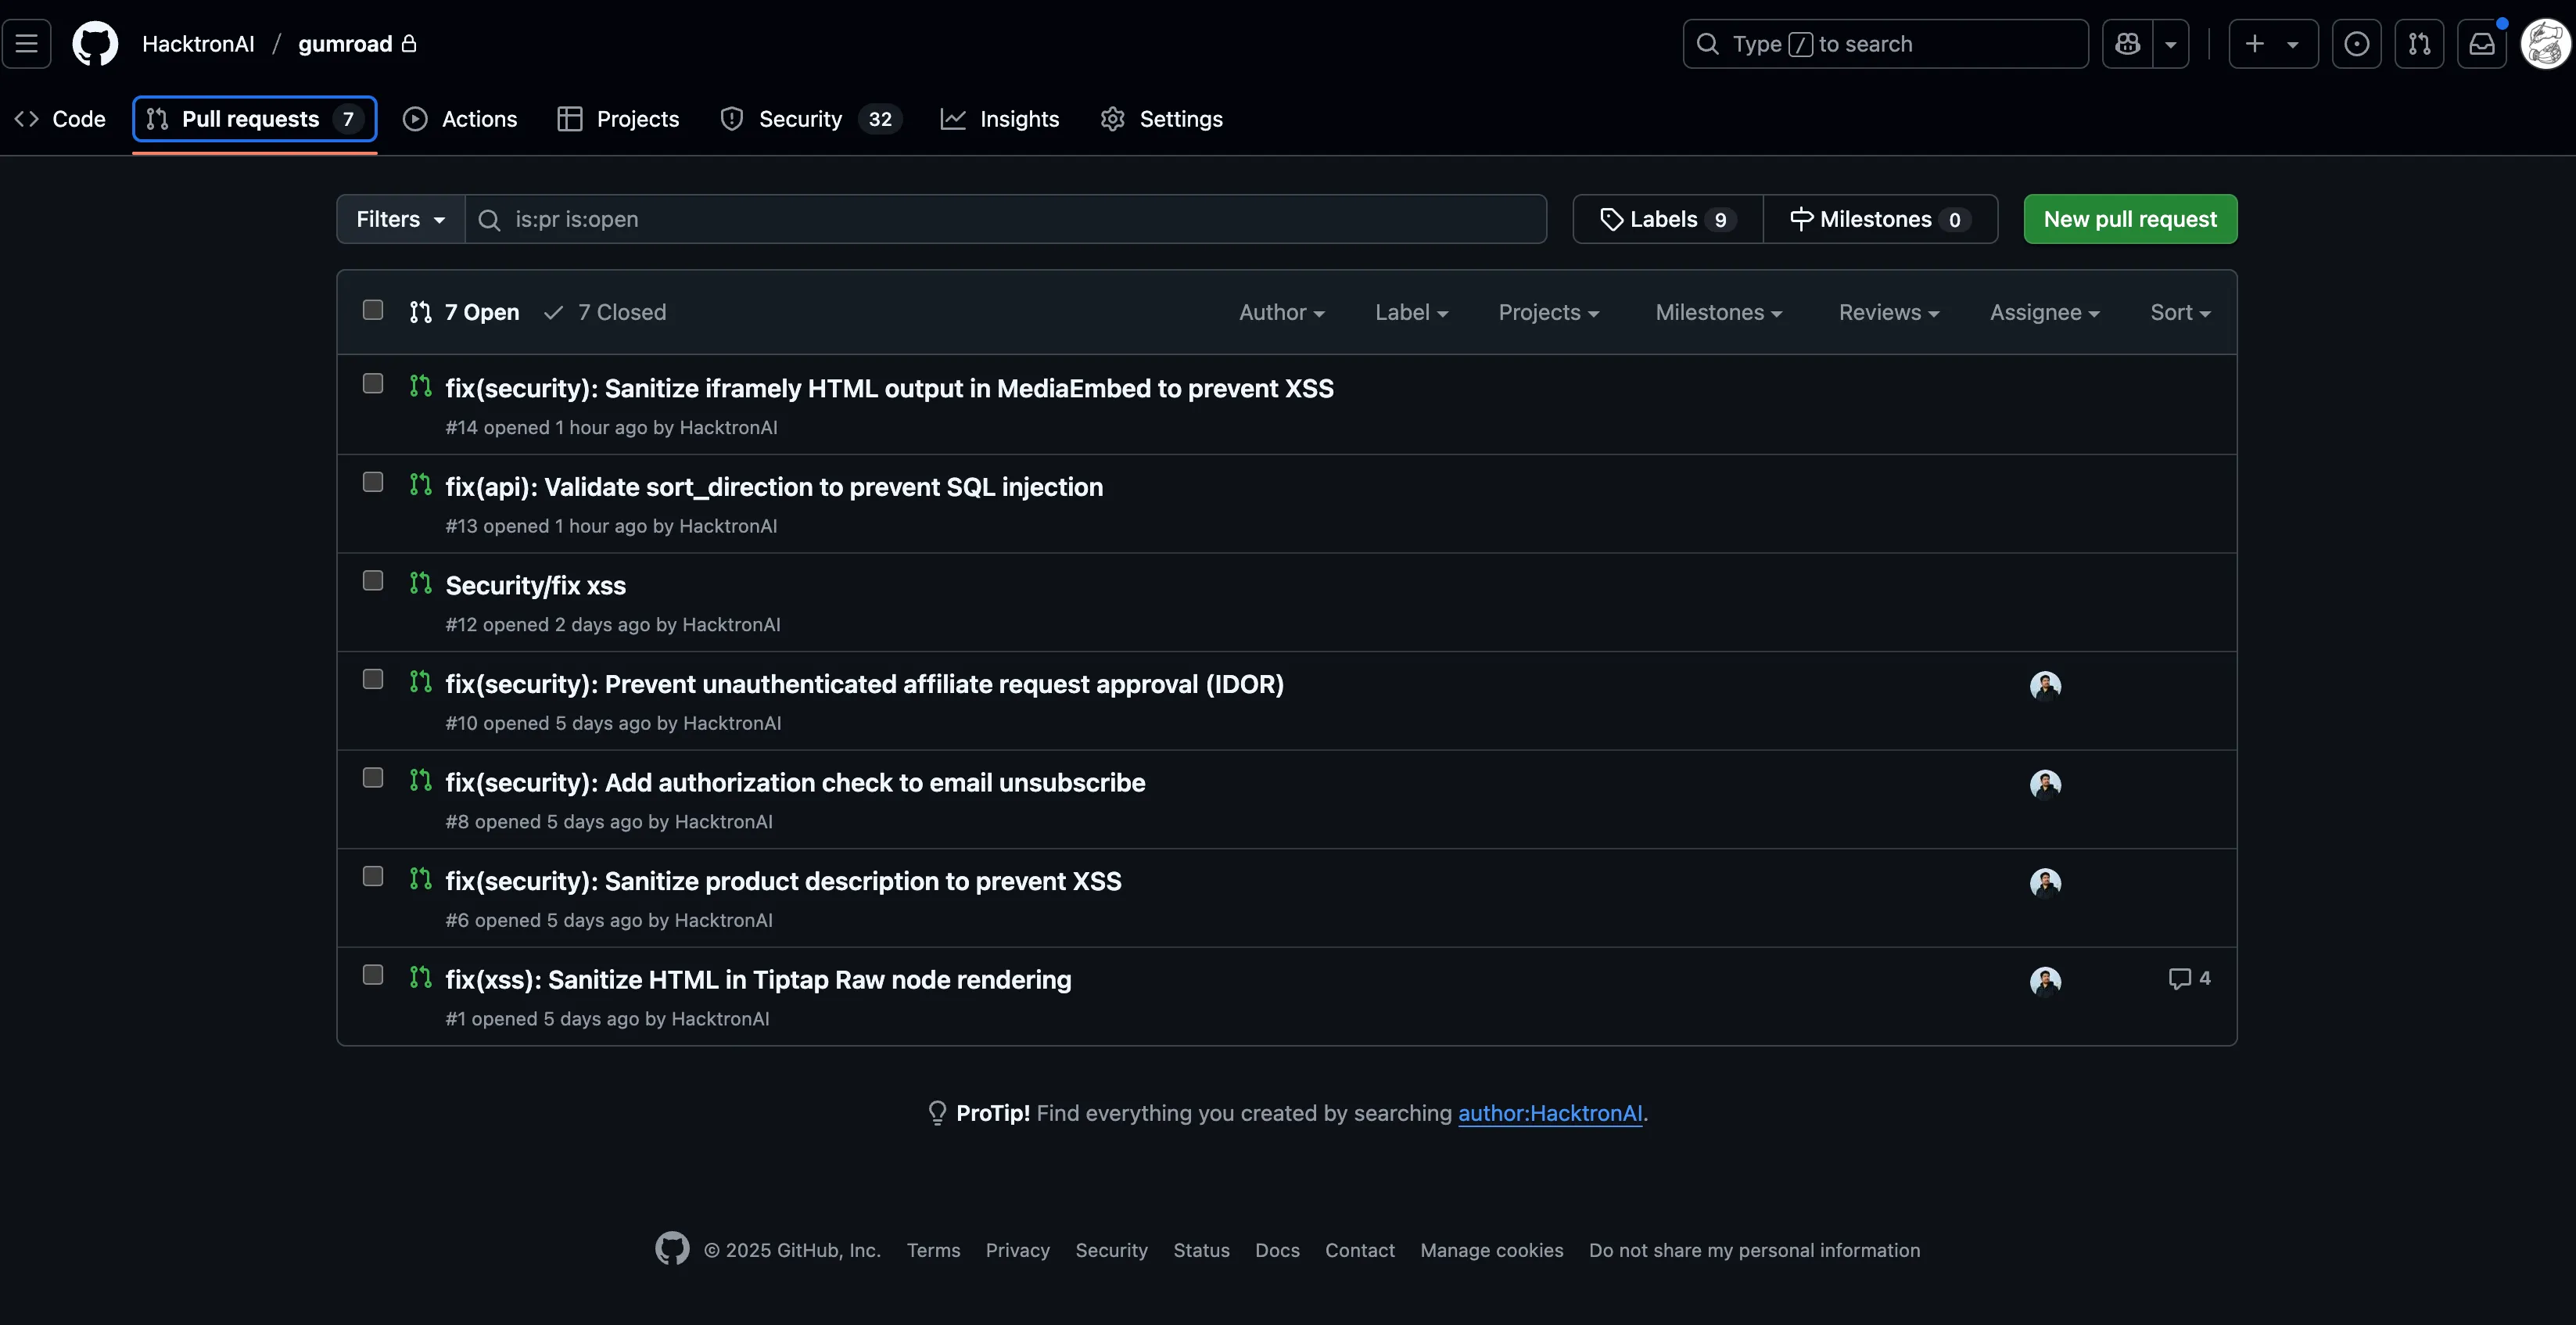
About us
Our security research team includes top-ranked CTF competitors, DEF CON-published researchers, creators, and bug bounty hunters. We’ve hacked browsers, operating systems, mobile apps, desktop software, and massive web platforms.
We’re now putting that expertise into Hacktron, AI agents that bring offensive security testing into every stage of the software lifecycle.
Meet our team.
Hacktron is currently in private beta. We’re running pilots with select partners to refine our AI agents and build out our platform.
Please contact us or email hello@hacktron.ai to discuss how we can help secure your product. You can also join our waitlist to be notified when we open up access more broadly.
Footnotes
-
Read more about our approach to building hacking agents in How Can We Make AI Hack Like a Human?. ↩
-
Pentesting today mostly revolves around finding variants of already known vulnerabilities. If we look at the top 10 reports from HackerOne, Bugcrowd, or Synack over the past decade, it’s the same issues repeating in different places. Specifically, Cobalt’s 2024 State of Pentesting report backs this up: on page 10, the numbers strongly support the estimate that around 90% of current web security issues are just repetitions. And even within the remaining 10%, about half are trickle-down issues from new variants uncovered first by security researchers. ↩
-
Our founding team has published security research on httpvoid.com, Electrovolt, s1r1us.ninja, analogue.computer, and liveoverflow. Our CVEs include CVE-
2023- , CVE-38693 2023- , CVE-32079 2023- , CVE-32078 2023- , CVE-32077 2020- , CVE-11053 2022- , CVE-25763 2022- , CVE-28129 2022- , CVE-1705 2022- , CVE-32213 2022- , CVE-32214 2022- , CVE-32215 2022- , CVE-24790 2022- , CVE-24801 2022- , CVE-24766 2022- , CVE-24761 2023- , CVE-3431 2023- , CVE-3432 2021- , CVE-41097 2022- , and CVE-29247 2021- . ↩43908